2025年,中国金融行业站上了从”数字化”迈向”智能化”的关键转折点。银行、保险、证券这类一向以稳健著称的机构,在合规与风控的硬约束之下,对新技术的引入历来审慎;但生成式AI带来的效率跃升与体验重塑,又是任何一家金融机构都不愿错过的红利。行业演进的核心驱动力,已经从最初”要不要用大模型”的试探和观望,转向场景的快速扩张、应用的规模化落地,以及对底层算力、解决方案与合规能力的系统性需求。金融AI云的竞争逻辑由此发生了一次根本性跃迁——从比拼算力”资源供给”维度,转向以”算力底座、平台调度、行业模型与合规可控”为核心的全栈能力竞争。

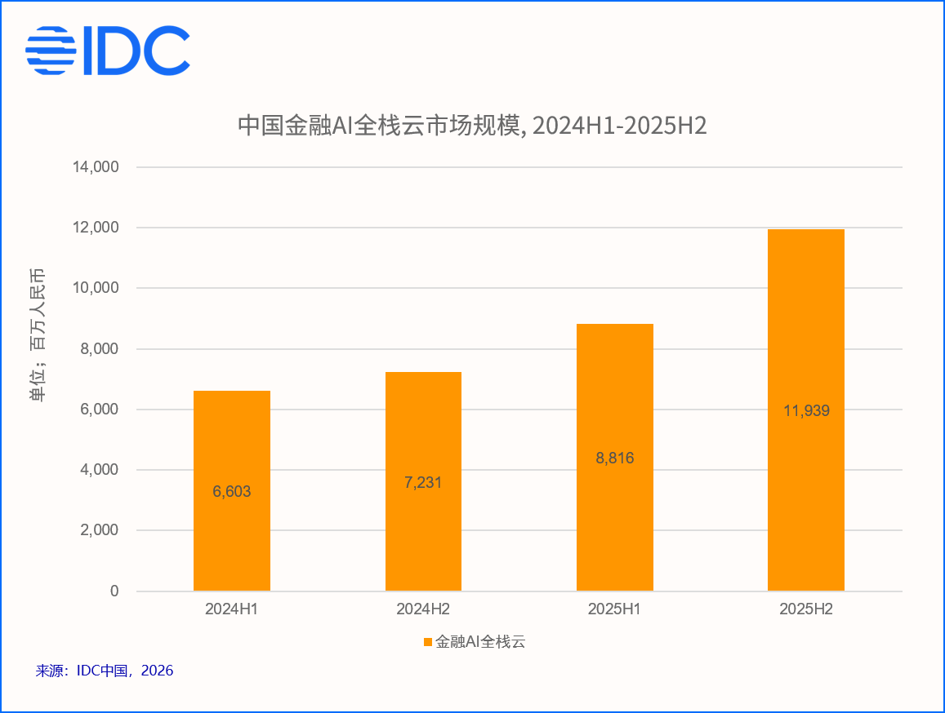
国际数据公司(IDC)最新发布的《中国金融云市场跟踪研究Add-on_AI全栈云》报告首次对中国金融云市场中公有云AI算力服务、私有云软硬件AI基础设施和GenAI解决方案子市场做出全栈式市场营收评估,中国金融AI全栈云市场2025全年市场规模207.6亿人民币,较2024年同比增长50.0%,远超金融云总盘23.9%的同比增速。这个数据对比显示出金融机构对AI相关领域的重视程度不断升级,预算投入持续加码,市场潜力快速兑现。

金融全栈布局下,头部云厂商的五种路径

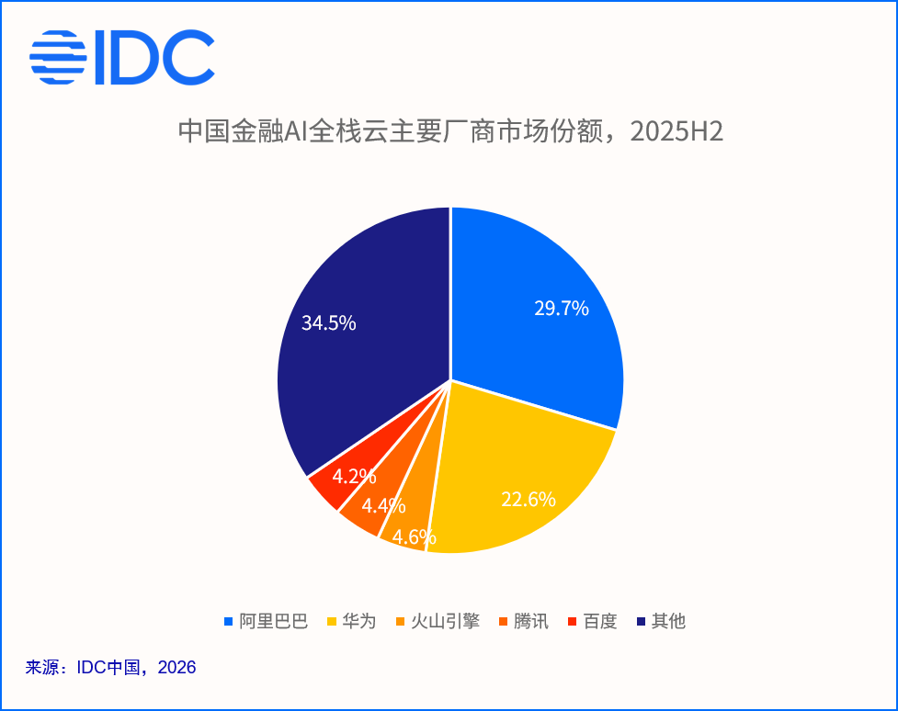
经过几轮市场调整,金融AI全栈云的第一梯队逐渐清晰。五家代表性厂商在算力、平台、模型与应用上的侧重各有不同,拼出一张完整的能力地图。

“公有云算力+私有化交付“双轨并进:代表厂商 阿里云

阿里金融云,在公有云一侧依托灵骏智能计算集群,在大规模算力调度与推理优化上持续投入;金融自主私有云一侧,平头哥自研的真武AI芯片已进入规模化部署阶段,并从2025年下半年开始逐步起量。叠加面向金融场景打磨的通义点金行业大模型,以及可落入客户机房的一体机交付形态,阿里云事实上把”芯片—模型—应用”的链路在金融场景里走通了一遍,并将在2026年持续深耕,加速复制。

软硬协同稳扎稳打:代表厂商 华为云

华为昇腾系列智算服务器,多年来在国产算力替代的进程中扮演压舱石角色。对金融机构而言,华为的吸引力恰恰在于”软硬一体、自主可控”带来的确定性——在数据不出域、供应链安全成为硬约束的当下,一套经过大规模验证的昇腾底座,往往比单纯的性能参数更有说服力。

AI应用和智能体先行:代表厂商 火山引擎

背靠字节跳动内部高并发推理场景的长期锤炼,火山引擎在推理成本控制与资源利用率方面建立了差异化优势,豆包C端的成功也给火山解决方案带来足够的曝光度和品牌效应,豆包大模型与火山方舟平台构成其对外的主要解决方案抓手。在智能营销、智能客服等高频交互场景中,这种”应用先行、智能体多点开花”的策略,更容易让金融客户在数据非敏感领域优先尝到AI红利甜头。

让金融AI“融汇贯通”起来:代表厂商 腾讯云

依托在平台层数据库和大数据产品的行业优势,腾讯云从AI通用大模型到上层AI应用,从平台产品到底层异构算力管理,试图把这条链路做成一个连续整体,而非彼此割裂的模块。对于拥有庞大存量系统、又要稳步引入AI能力的金融客户来说,这种平滑过渡、整体交付的能力,本身就是一种稀缺竞争力。

“芯片+平台”组合拳:代表厂商 百度智能云

昆仑芯P800已完成规模化验证,2025年以来已交付多个万卡集群,并支撑了文心大模型新版本的训练。配合百舸AI计算平台在异构调度上的能力和千帆平台对金融应用场景的支撑,百度为金融客户从模型基础训练到推理开发上线,铺设了一条相对完整的国产化通道。

五家厂商路径不同,指向的判断却高度一致:在金融这样对”稳健”近乎苛求的行业里,单点能力很难构成壁垒,唯有把算力、平台、模型、应用与合规能力打通,才能真正站稳脚跟。

金融ISV服务商的“喜“与“痛“:增量市场背后的挑战

在AI云厂商与金融机构之间,往往活跃着各个子赛道金融ISV服务商的身影。他们既是AI方案的集成者,也是AI应用落地的”最后一公里”。2025年,金融ISV服务商感受到了明显的市场变化,AI市场带来新增营收机会的同时,也带来了全新的机遇和挑战。

一方面,金融AI场景在2025年正式跨过了“项目落地“的门槛,并呈现出明显的量价齐升势头。在传统金融预算大环境整体承压的当下,这样一块实打实的市场增量殊为不易,它意味着新的项目机会、新的合作入口,以及与客户重建深度连接的契机。不过,这份增量需要冷静看待,AI相关收入对整体金融云解决方案营收的直接贡献占比仍然偏小,更多扮演的是”敲门砖”与”引流器”的角色——通过AI项目切入客户、增强黏性,再向定制化开发、平台软件乃至底层基础设施资源的销售导流,而这些方向的受益者往往是云厂商占优。真正的商业价值,可能兑现在AI之外。

另一方面,金融机构对AI方案的选型普遍呈现迷茫状态。用哪家大模型,走开源还是闭源,部署在公有云还是落到本地机房,是否涉及业务系统解耦和微服务改造,数据安全合规如何满足监管要求,未来方案兼容性与可持续性又如何保证——这些问题几乎没有现成经验可以照搬。金融ISV服务商需要陪伴客户共同摸索试错,在反复的POC与调优中消耗大量人力成本。这种”陪跑”固然能加深信任,却也推高了交付成本,挤压了本就不宽裕的利润空间。

IDC市场调研发现,金融ISV AI服务商正从”项目制交付”向”持续运营”转型,从单纯的技术提供者,转变为深度参与客户流程重构的”业务转型伙伴”。金融AI可能对未来ISV服务商竞争格局带来颠覆性变化,金融服务商不仅要懂业务,还要懂AI、养AI、用AI,扛的住长期AI运营的玩家才能在未来竞争中立于不败之地。

IDC洞察:金融AI要以全栈能力和生态协同赢得长期战斗的胜利

对于金融云服务商和云厂商而言,是否全栈式布局已不再是选答题,而是必答题。金融客户要的不是某一颗更快的芯片或某一个更准的模型,而是一套“数据—模型—平台—应用—服务“端到端打通、并能自我迭代和强化的能力体系。在这一点上,自主算力与行业大模型的协同尤为关键,它既回应了自主可控的政策诉求,也构筑起别人难以复制的护城河。与此同时,”合规”应当被前置为产品能力而非事后补丁——数据不出域、决策可追溯、幻觉可约束,在通用市场或许是加分项,在金融市场却是入场券。

随着智能体应用从单点走向全流程,推理调用量将呈指数级放大,按需租赁、弹性扩容与混合部署在未来三到五年内,有望逐步替代传统的重资产采购模式,成为金融AI基础设施建设的新常态。能在保障性能的同时把综合成本压下来的厂商,将在长期竞争中占得先机。

此外,建议金融云厂商加大对金融ISV服务商的支持力度。ISV是云厂商触达金融客户的重要渠道,也是行业Know-How的历史沉淀者,并在AI拓展方面成本承压。云厂商在算力补贴、平台开放、收益合作与人才培养上给予生态伙伴更深层的支持,可加快金融AI整体升级节奏。

金融行业要的,从来不是非此即彼的”创新”或”稳健”,而是两者之间的平衡。能否帮客户既迈得开步子、又站得稳脚跟,正是这场金融AI全栈云竞速中,最终拉开差距的地方。

如需进一步了解IDC相关研究,或就中国金融云AI市场发展趋势进行深入交流,欢迎与IDC联系,获取更多洞察与数据支持。

北京,2026年6月5日——国际数据公司(IDC)最新发布的《2026年第一季度全球手持智能相机市场跟踪报告》显示,2026Q1全球手持智能相机市场出货量达到414万台,同比增长33%。销售额超过105亿元人民币,同比增长20%。IDC预计,至2030年,全球手持智能相机市场规模将会超过4000万台,五年复合增长率接近18%。

2026Q1全球手持智能相机发展状况

  • 运动相机市场:26Q1全球运动相机出货量接近201万台,同比增长39%。平均单价2149人民币,同比下降11%。推动市场高速增长的主升浪来自于大疆和影石爆款明星产品热销,同时上一代产品的强势调价促销也为厂家贡献了良好业绩。大疆和影石出货量市场份额同比攀升13个百分点,老牌厂商GoPro生存空间继续被挤压。从运动相机市场细分品类来看,可拆卸运动相机即“拇指相机”出货量同比增长惊人超过350%,不可拆卸运动相机同比增长16%。
  • 云台相机市场:26Q1全球云台相机出货量同比增长超过18%,平均单价2840人民币,同比下调12.5%。此市场大疆继续保持独占领先优势。手持云台相机市场在产业上下游供给侧和最终用户需求端都保持了高热度,26年将迎来产品突破升级和新竞争厂商出现。
  • 全景相机市场:26Q1全球出货量超过50万台,同比增长高于50%。影石在全景相机领域排名第一且大幅领先,出货量份额接近七成,大疆Osmo360火爆单品保持热度拿下超过两成市场。

2026Q1全球手持智能相机市场主要厂商概况:

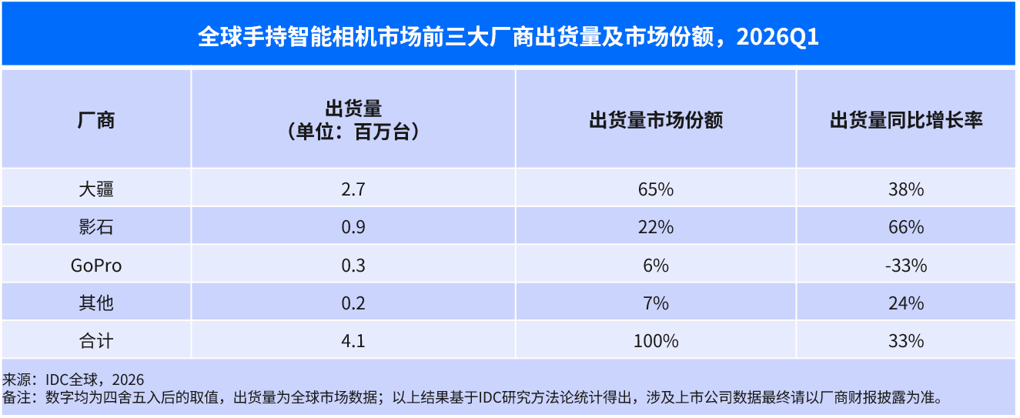
26Q1全球手持智能相机市场,大疆以65%出货量市场份额保持第一,同比增长38%。影石出货量市场份额达到22%,同比增长66%排名第二。GoPro受到大疆和影石的全球激烈竞争出货量同比持续萎缩。

大疆

大疆凭借无人机领域全产业链成功多年积累的硬件核心技术(多轴云台稳定系统,影像及多传感器融合技术,飞行及运动控制系统)向手持智能影像设备迁移,打造高可靠性和易用性的影像产品全系列矩阵。品牌拥有完善供应链体系,成本抗压弹性,议价能力,上游核心部件定制化能力均较强。26Q1云台相机自身出货量占比超过一半,Pocket4新品预售火爆断货,3代产品调价后继续受到市场追捧。不可拆卸运动相机出货量市场份额同比上升3和百分点增长至54%,可拆卸运动相机即“拇指相机”单品Osmo Nano在25年发售后保持热销,26Q1出货量拿下过半市场份额。在全景相机领域,26Q1大疆凭借Osmo360单品赢得22%出货量市场份额占稳这一市场。

影石

26Q1全球出货量接近90万台(结果基于IDC研究方法论统计得出,涉及上市公司数据最终请以厂商财报披露为准)。影石持续加大投入研发资源,凭借在全景相机领域作为全球领军厂商的多年技术积累,已经在差异化应用场景和应用软件方面形成独特优势和壁垒。其系统应用软件在拼接算法,多场景防抖,深度主体追踪以及在AI助手一键剪辑方面获得庞大用户群的广泛认可。影石在全景相机领域虽然遭遇挑战,但26Q1仍旧保持了接近七成出货量市场份额。在不可拆卸运动相机领域,AcePro2街拍套装促销取得成功,出货量市场份额创新高超过17%,同比吃掉7个百分点。在可拆卸运动相机市场,尽管面临强势竞争,产品出货量同比增长翻倍且Go Ultra表现亮眼。此外云台相机高热度新品将在第二季度全球出货也为厂商锚定新的增长点。

GoPro

遭遇中国厂商全球激烈竞争,面临供应链成本上涨,削减库存等多方面压力同比大幅收缩。26Q1全景相机出货量同比跌幅大于运动相机,运动相机内部Lit Hero以及Hero低价老品自身比重增加,整体均价同比下调17%。虽然发布M1系列新一代运动相机以及继续推广全景Max2新品但市场表现有待观察。

IDC分析师洞察与市场未来发展预测:

  1. 手持智能相机从硬件堆叠到全产品矩阵,进一步深度挖掘场景覆盖。回顾手持智能相机发展历程,关键硬件研发诸如大底传感器,可变光圈系统,8K超高分辨率等技术仍旧是推动市场发展的核心因素。从产品端侧看已经由全景相机,不可拆卸运动相机,手持云台相机到可拆卸运动相机形成手持智能影像全产品矩阵。与此同时覆盖用户人群由小众极限运动极大拓展到广大运动爱好者到Vlog创作者和大众记录日常。厂商仍旧致力于深挖用户场景需求乐此不疲。
  2. AI融入手持智能影像终端最终能为用户带来什么价值。目前AI功能主要集中于AI场景深度感知,AI智能降噪,多帧合成算法,暗光画质增强,AI后期智能剪辑成片等功能型应用。AI融入手持智能影像终端的未来愿景是成为智能影像机器人终端的底座和大脑,由被动的影像记录终端成长为基于海量数据采集可以按照用户各种需求主动生成创作内容的超级智能体。
  3. 中国是手持智能相机的第一大市场。从2025年度出货量来看,中国贡献了超过一半的市场份额,26Q1延续了这种趋势且贡献进一步有所加大。除中国外,美国,西欧,亚太区和日本是全球前四大市场。海外市场产品渠道营销是国内厂商投入资源的核心议题之一。
  4. 手持智能相机市场的渗透率仍旧较低,未来增长空间可期。手持智能相机市场无论从产业资本和上下游供给侧还是最终用户消费者层面仍旧保持高热度。无论哪一条细分产品线市场的未来五年复合增长率均高于15%。IDC预计,至2030年,全球手持智能相机市场规模将会超过4000万台,总体复合增长率接近18%。

IDC手持智能相机定义

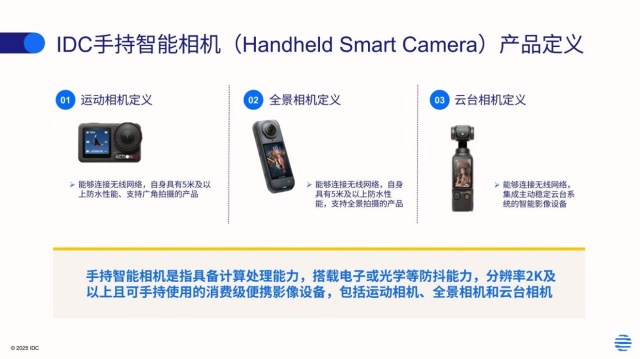
IDC对手持智能相机的定义是指具备计算处理能力,搭载电子或光学等防抖能力,分辨率2K及以上且可手持使用的消费级便携影像设备,包括运动相机(包含可拆卸和不可拆卸运动相机两种形态),全景相机和云台相机。

IDC更多相关详细内容,敬请关注:IDC WW Quarterly Handheld Smart Camera Tracker

请点击此处与我们联系。

Jacky Xue

Jacky Xue - Research Manager

Jacky Xue is a research manager with the Client Systems Research team at IDC China, responsible for projector, IWB and enterprise client devices research and analysis. His responsibilities include tracking the industry data, monitoring the market development, analyzing the future…

Organizations worldwide are failing to deliver cybersecurity metrics that serve their boards, executives, and operational teams, and the emergence of AI has widened that gap significantly. Cyber risk has risen from an operational concern to an existential business risk. Ransomware attacks have shut down companies outright. Regulatory frameworks, including DORA, NIS2, and SEC disclosure rules, now hold boards directly accountable for risk and compliance posture. The stakes have never been higher, yet the tools used to communicate cybersecurity health remain fundamentally misaligned with the audiences that need to act on them.

Just as revenue and expense data flows across every level of an organization, cybersecurity risk intelligence must reach operations, management, and governance audiences, calibrated to each. The message appropriate for a security operations team is not the message appropriate for a board of directors.

More importantly, many CISOs do not know how to communicate with executives and board members, and executives and board members do not know what they want from CISOs. CISOs want to discuss in cybersecurity terms, but executives and board members really only understand business, revenue (dollars), and resilience, and they don’t understand cybersecurity. This data-driven cybersecurity metrics framework was written specifically to deal with that problem in a way that lets the CISO, executives, and board members communicate in a language both understand.

Why cybersecurity metrics are misunderstood

Cybersecurity matured in reverse. Unlike most disciplines that flow from strategy to goals to policies to tactics, cybersecurity built itself from the bottom up: tactics first, strategy last, if ever. The consequences of that legacy persist today:

  • Formal strategy is largely an accumulation of small tactical decisions made over decades, never designed for governance audiences.
  • Boards are routinely presented with operational metrics — firewall blocks, vulnerability counts, patch rates — that were never built for governance consumption.
  • Regulatory pressure is accelerating the problem: governments worldwide now hold executives and boards directly accountable for risk and compliance posture.
  • The result is a persistent, structurally embedded mismatch between what cybersecurity teams can easily produce and what governance audiences actually need.

Why executive and board meetings fail to communicate cyber risk

Boards govern. Executives strategize. Neither runs day-to-day operations. Yet most cybersecurity presentations treat them as if they do:

  • Executives lack deep cybersecurity domain expertise by design; their role is strategic governance, not running a security operations center.
  • When metrics are misaligned, board meetings devolve into data dumps, forcing executives to decode technical minutiae rather than engage in meaningful risk dialogue. A single DLP block statistic can consume an hour of board time with no actionable outcome.
  • CISOs typically rise through technical security leadership, not business management, limiting their experience translating risk into the language of business strategy.
  • Board-level cybersecurity accountability is a relatively recent demand, driven by the ransomware pandemic rather than strategic planning. There is no established playbook; most CISOs learned by trial and error.
  • The result: CISOs default to presenting what they have — operational metrics — and boards are left searching for the risk signal buried in the technical noise.

Why traditional metrics failed everyone

The failure wasn’t malicious. It was structural. Both sides operated in good faith with the wrong tools:

  • Metrics were built from available data, not from audience needs. Current metrics are often fragmented across multiple repositories and formats, making collection laborious and time-consuming.
  • What existed was appropriate for operations management — rarely in a form useful for executive decision-making.
  • Noncompliance rates, firewall blocks, and vulnerability scan results are tactical measures with no clear call to action at the executive level.
  • Management asked, “Are we OK?” and received patching statistics in response: a fundamental mismatch between the question asked and the answer provided.
  • Tactical metrics aid day-to-day program management but lack the context and comprehensiveness required for strategic leadership. Without a centralized intelligence platform, this gap cannot be closed.

How AI has changed the metrics imperative

AI has added two urgent, distinct dimensions to an already unsolved problem.

Offensive: AI as an adversarial weapon

  • Threat actors are weaponizing AI to generate convincing phishing campaigns at unprecedented scale.
  • Deepfake audio and video are being used to impersonate executives and manipulate internal decision-making.
  • AI accelerates vulnerability discovery, exploit development, and evasion of traditional detection controls.
  • The net effect: faster, higher-volume, more sophisticated attacks, with compressed detection and response windows.

Defensive: Ungoverned internal AI deployments

  • Organizations are embedding AI into products, services, and operational decisions at a pace that far outstrips governance and oversight controls.
  • Shadow AI, agentic AI, and SaaS-embedded AI are widely deployed and largely untracked.
  • This creates a new class of enterprise risk: model failures, hallucinated outputs influencing strategy, customer harm, and regulatory exposure.
  • Without AI-focused metrics at every organizational level, the gap between the questions executives are asking and the answers cybersecurity leaders can provide will only widen.

The qualities of data-driven metrics

Data-driven metrics must serve specific audiences, telling a coherent story calibrated to each stakeholder’s role, accountability, and risk exposure. Three tiers are required:

Governance (Board/C-Suite)Strategic risk oversight, compliance posture, AI governance status. 6–10 high-signal metrics organized across 4 IDC-defined categories.
Managerial (C-Suite/LOB/Ops Management) Program health, AI incident trends, shadow AI exposure, regulatory compliance progress. Both strategic and tactical in nature.
Operational (CISO/Functional Teams)Day-to-day control effectiveness, AI attack surface, shadow AI detection, hallucination monitoring, data protection. Essential for execution teams; too granular for boards.

Effective data-driven metrics share these qualities:

  • Audience-specific: Each tier receives only what is relevant to its function, accountability, and decision-making authority.
  • Outcome-driven: They measure progress toward defined business objectives, not activity volume.
  • Actionable: Every metric carries an implicit or explicit call to action, enabling informed, confident decisions.
  • Contextual: Risk is framed in financial, operational, or reputational terms, not technical jargon.
  • AI-inclusive: Every tier must now incorporate AI-specific risk intelligence alongside traditional cybersecurity metrics.

Elements to consider in crafting metrics

Building metrics that work requires a structured, iterative process anchored in business context, not available data.

1. Understand the risks

  • Begin with the business: define key functions, processes, and associated risks before mapping them to cybersecurity priorities.
  • Engage stakeholders from IT, audit, legal, risk, compliance, BISOs, and senior executives to build consensus around what matters most.
  • Incorporate AI as both an internal operational risk (from the organization’s own deployments) and an external threat vector.
  • Expand the stakeholder group to include AI governance officers, AI product owners, and legal or privacy counsel with AI expertise.

2. Align data collection

  • Shape metrics collection around agreed risks, automating data sources through GRC platforms capable of generating audience-specific intelligence.
  • Treat AI systems as first-class data sources: model inventories, output logs, decision audit trails, and third-party AI component registries are required inputs alongside traditional telemetry.

3. Analyze the Data

  • Use automation and AI to analyze large volumes of contextual intelligence against the risk register, surfacing asset ownership gaps, CMDB inaccuracies, and emerging risks.
  • AI-generated analyses must be subject to human validation before informing decisions.
  • AI output accuracy should itself become a tracked and reported metric.

4. Interpret Results in Business Terms

  • Outcomes must be specific, measurable, and meaningful — for example, a DLP implementation should show users changing behavior, exfiltration declining, and residual risk being quantified.
  • When AI systems produce outcomes, interpretive frameworks must distinguish human-driven from AI-driven results and assess accuracy and fairness, not just control effectiveness.
  • AI-generated recommendations must never be treated as equivalent to validated analyst conclusions.

5. Consider the stakeholders

  • Manufacturing LOBs: focused on process uptime and network segmentation risks.
  • eCommerce LOBs: focused on application security and architecture risks.
  • AI-deploying LOBs: carry distinct AI-related cybersecurity risks requiring specific communication.
  • Expand the model to include AI product owners, data scientists, and AI governance officers wherever AI intersects cybersecurity risk.

6. Empower decision-making and monitor continuously

  • Cybersecurity leaders own the recommendation; the risk decision belongs to the business owner accountable for it. Their role is to build a story that lets decision owners act with confidence.
  • Monitor for model drift; schedule regular AI system reevaluation and retraining.
  • Continuously retire irrelevant risks and elevate newly emerging ones, including those introduced by evolving AI deployments.
  • Embed AI governance explicitly: model approval policies, mandatory preproduction risk assessments, human review standards for high-risk AI decisions, and AI incident management procedures are all required.

What is needed for data-driven metrics

Effective data-driven metrics communicate risk likelihood versus business impact. They go beyond statistics to deliver actionable insights supporting both strategic and tactical decision-making. Achieving this requires:

  • A centralized intelligence repository consolidating contextual business, IT, and cybersecurity data, including AI-specific signals, into a single, consistent source of truth.
  • Three metric tiers (governance, managerial, and operational) generated consistently over time from that single source.
  • AI-specific metrics at every tier: shadow AI detection, AI regulatory compliance posture, agentic AI governance, model IP protection, SaaS-embedded AI risk, and AI output integrity.
  • Automation, machine learning, orchestration, and AI to generate an ever-evolving set of metrics and adjacent risk insights.
  • Audience-specific dashboarding and stakeholder messaging that translates technical cybersecurity data into business risk language, calibrated to the level of accountability and required response.

The role of GRC platforms and intelligence fabric

Modern GRC platforms are uniquely positioned to close the metrics gap. By consolidating internal and external business, IT, and cybersecurity intelligence into a single repository, enhanced through automation, machine learning, and AI, they power consistent, audience-specific metrics at scale.

The intelligence fabric is the contextual data layer at the core of a modern GRC platform. It must enrich the risk register with:

  • Newly discovered assets and their sensitivity classifications
  • Potential data and asset ownership
  • Estimated monetary impact of risks and compliance issues
  • Contextual interpretation of risks against organizational policies

The fabric must now extend to AI-specific intelligence, organized by metric type so each audience sees the right signal at the right altitude:

1. Cybersecurity risk posture2. Compliance posture3. Program outcomes4. AI governance status

This includes:

  • AI model inventories and ownership records
  • Shadow AI detection signals
  • AI output logs and decision audit trails
  • AI regulatory compliance mapping (EU AI Act, NIST AI RMF, and sector-specific requirements)

What this enables:

  • Single source of truth: Centralized GRC intelligence across cybersecurity, IT, and business functions.
  • Audience-specific dashboards: SOC views for operational teams; risk posture views for executives and boards.
  • Outcome-driven metrics: Actionable statistics, trends, and risk-driven insights tied to business objectives.
  • Targeted stakeholder messaging: Calibrated by audience and required response — for-your-information only, executive risk-based decision required, or action needed (e.g., budget approval).
  • Reduced human bias: AI-assisted analysis increases consistency and accuracy across the metrics program.

Advice for technology buyers and suppliers

For the technology buyer

A passing awareness of cybersecurity posture is no longer acceptable at any level of leadership. Buyers should:

  • Partner with a qualified cybersecurity GRC software provider experienced in collecting, analyzing, and generating audience-appropriate metrics aligned to this three-tier framework.
  • Ensure the platform consolidates contextual business, IT, and cybersecurity intelligence, internal and external, into a robust, integrated repository.
  • Demand at least three levels of metrics: governance (strategic), managerial (strategic and tactical), and operational (tactical), generated consistently over time from a single source.
  • Require AI-specific risk metrics across all three tiers: shadow AI detection, AI regulatory compliance posture, agentic AI governance, model IP protection, and SaaS-embedded AI risk.
  • Insist on automation, machine learning, and orchestration to generate an evolving metrics program that stays ahead of the threat and regulatory landscape.
  • Boards must be able to confirm: Are AI systems governed? Is AI risk being measured? Are AI incidents — regulatory actions, customer harm, reputational damage — being proactively managed and reported?

For the technology supplier and services provider

The market opportunity is clear, immediate, and structurally durable. Organizations at every level need current, audience-appropriate visibility into cybersecurity risk and compliance posture, and most lack the platforms, skills, and frameworks to deliver it. Suppliers should:

  • Build or extend GRC platforms with a consolidated intelligence repository that centralizes business, IT, and cybersecurity data to power consistent, audience-specific metrics at scale.
  • Deliver all three metric tiers (governance, managerial, and operational) from a single consolidated intelligence source. Providers who can do this address a gap most organizations cannot close without external platform support.
  • Invest in audience-specific dashboarding that translates technical cybersecurity data into business risk language, designed for boards, executives, and operational teams alike.
  • Incorporate AI governance metrics: shadow AI detection, AI regulatory compliance posture, agentic AI risk, and model IP protection across all three audience tiers.
  • Develop consulting and managed service offerings that help customers build data-driven, AI-inclusive metrics programs and bridge the business acumen gap most cybersecurity teams face.
  • Providers who help CISOs speak the board’s language, translating cyber-risk into business risk, will earn lasting customer loyalty and reduce competitive displacement risk.

“The cybersecurity metrics market is at an inflection point. Customers are being held accountable for AI risks they cannot yet measure, and boards are demanding business risk context that most security tools still cannot deliver. Technology and service providers that step into this gap, with consolidated intelligence platforms, audience-specific metrics, and AI governance capabilities, will define the next generation of cybersecurity and GRC market leadership.” — Philip D. Harris, Research Director, Governance, Risk, and Compliance Solutions, IDC

Philip D. Harris, CISSP, CCSK

Philip D. Harris, CISSP, CCSK - Research Director, Governance, Risk, and Compliance (GRC) Solutions

Phil Harris is Research Director for GRC Solutions at IDC, where he develops and promotes IDC's point of view on risk, advisory, privacy, and compliance services and software. He conducts research on business strategies and the impact of relevant offerings…

For years, small and medium-sized businesses took the same approach to AI: watch, wait, and let someone else absorb the cost of a failed experiment. In 2026, that calculus has changed. IDC’s Katie Evans, Senior Director of Worldwide Small and Medium Business Research, sat down to share what the latest data, drawn from more than 2,700 IT decision-makers across 23 countries, reveals about where SMBs are now, what’s driving the shift, and what any SMB owner should do before making their first AI investment.

The “fast follower” strategy paid off

Three years ago, IDC research consistently surfaced a pattern in how SMBs talked about AI. They weren’t early adopters. They were deliberate holdouts, not because they didn’t see the opportunity, but because the risk calculus didn’t work in their favor.

“They would say, ‘I want to be a fast follower,'” Evans explains. “We don’t have the budget for a failed AI experiment.”

That instinct turned out to be sound strategy. While large enterprises absorbed the costs of early-stage AI experiments (the failed pilots, the shaky implementations, the expensive custom builds), SMBs watched and learned. By the time vendors began packaging AI into the tools SMBs were already using, those businesses knew exactly what they were looking for.

IDC’s 2025 survey captured the inflection: in 2024, AI ranked third among forward-looking technology priorities for SMBs. By 2025, it had jumped to number one. The share of SMBs not using AI at all dropped from 11.2% to 6.3% in a single year.

The proof arrived. The fast followers moved. And the first thing most of them did was look inward.

What SMBs are actually using AI for

The businesses that have moved fastest share a common starting point: they looked at their own operations before they looked at any vendor. The number one current AI use case for SMBs worldwide reflects that instinct: generative AI for content creation. That includes marketing copy, internal documentation, customer communications, and code. It’s the entry point, and it’s well-established.

But the picture is expanding. IDC’s research shows SMBs are moving beyond isolated productivity tools into more operational territory. Digital assistants to manage tasks are rising fast, particularly among smaller businesses with lean staff. Robotic process automation (RPA) is growing. And the next wave, agentic AI, which can take autonomous action on behalf of a business, is already on the planning horizon.

Evans points to a practical lens for SMBs trying to decide where AI fits in their business: look at where work is piling up.

“Look for high-volume, repetitive tasks: invoice processing, data entry, inventory tagging, moving figures from PDFs to spreadsheets,” she says. “If those tasks are increasing as your business grows, you’re building a bottleneck. That’s where AI can take over.”

There’s a retention argument here too. SMBs, which often can’t match the compensation packages of larger competitors, can use AI to remove the dull, error-prone work that drives good employees out the door. “If you can make their workplace more fulfilling by leaning into technology,” Evans notes, “it really helps with retention.”

The goal, she is clear, isn’t to save a few minutes per task. It’s to increase revenue per employee.

But knowing where AI can help is only half the equation. The other half is finding a solution that a lean, non-technical team can actually use.

Why embedded AI is winning

Here is the constraint that shapes everything else for SMBs: 40% of the nearly 3,000 SMBs IDC surveyed do not have a single full-time IT employee in-house. That number has held steady for several years, even as SMB technology budgets have grown. A third of SMBs cite lack of IT staff as a top challenge. Another third flag user adoption as a major obstacle.

These numbers explain why standalone AI point solutions are losing to embedded ones.

“SMBs that are seeing real results from AI are not adding it as a separate point solution,” Evans says. “They’re turning on AI capabilities that are already inside the platforms they use every day: their CRM, their ERP, their accounting system.”

The logic is straightforward: no new interface to learn, no separate implementation cycle, no change management burden. The vendor is already known and trusted. The AI feature is just a feature that gets switched on.

Vendors have started meeting SMBs where they are. IDC’s 2026 market data shows a clear shift toward GenAI as the top forward-looking technology priority, overtaking traditional AI and process automation. And increasingly, vendors are embedding those capabilities directly into their products: consumer-grade interfaces, guided chat prompts, no-code and low-code options, designed for non-technical staff with no IT backup.

“As easy as you can make AI for your employees to use is the key,” Evans says. “Think of it like an app on your phone. Something that just works.”

Vendors are getting there. But two obstacles are slowing the journey for SMBs that are ready to move.

The barriers that still need solving

Unpredictable pricing is the first. When an SMB implements an AI capability, sees it working, and then watches its bill triple because it crossed an invisible usage tier, trust breaks down fast. Evans puts it plainly: “SMBs have tighter budgets. Unpredictable costs are a big red flag.”

What SMBs want is transparency: credit-based models that let them control usage, freemium options that allow experimentation before commitment, and clear communication about what each pricing tier actually means. The lowest price isn’t always the winner. Predictable pricing, where the total cost of ownership is legible, is.

Security is the other major barrier, and it’s gotten bigger, not smaller. IDC’s 2026 data found that implementing new technology securely is the number one challenge SMBs name when asked what’s standing between them and their business priorities. It ranked above lack of budget, above user adoption, above lack of IT staff.

“AI is a data guzzler,” Evans says. “It constantly needs new, fresh data to train its models. So SMBs are asking: where is the data coming from? Are you using my customers’ data? How long is it being stored?”

The ask from SMBs is clear: security and compliance built in, not bolted on. A business with no cybersecurity expert on staff needs its vendor to handle that layer. And for an SMB still building consumer trust and brand reputation, a breach isn’t just an operational disruption. It’s potentially an existential one.

IDC forecasts that 50% of SMBs will increase security spending over the next 12 months. For tech suppliers, that is signal: security credibility is a sales requirement, not a feature differentiator.

For SMB owners, it is a checklist item. Before signing with any AI vendor, ask how they handle your data, where it is stored, and what compliance frameworks they operate under. Pricing and ease of use matter. So does knowing your customers’ information is protected. With those boxes checked, the path forward is clearer than it has ever been.

What smart SMBs should do next

The data is there. The vendor options are growing. The path to AI adoption for SMBs isn’t as steep as it was three years ago. But it still requires some deliberate homework.

Evans’s advice, distilled from conversations with hundreds of SMBs and thousands of data points: start with an operational audit. Before evaluating any specific AI tool, walk your own business and look for the work that consistently slows you down. High-volume, repetitive tasks. Processes that pile up as you grow. Places where a lean staff is spending hours on work that produces no strategic value.

Then look for AI that is embedded in platforms you already trust, built for non-technical users, and priced transparently. Any vendor worth considering should be able to show you measurable outcomes, not just capabilities.

“Many solutions that are a good fit for your business are out there,” Evans says. “But you need to find something that meets your unique needs. Do your homework.”

IDC predicts that by 2027, driven by the widespread adoption of AI and agentic AI, 70% of medium-sized businesses will achieve digital payback at twice the rate of previous technology cycles. That’s not a forecast about large enterprises with armies of engineers. That’s a forecast about companies like yours.

The window the fast followers waited for is open. The question now is how confidently you walk through it.

Christina Cardoza - Content Marketing Manager - IDC

Christina Cardoza is a Content Marketing Manager at IDC, where she specializes in brand content and social media strategy. With a background in journalism and editorial leadership, she has a proven ability to transform complex technology topics into clear, actionable insights.

Most AI intelligence platforms are built for the general case. Ask them about cloud infrastructure spending trends, managed services growth, or competitive positioning in a vendor landscape, and they’ll produce something fast, sourced, and useful. 

Now ask them something specific to you. What does this market data mean for a company operating across three distinct verticals with no direct peer set? How does this vendor analysis map against the internal roadmap we’ve already committed to? What’s the right staffing model for an organization at our scale, in our geography, with our constraints? 

That’s where most platforms go quiet. Or give you a generic answer dressed up as a tailored one. 

Two questions are buried in that problem, and they’re worth separating. The first is whether an AI intelligence platform can meet you where you are, understanding your context, your data, your priorities, rather than handing you a market-wide answer and leaving the translation work to you. The second is what happens to your strategy once you’ve shared it. When you bring your internal documents, your roadmaps, your competitive thinking into an AI session, where does that information go? 

These aren’t hypothetical concerns. According to IDC’s Future Enterprise Resiliency & Spending Survey, more than three-quarters of AI projects fail to move from proof of concept to production. The most cited barriers aren’t technical. They’re trust-related: 27% of organizations cite challenges protecting against sensitive data exposure, and 23% report inadequate data governance as a blocker. In IDC’s Enterprise Intelligence Services Survey, security, privacy, and governance concerns ranked as the single most common challenge for buyers adopting AI-driven intelligence solutions, ahead of budget, skills, and technical integration. 

The platforms aren’t failing because AI doesn’t work. They’re failing because organizations can’t answer two basic questions before they fully commit: 

Does this platform understand my situation?

Is my strategy safe here?

IDC Quanta, IDC’s AI platform built on 60 years of proprietary research, is built around both questions. The Contextual and Secure pillars aren’t marketing language. They’re specific product commitments backed by real mechanics. A few organizations that have already been living with them offer a clearer picture of what those commitments mean in practice. 

How contextual AI intelligence adapts to your business, not the market average 

Phillip Langeberg leads technology for The Resorts Companies, a 100% employee-owned Virginia-based group operating across hospitality, real estate, and recreation. Massanutten Resort alone spans 6,000 acres and 2,500 accommodations, with a waterpark, a ski mountain, golf courses, and a 55+ residential community under development. 

There is no standard industry benchmark for that. 

When Langeberg went looking for intelligence to inform vendor decisions, staffing models, and technology roadmaps, he wasn’t operating in a category where peer data arrived pre-packaged. Hospitality benchmarks didn’t capture the complexity of real estate. Real estate data missed the recreation dimension. Manufacturing comparisons were close in some ways and irrelevant in others. 

What he needed wasn’t a faster way to retrieve a generic market answer. He needed a platform that could take his context, his organizational structure, his operational specifics, his ongoing priorities, and benchmark it against IDC research in a way that produced something actually applicable. 

That’s the Contextual pillar. It is a specific product capability, not a marketing shorthand for personalization. You bring your own documents, data, and history into the intelligence session and query them alongside IDC’s proprietary research. The context persists across sessions. You’re not re-briefing the platform every time you return. It accumulates what it knows about your situation and applies it to every answer. 

For Langeberg, that meant analyst conversations and IDC Roundtables that compared his operation with peers across water treatment, manufacturing, and other adjacent industries, not because those were his competitors, but because they operated at a comparable level of complexity. Quanta extended that same principle into a platform: the ability to bring his situation to the intelligence, rather than extracting generic intelligence and hoping it applied. 

“When I walk into that moment where I’m not sure where I need to be on something, I know that IDC is there as a partner — through their research, the AI platform, the analysts — to help us plot the right course.” — Phillip Langeberg, CTO, The Resorts Companies

Market intelligence that knows your business isn’t a luxury for complex operators. It’s the difference between a useful answer and a generic one. 

Why AI research platforms must protect your strategic data 

Eric Walk leads AI data platforms at Perficient, a global technology consultancy with more than 7,000 advisors, engineers, and designers serving over 300 Fortune 500 clients. Perficient’s value proposition is straightforward: help organizations apply emerging technology effectively, and stand behind the advice with enough confidence to stake their reputation on it. 

That proposition depends entirely on the quality of the intelligence that feeds it. 

“You can open up the world and have AI crawl the internet and look at any source of information, but you’re going to get results that reflect the internet. It’s critical for us to ensure we have trusted inputs to produce trusted outputs.” — Eric Walk, VP AI Data Platforms, Perficient

There’s a second-order version of the same problem that gets less attention. When a consultancy brings internal client context, competitive analysis, strategic positioning documents, and roadmap data into an AI research session, the question isn’t just whether the output is accurate. It’s whether the inputs stay contained. 

Most enterprise AI tools don’t give a clean answer to that question. They say things like “we take privacy seriously” and point to terms of service. That’s not the same as a specific architectural commitment. 

The Secure pillar is the specific commitment. Your queries, documents, and outputs live in a private, isolated workspace: not shared with other users, not visible across sessions, not accessible to anyone outside your organization. IDC never uses what you bring into the platform to train its models. Every user is token-isolated. Documents are automatically deleted after 90 days. The platform uses AES-256 encryption, holds SOC 2 Type II certification, and supports enterprise SSO and SAML authentication in general availability. 

That is not reassurance language. It’s architecture. And for a firm like Perficient, where the advice is the product and the advice depends on thinking that can’t afford to leak, the architecture is the point. 

As Jennifer Glenn, IDC Research Director for Information and Data Security, has noted: “AI is only as trustworthy as the data it consumes.” The Secure pillar ensures that the data you bring to that exchange stays yours, every session. 

How contextual and secure work together for enterprise AI adoption 

The sales conversation around IDC Quanta deliberately distinguishes between audiences. For smaller, growth-stage organizations, the most immediate value tends to be Embedded (intelligence delivered without a new tool to learn) and Rigorous (sourced, defensible answers that hold up in front of leadership). Those are the two concerns that surface fastest when teams are lean and can’t absorb errors. 

For larger, more complex organizations, the ones operating at scale with complex internal data, real data governance stakes, and strategy that competes in sophisticated markets, the conversation starts with Contextual and Secure. 

The reason is sequential. You don’t bring your internal roadmap, your competitive intelligence, your client data into an AI platform until you know two things: that the platform will calibrate its answers to your situation rather than the generic market, and that what you share won’t find its way somewhere it shouldn’t. Contextual answers the first. Secure answers the second. 

For an organization like Kyndryl, which spun out of IBM in 2021 as one of the world’s largest managed service providers with 80,000 employees and an analyst relations function serving hundreds of internal stakeholders, the ability to surface IDC research interactively transformed a function that had been bottlenecked by synthesis time. Weeks of research became minutes of conversation. 

But the precondition for that kind of organizational adoption is exactly the trust that Contextual and Secure establish: strategy, product, finance, and sales teams all querying the same platform, knowing their context is understood and their inputs don’t leave the room. 

What to ask before adopting an enterprise AI intelligence platform 

Most organizations ask one due diligence question before adopting an AI intelligence platform: Does it have the data I need? That’s table stakes. IDC Quanta’s foundation is 60 years of proprietary research, 1,300+ analysts across 110+ countries, and 6,000 documents published annually. The data is there. 

The questions most organizations skip are the ones that determine whether an AI platform actually becomes part of how decisions are made, rather than something that gets evaluated, approved, partially adopted, and quietly abandoned when the answers don’t quite fit. 

Does it understand my business well enough to give me an answer I can use?

Can I trust it with the internal context I’d need to share to make that happen?

Contextual and Secure exist because those questions have a right answer. Getting that answer right is what separates an AI intelligence platform that changes how your organization operates from one that sits alongside it. 

Ryan Smith - Content Marketing Director - IDC

Ryan Smith is the Director of Content Marketing at IDC, where he leads brand-level content and social media strategy, aligning research insights with compelling storytelling to engage technology decision-makers. With a background in both IT and marketing, Ryan brings a unique blend of technical understanding and creative strategy to his work. He’s also a seasoned storyteller, speaker, and podcast host who believes the right message, told the right way, can drive both trust and transformation.

2026年初頭、半導体エコシステムの多くの関係者は、状況が緩和されることを期待していた。新たなファブ設備の稼働が始まり、消費者需要は落ち着き、AIインフラの拡大もいずれ一服すると見られていた。しかし、その転換点は訪れていない。むしろ、課題は積み重なるばかりだ。

メモリ市場は2027年まで逼迫し続けるのか?

メモリ市場は2026年に入っても強い価格上昇の勢いを維持しており、その流れは止まっていない。サーバー需要は供給の追いつかないペースで成長を続けている。スマートフォンやPCといった消費者向けセグメントでは、部品表(BOM)コストの上昇がデバイスの製品経済性を根本から変えつつある。そして、AIインフラの拡大は正常化するどころか、メモリ業界がこれまでに経験したことのない需要プロファイルを生み出し続けている。

期待されていた緩和が訪れないのは、逼迫を引き起こす力が解消されていないからだ。それらは複合的に積み重なっている。

メモリ不足は構造的なものか、それとも循環的なものか?

これが最も重要な問いであり、調達から設備投資(capex)、製品ロードマップに至るまで、あらゆる意思決定に関わる答えだ。

メモリはもはや景気循環型のコモディティではない。戦略的なインフラ投入物へと変貌を遂げた。

数十年にわたり、半導体業界は一定のリズムで動いてきた。需要が急増し、価格が急騰し、供給が追いつき、価格が落ち着く。苦痛を伴うが、予測可能なサイクルだ。しかし今、データが示しているのはそれとは異なる状況だ。需要の構造そのものが根本的にシフトしている。季節性やアップグレードサイクルが行動を規定する消費者向けエレクトロニクスから離れ、四半期ごとに需要が正常化することのないAIのトレーニングおよび推論インフラへと向かっている。需要は積み重なる。デプロイされた推論ワークロードはそれぞれ、次のワークロードが積み上がるベースラインを形成する。

高帯域幅メモリ(HBM)、高密度DRAM、エンタープライズグレードのNANDは、もはや標準的な部品と同じように価格設定や割り当てがされていない。供給契約は長期化し、アロケーションはより厳格になり、供給を確保した企業とそうでない企業の差は拡大している。主要なメモリメーカーは公式のガイダンスで明確に述べている。逼迫した状況は短期的な異常ではないと。これはアナリストの予測ではなく、市場そのものが発しているメッセージだ。今後の計画を見直すべき時が来ている。

2027年まで続くメモリ逼迫を引き起こしているものは何か?

需要サイドでは、AIインフラが最大の牽引役となっている。GPUサーバーは、供給が均衡を取り戻す前にメモリ容量を吸収するペースで拡大している。かつてはトレーニングより軽いと考えられていた推論ワークロードも、特に企業がパイロットから本番環境へ移行するにつれ、大規模では同様にメモリを大量に消費することが明らかになっている。ハイエンドスマートフォンやAI PCにおけるオンデバイスAIも、データセンター需要の上に分散型の需要レイヤーを加えている。

供給サイドでは、状況は逼迫というより、むしろコントロールされている。主要なメモリメーカーは過去のサイクルから教訓を得ている。レガシー製品よりも先端ノードとHBMを優先し、ビット出力を慎重に管理し、生産量拡大を競うのではなく、希少性を反映した価格設定を行うという意図的な設備規律を実践している。新たなファブは稼働しつつあるが、リードタイムは長く、中国の主要メーカーに影響を与える技術規制を含む地政学的要因が、グローバルな供給計算に重大な不確実性をもたらしている。

その結果、供給が存在しないのではなく、管理されている市場が生まれている。そして、その管理の恩恵を受けているプレイヤーは均等ではない。

半導体業界が注目すべき5つの問い

以下は、私が最も注意深く見ているシグナルだ。メモリメーカー、OEM、システムインテグレーター、ディストリビューター、そして世界中の金融コミュニティにとって関連性が高い。

1. 競争が激化する中、HBMのアロケーションはどのように変化するか? HBMは最も逼迫しており、最も高い価値を持つDRAMセグメントだ。より多くのメーカーがHBM製造に参入し、AIチップアーキテクトがアロケーションを競う中で、価格と可用性はどちらの方向にも急速に変化する可能性がある。誰がデザインウィンを獲得し、どのようなタイムラインで進むかを注視することが重要だ。

2. 消費者セグメントはいつ、どのような条件で回復するか? スマートフォンとPCはともに2026年に深刻なBOM圧力にさらされている。問題は単に出荷量がいつ回復するかではない。本当の問いは、手頃なデバイスの製品経済性が構造的に高いメモリコストのもとで再構築できるかどうか、あるいは製品ミックスと平均販売価格(ASP)が恒久的に上方シフトするかどうかだ。

3. 中国の実効的なメモリ供給能力はどの程度か? YMTCとCXMTは2026年に重要な生産マイルストーンに達しつつあるが、技術規制によりノードアクセスは引き続き制限されている。これがグローバルなNANDおよびDRAM供給にどのように影響するか、またバリューチェーン全体のプレイヤーにどのような機会やリスクをもたらすかは、依然として流動的で注視が必要だ。

4. OEMや調達チームはソーシング戦略をどのように適応させているか? スポット購入や短期契約のモデルはますます機能しなくなっている。あらゆる業界で、バイヤーは長期契約、デュアルソーシング、メモリ依存リスクを低減する設計上の選択を再考している。誰が適応し、誰がそうでないかが、条件の変化に伴う競争上のポジショニングを決定することになる。

5. DRAMとNANDの価格軌道は今後どうなるか? 価格はこの18カ月の大部分において一方向に動き続けてきた。その勢いを生み出した条件は依然として大部分が維持されているが、永続はしない。何が反転のトリガーになるか、どのくらいの速さで動くか、そしてどのセグメントが最もリスクにさらされているかを理解することは、今日の資本配分や在庫の意思決定を行う全ての人にとって不可欠だ。

現在のメモリ市場に関するよくある質問

メモリチップ不足の原因は何か? 主な要因は、GPU サーバー構成における HBM と高密度 DRAM に対する AI インフラ需要が、メーカーの設備拡大のペースを上回って成長していることだ。これに加え、先端ノードと収益性を優先する主要メーカーによる意図的な供給規律が重なっている。

2027年にメモリ価格は下がるか? 現在の分析に基づくと、主要セグメントにおける需給不均衡は2027年以降も持続する見込みだ。持続的な価格上昇圧力をもたらした条件は依然として概ね維持されている。2030年までの価格軌道を含む詳細な予測とシナリオ分析については、7月8日のIDCメモリ市場アウトルック・ウェビナーで発表する予定だ。

HBMとは何か、なぜメモリ市場にとって重要なのか? 高帯域幅メモリ(HBM)は、主にAIアクセラレーターやGPUシステムで使用される高性能DRAMインターフェースだ。現在のメモリ市場において最も逼迫し、最も高い価値を持つセグメントの一つであり、需要はAIのトレーニングおよび推論インフラによって牽引されている。HBMの容量制約はAIコンピューティングシステムの可用性と価格設定に直接影響を与え、より広いメモリ市場の見通しを測る指標となっている。

7月8日、全体像をご覧ください

7月8日午後2時(SGT)のIDCメモリ市場アウトルック・ウェビナーで、上記の全ての問いに対するIDCの詳細なデータドリブンな見解をお伝えする。

IDCの信頼できるテクノロジーインテリジェンスと2030年までの世界メモリ需給予測を基に、DRAM、NAND、HBMの価格動向、需給不均衡の今後の推移、そして2026年後半から今後10年にわたるバリューチェーンの各セグメントのシナリオをお伝えする。

メモリが今日のビジネスにおける制約となっているならば、あるいは従来のやり方が通用しなくなった市場で自信を持って次の一手を探しているならば、ぜひご参加いただきたい。

今すぐ登録:2026年7月8日 | 午後2時(シンガポール時間)

*本記事は、2026年6月22日に掲載された英語版ブログ記事の日本語訳です。原文は以下よりご確認いただけます。https://bit.ly/4asfib1

Soo Kyoum Kim - Associate Program Vice President, Semiconductors and Enabling Technologies - IDC

Soo Kyoum Kim is Associate Vice President within IDC’s Enterprise Infrastructure global research domain. He focuses on DRAM and NAND Memory as part of the Semiconductors and Enabling Technologies subdomain. Soo Kyoum’s research covers demand and supply analysis for DRAM and NAND, memory consumption for server workloads, next generation memory, and emerging memory markets. He provides insights on the demand and supply dynamics in industry, chip pricing, competitor, and fab capacity. He also covers the dedicated foundry market.

As AI adoption accelerates across enterprises, organizations are learning a hard lesson: bolt-on training tied to individual use cases just won’t cut it. To win, organizations must treat AI literacy as a strategic enterprise-wide capability.

That means embedding AI training in culture, governance structures, onboarding and performance expectations. It also means moving beyond the pilot mindset and building systematic programs with sustained executive backing, role-based curricula and real change management discipline.

IDC research reveals the gap.

Meanwhile, companies charge on with their AI plans. That leaves a lot of employees improvising on the very tools their companies are betting on. Good intentions can’t substitute for real, organization-wide knowledge about what AI can and can’t do, and how to make the best use of it.

As the recent IDC study on Foundation AI literacy, the baseline competencies every employee needs to use AI responsibly and effectively, makes clear: AI training must be for everyone, not just technical teams. Scaling means moving past pilot- and use-case-specific training to a tiered curriculum that reaches the whole workforce. Start with the basics for all employees: what AI is and is not, responsible-use guidelines and the key risks, including bias, hallucinations, privacy and data leakage. Then show the upside, the opportunities for augmentation and productivity. Most employees arrive without a structured academic grounding in AI, so accessible, role-aware pathways matter.

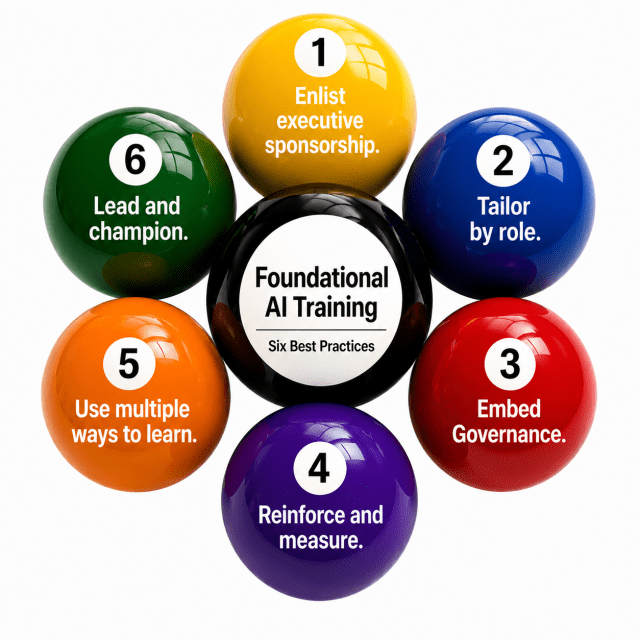
Here are six practices that distinguish successful AI initiatives at global organizations.

1. Enlist executive sponsorship

Successful programs begin with visible, sustained support from senior leadership. When a CEO or COO clearly signals that responsible AI use is a business priority, adoption accelerates. Position AI literacy as a strategic workforce capability, aligned directly with organizational objectives, risk frameworks and governance priorities. It should sit alongside AI governance and compliance efforts, not in a silo operating separately from them.

2. Tailor by role

Once the foundation is set, layer in role-based modules. Business leaders need strategic decision-making, oversight and risk awareness. Technical teams need implementation, validation and monitoring. Add scenario-based learning on top: realistic, sector-relevant case studies and high-impact use cases drawn from your own environment, in simulated settings where possible. The closer the training sits to the work, the better it sticks.

3. Embed governance

Responsible AI principles, fairness, transparency, accountability and privacy, shouldn’t be a standalone module. Weave them through the entire curriculum. Training should reinforce internal AI usage policies, data classification standards, escalation and oversight procedures and documentation expectations. Use real-world examples from your sector. Concrete evidence of real consequences — good and bad — is what makes governance stick.

4. Reinforce and measure

One-time training fails because AI capabilities, risks, and policies change continuously. Build periodic refreshers, knowledge checks, feedback loops and ongoing updates into the program, and embed reinforcement directly into daily workflows to lift retention. Then measure more than completion rates. Track behavioral change and impact. Adoption of approved AI tools, fewer policy violations, better documentation and productivity or quality gains can and should be tied to responsible AI use. Those metrics give you confidence that the program is actually working — and the evidence you need to sustain investment in it.

5. Use multiple ways to learn

Different formats reinforce different behaviors, and mature programs don’t rely on a single mode. They layer self-paced e-learning, live workshops, microlearning, hands-on labs and in-app guidance. Meeting people where they work, in the flow of the job, beats stacking one-off events.

6. Lead and champion

None of this scales without visible, sustained sponsorship from the top. When a CEO or COO signals that responsible AI use is a business priority, adoption accelerates, so position AI literacy as a strategic workforce capability aligned with organizational objectives, risk frameworks and governance priorities, not parked in a training silo. Treat it as a core, required competency for all staff, the way you treat cybersecurity awareness or data privacy training. Clear communication helps: emphasize AI as augmentation, the organization’s commitment to responsible use and how literacy supports mission, stewardship and risk management. Good change management reduces uncertainty. It also discourages shadow AI, people reaching for unapproved tools because no one showed them the approved path.

The takeaway is simple. Organizations that treat AI literacy as a strategic capability across the organization will be better positioned to close the gap between AI investment and AI output. Those that skip the discipline will see the gap between ambition and readiness widen. IDC’s Foundation AI Literacy study is a practical starting point. Read it to see how leading organizations are building the capability today.

Gina Smith, Ph.D

Gina Smith, Ph.D - Senior Research Director, IT Skills for Digital Business

As a Senior Research Director at IDC, Gina Smith produces research in the IT education and skills sector. Her responsibilities include primary research, analysis, and the production of market insights worldwide. The New York Times bestselling author of Apple cofounder Steve Wozniak’s…

Key Takeaways:

  • NXP introduced the Neural Axis architecture and is leveraging its acquisition of Kinara to expand its edge-AI NPU capabilities.
  • NVIDIA launched a platform for humanoid robotics, including world simulation and reference hardware.
  • Qualcomm introduced the Dragonwing IQ10, a fully integrated robotics SoC (system-on-chip) targeting production deployment by September 2026.
  • Intel formally launched Intel Robotics as a dedicated business unit with 130+ commercial design partnerships.

Computex Taipei 2026 demonstrated that robotics is no longer a side story at the world’s largest computing show. For the first time in its 45-year history, Computex dedicated an entire exhibition zone to Robotics and Physical AI. Major semiconductor vendors arrived not just with products but with a strategic position on who should own the market for the processors used in robotics.

Nvidia Leans on CUDA to Train and Run Physical AI

NVIDIA came to Computex with the boldest claim: that it intends to own the software layer that every robot in the world is developed on and runs on. Jensen Huang unveiled a complete platform spanning AI models for humanoid robots, a world simulation environment that lets developers train robots faster and at far lower cost, and a reference robot design that any manufacturer can build upon. Partners such as Stanford and ETH Zurich are already committed to the platform.

NVIDIA is releasing models and development tools openly to entice the robotics ecosystem onto its platform. It is taking the same playbook that built its dominance in datacenter AI and applying it to robotics. NVIDIA’s solutions are higher cost and have higher power consumption than its competitors.

NVIDIA’s benchmark claims are strong, but the real test is unstructured real-world performance over sustained operating periods, not controlled evaluations. The reference design approach smartly avoids NVIDIA competing with potential hardware partners. Watch whether robot manufacturers outside the Unitree partnership accept a platform built on a competitor’s silicon roadmap. That tension is where the ecosystem story either succeeds or stalls.

Qualcomm’s Dragonwing IQ10 Aims for Ease of Development

Qualcomm made a sharper, more immediate argument. Building a robot today means stitching together components from dozens of vendors, and every seam in that system is a source of cost, delay, and failure. Qualcomm’s answer is a single fully integrated platform, the Dragonwing IQ10, that collapses that complexity into one deployment-ready system. Cristiano Amon drove the point home by bringing a full-sized humanoid robot on stage and demonstrating it live. The commercial target is clear: the growing tier of robot makers and industrial operators who want to move from prototype to production without building their own technology stack. Early partners include NEURA Robotics, Advantech, and NEXCOM, with broader availability by September 2026.

Qualcomm’s position is built on a decade of designing chips for cars, where real-time reliability is non-negotiable. That heritage is a genuine differentiator in industrial Robotics. Pricing and actual partner shipments will be the proof points to watch.

Intel Robotics Goes the Open Source Path

Intel took the longest-term angle of the three. The company formally launched ‘Intel Robotics’ as a dedicated business and introduced an open-source framework designed to close the gap between robots that work in the lab and robots that work reliably on the factory floor. With more than 130 commercial design partnerships already in place, Intel has a broader installed base than its keynote visibility might suggest.

The clearest demonstration came from Sensory AI’s Ella, a robot barista operating in live retail environments, running multiple AI tasks simultaneously on a single Intel Panther Lake SoC. The one SoC has replaced what would have required multiple processors and a more complex system.

Intel’s open-platform strategy is a smart way to compete without going head-to-head with NVIDIA’s brand authority or Qualcomm’s automotive credibility. The risk is that open ecosystems take time to build, and Intel needs its developer community to grow faster than the incumbent platforms consolidate

Intel is also building on a long history of providing processors for edge infrastructure used for industrial automation and robotics, including the coordination of robots in a factory. Intel also has a history with its RealSense camera sensors, demonstrating drones that could fly through a forest, for example, dodging trees, and providing drone show coordination solutions. Intel is not new to robotics or to working with robotics companies, and it will be able to leverage decades of experience.

NXP’s Neural Axis Architecture Likened to a Nervous System for Robots

NXP used the closing keynote of Computex to make the most pointed argument of the show. CEO Rafael Sotomayor’s talk, ‘Bringing AI into the Real World,’ unveiled the Neural Axis architecture — a three-layer, biologically inspired framework spanning reasoning, coordination, and reflexive intelligence. His thesis: the defining challenge of physical AI is not how smart a machine is, but whether it can react in milliseconds without round-tripping to the cloud. Intelligence, he argued, cannot be centrally scaled; it has to be distributed so that no single point of failure can stop the machine.

NXP demonstrated the architecture across drones, software-defined vehicles, and humanoid robots, wrapped it in a trust framework built on containment, protection, verification, and adaptation, and tied it to its eIQ developer toolkit and its $307 million acquisition of edge-AI NPU maker Kinara. The framing casts NXP as the owner of the robotic nervous system—the reflexes and safety layer beneath whichever “brain” handles high-level reasoning.

NXP’s wide portfolio of processors, microcontroller units (MCUs), neural processing units (NPUs), connectivity technologies and analog components is highly complementary to the main processor.  NXP can own the deterministic, safety-critical layer where decisions happen in real time. Its decades of heritage in automotive and industrial silicon are hard to replicate. It can apply its experience in reliable solutions and functional safety to the robotics space. NXP is also partnering with Nvidia and supporting its software stack.

The Robotics Semiconductor Landscape Became More Competitive After Computex 2026

Computex’s new AI Robotics Zone drew Taiwan’s full supply chain of components, motors, and system builders. AI-related industries are forecast to account for around 70% of Taiwan’s exports over the next six months.

Beyond the headline platforms, Computex surfaced a sharper debate about what robotics requires to succeed at scale. NXP, as covered above, pressed the case that responsiveness — not raw intelligence — is the real constraint on physical AI. ABB, the industrial automation giant, showed that its NVIDIA partnership is enabling simulation accuracy close enough to real-world conditions that training times and deployment risks are falling significantly. ASUS entered the consumer market with service robots for healthcare and senior care, backed by an orchestration platform designed to work across brands and devices.

Robotics companies will have choices across processor vendors, processor architectures, closed versus open development platforms and software solutions, and various performance, power consumption, and cost specifications for CPUs and accelerators. The robotics market is not new, but the training and inference on new AI models – physical AI – is new, and the semiconductor vendors that can best support these new models with low power consumption and low cost will be best positioned to hit the sweet spot of unit volume and ASPs. There is also a lot of opportunity for adjacent companies such as NXP, IP vendors such as MIPS, and all the other semiconductors that provide other processors, connectivity, sensors, and power-related components.

Stay ahead of the physical AI semiconductor market. Access IDC’s latest forecasts, vendor analysis, and industry data at IDC Semiconductor Research. Speak with our analysts, contact us today!

Phil Solis - Research Director, Semiconductors and Enabling Technologies - IDC

Phil Solis is Research Director within IDC’s enterprise infrastructure global research domain. He focuses on client computing and connectivity as part of the Semiconductors and Enabling Technologies subdomain. Phil’s coverage spans semiconductors in PCs, media tablets, smartphones, and wireless and mobile connectivity technologies.

Navkendar Singh - Associate Vice President - IDC

Navkendar Singh is a Associate Vice President with IDC India, based in Gurgaon. His research domains encompass deep-dive research and insights in and around mobile devices, smart homes, PCs, tablets, wearables, and the printing market in India, Bangladesh, and Sri Lanka. He is also involved in building IDC's successful channel research programs for these domains at city and state levels. Navkendar also leads research related to analyzing the role of devices, emerging business engagement models, the impact of emerging technologies on devices, and emerging personas related to Future of Work.

President Trump’s Executive Order on quantum innovation establishes the most comprehensive U.S. federal commitment to quantum technology leadership since the National Quantum Initiative Act of 2018, directing coordinated investment across national laboratories, industry, academia, and the intelligence community to develop the first quantum computer capable of enabling a new era of scientific discovery. By mandating an updated national strategy, workforce development, domestic supply chain resilience, and quantum-enabled sensor and network deployment within five years, the Order creates a structured federal demand signal that will accelerate commercialization timelines, attract private capital, and intensify competitive pressure on U.S. technology companies to deliver quantum-ready solutions. IDC views this Executive Order as a market-shaping policy event that will define quantum investment priorities, procurement patterns, and go-to-market strategies for technology vendors across computing, cryptography, sensing, and national security for the decade ahead.

What the order does and why it matters

President Trump’s Executive Order on quantum innovation represents a decisive escalation of the federal government’s commitment to securing and extending U.S. leadership in quantum technologies at a moment when competing nations — including adversarial states — are accelerating their own quantum programs. The Order updates the National Quantum Strategy to prioritize quantum-enabling technologies and industry partnerships, establishes a national effort to build the first quantum computer powerful enough to initiate an era of quantum-enabled scientific discovery, and directs coordinated action across the Departments of Energy and Commerce and the intelligence community. In the quantum computing market, this policy action serves as both a demand catalyst and a strategic roadmap, signaling sustained federal investment, procurement intent, and the organizational infrastructure needed to translate laboratory-stage quantum capabilities into commercial and national security applications at scale.

The Order’s workforce and supply chain directives are among its most commercially significant provisions for technology market participants. By prioritizing the expansion of registered apprenticeships, credentials, and the creation of National Quantum Workforce Development Institutes, the Executive Order directly addresses the talent gap that has constrained quantum program scaling across both government and private sector organizations. The simultaneous directive to develop domestic supply chain and manufacturing capabilities for quantum technologies signals federal intent to reduce dependence on foreign components and subsystems — a move that will create procurement advantages for U.S.-based quantum hardware and materials suppliers while pressuring global supply chains to realign around domestic sourcing requirements. For technology vendors, these provisions create a structured pathway to federal partnership that rewards early investment in workforce alignment and domestic manufacturing capacity.

The Order’s directive to deploy quantum-enabled sensors and networks within five years, combined with the reconstitution of the National Quantum Initiative Advisory Committee and the expansion of the Quantum Counterintelligence Protection Team, signals that the federal government is treating quantum not merely as a future computing paradigm but as an active national security and infrastructure priority that requires immediate operational planning. This framing has direct implications for the cybersecurity market, where the prospect of quantum computers with cryptographic relevance has already driven post-quantum cryptography standardization efforts, and where the expanded Quantum Counterintelligence Protection Team signals heightened federal attention to quantum-enabled espionage and supply chain integrity risks. Building on the Trump Administration’s $625 million investment in national quantum research institutes and the November 2025 Genesis Mission executive order on AI-accelerated scientific discovery, this latest Order positions quantum as a foundational layer of U.S. technological and economic dominance for the decade ahead.

Key benefits for the technology marketplace, citizens, and technology customers

  • Federal demand signal accelerating quantum commercialization timelines. The Executive Order establishes structured federal procurement intent and investment priorities that provide quantum technology vendors with a clear roadmap for aligning product development with government requirements and accelerating the transition from research-stage to commercially deployable quantum systems.
  • National workforce development infrastructure reduces the quantum talent gap. The creation of National Quantum Workforce Development Institutes and the expansion of registered apprenticeships and credentials will begin to address the critical shortage of quantum-skilled engineers, scientists, and technicians, which has been the primary constraint on quantum program scaling across both public and private sectors.
  • Domestic supply chain investment creating competitive advantage for U.S. vendors. Federal directives to develop domestic quantum manufacturing and supply chain capabilities will create procurement preferences and partnership opportunities for U.S.-based quantum hardware, materials, and component suppliers — reducing foreign dependency while building industrial capacity.
  • Quantum-enabled sensor and network deployment opening new commercial markets. The five-year directive to deploy quantum sensors and networks across government applications will create early reference deployments that validate commercial use cases in precision navigation, environmental monitoring, medical imaging, and secure communications — accelerating civilian market development.
  • Post-quantum cryptography urgency driving enterprise security investment. The Order’s national security framing and expansion of the Quantum Counterintelligence Protection Team will intensify enterprise awareness of quantum-enabled cryptographic risks, accelerate the adoption of post-quantum cryptography standards, and create near-term commercial opportunities for cybersecurity vendors.
  • AI and quantum convergence are unlocking transformational scientific and industrial applications. By building on the Genesis Mission’s AI-accelerated scientific discovery framework, the Order positions quantum-AI convergence as a strategic national priority, creating commercial opportunities in drug discovery, materials science, energy optimization, and advanced manufacturing for vendors operating at this intersection.
  • International partner engagement strengthening global quantum market access. The Order’s directive for appropriate engagement with international allies on quantum matters establishes a framework for allied-nation quantum collaboration, opening export opportunities for U.S. quantum technology vendors in trusted partner markets.
  • $625 million federal research investment seeding long-term commercial ecosystem development. The Trump Administration’s existing investment in national quantum research institutes, combined with new funding directives in this Order, provides an academic and laboratory pipeline that will produce the talent, intellectual property, and start-up formation activity that sustains long-term commercial quantum ecosystem growth.

What this means for the market

IDC views President Trump’s quantum Executive Order as the most consequential U.S. quantum policy action since the National Quantum Initiative Act, and one that will materially reshape investment patterns, procurement priorities, and competitive dynamics across the quantum computing market. The Order’s establishment of a national effort to build a scientifically capable quantum computer provides the clearest federal articulation to date of what the government expects quantum computing to achieve — and by implication, what capabilities vendors must demonstrate to compete for federal contracts and partnerships. This specificity of ambition, combined with coordinated cross-agency execution authority, is precisely the governance structure the quantum market has needed to move from research investment to programmatic deployment at scale.

The workforce and domestic supply chain directives are the provisions IDC considers most structurally important for the long-term health of the U.S. quantum industry. Quantum program scaling has been constrained less by fundamental physics than by the availability of engineers, technicians, and program managers who can operate and integrate quantum systems in real-world environments. The National Quantum Workforce Development Institutes and the expansion of apprenticeships directly address this constraint. Simultaneously, domestic supply chain investment addresses a vulnerability that has become increasingly visible as geopolitical tensions have exposed the fragility of global semiconductor and advanced materials supply chains — a risk that applies with equal or greater force to the specialized components required by quantum hardware.

The quantum-AI convergence embedded in this Order — building explicitly on the Genesis Mission’s AI-accelerated scientific discovery framework — signals that the federal government views quantum and AI not as parallel programs but as mutually reinforcing capabilities that will together define the next wave of U.S. technological advantage. For technology vendors, this framing has immediate strategic implications: organizations that can demonstrate integrated quantum-AI solutions will be positioned advantageously for federal partnership, research funding, and procurement consideration. IDC expects this policy environment to accelerate M&A activity, joint venture formation, and strategic partnership announcements among quantum hardware, quantum software, and AI platform vendors as they move to align their portfolios with the federal strategic direction.

The primary challenge for U.S. technology companies responding to this Executive Order is the gap between federal ambition and the current state of quantum hardware maturity. The Order’s directive to build the first scientifically capable quantum computer and deploy quantum sensors and networks within five years sets extremely demanding timelines, given the engineering challenges that remain in error correction, qubit coherence, and system integration. Technology vendors risk over-committing to federal program requirements that outpace achievable hardware milestones, creating execution risk that could damage both commercial credibility and federal partnership relationships if quantum capability targets are missed at the program level.

Philip D. Harris, CISSP, CCSK

Philip D. Harris, CISSP, CCSK - Research Director, Governance, Risk, and Compliance (GRC) Solutions

Phil Harris is Research Director for GRC Solutions at IDC, where he develops and promotes IDC's point of view on risk, advisory, privacy, and compliance services and software. He conducts research on business strategies and the impact of relevant offerings…

IDC recently brought together 20 senior technology executives for an invitation-only dinner with analysts Carla Arend, Andrew Buss, Duncan Brown, and Rahiel Nasir to discuss digital sovereignty in Europe. Here’s what came out of the room.

Sovereignty is real. The conversation around it isn’t.

IDC opened with a provocation: the word “sovereignty” is doing more harm than good. It’s politically loaded, definitionally contested, and vendors have been guilty of “sovereign washing”. Meanwhile, IT departments struggle to translate the concept into something their internal stakeholders actually care about.

What European organisations do care about is entirely concrete: protection against extra-territorial data requests, regulatory compliance, and supply chain resilience. According to IDC research, these are operational risk priorities, not political statements. The vendors making progress in this space have figured out how to speak to that gap. Those still foisting their own definitions of sovereignty on to the market and/or offering nothing more than so-called solutions for data localisation/residency largely haven’t.

The cloud strategy picture is more nuanced than the headlines suggest

Europe is re-assessing its options for cloud and technology providers. Global hyperscalers remain part of the picture, but how they are used is increasingly open to question. IDC’s data points to a clear shift toward layered architectures that combine global scale with local control. A specific model is emerging as the dominant pattern, and the vendors positioned within it are seeing very different conversations than those sitting outside it.

The regulatory picture adds another layer of complexity. NIS2, DORA, the AI Act: each creates compliance obligations that directly shape how organisations think about their technology infrastructure and provider relationships. Navigating that landscape without a clear positioning is increasingly difficult.

Private cloud is not the safe harbour it looks like at first glance

IDC commonly emphasizes that private cloud is the ultimate sovereign cloud, and this remains strongly the case as very few companies wish to exit all their datacenters and move wholesale to the public cloud. As adoption of private cloud has grown and evolved, it has moved from bespoke private cloud implementations towards being built on end-to-end private cloud stacks from major providers, with popular options being Microsoft Azure Local, Google Distributed Cloud, AWS Outposts, or VMware Cloud Foundation. This has resulted in unprecedented capability for enterprises running their own applications and services – but with this has also come a co-dependency on external providers for the ongoing operations of the control plane of the private cloud.

Should any serious technology or political issues arise that interrupts the connection between the public cloud based control plane and the private cloud, services deployed and delivered on the private cloud infrastructure may remain static, degrade over time, or even stop working. The end result is a bought and paid for sovereign physical infrastructure that is unable to operate effectively due to a non-sovereign operations management dependency – and this is a major risk today that a few years ago seemed unthinkable.

European customers have been providing forceful feedback to private cloud stack providers that this public cloud control plane dependency is untenable, and the market is beginning to respond. Most, but not all, providers of private cloud stacks have begun to offer an on-premises approach to the control plane, allowing fully disconnected management of applications or digital services deployment and operations, as well as of licencing tracking and billing, or updates and patching from offline sources.  The big challenge though is that these disconnected options are often limited when it comes to go to market, with vendors limiting access to the largest companies or critical national infrastructure providers or the defense industrial complex. While this may be acceptable initially as solutions come to market and are proven, for the longer-term vendors will need to make disconnected operations a core part of their value proposition across the whole customer base.

AI sovereignty: the new frontier

AI sovereignty has been part of the digital sovereignty debate for some time. But it has now emerged as the new frontier: the question of who controls the models, the data used to train them, and the inference infrastructure is becoming as contested as data residency was five years ago. The general read in the room: AI sovereignty is harder to achieve than data or infrastructure sovereignty, and the messaging across the industry remains inconsistent.

Dig deeper into the research

The dinner was one part of a broader IDC programme on digital sovereignty across Europe. If the themes above are relevant to your positioning or go-to-market strategy, here is where to go next.

Digital Sovereignty Beyond the Label – IDC’s Strategic Guide cuts through the definitional noise and explains what buyers actually evaluate when assessing sovereign solutions and providers. Download free.

From Sovereignty Claims to Credible Positioning – A customer case study on how technology providers are turning sovereignty into a commercially viable proposition. No form required.

Missed the webinar? Rahiel Nasir and Duncan Brown covered buyer expectations, sovereign washing, and practical go-to-market guidance on June 18. The on-demand recording is available here.

IDC’s Digital Sovereignty research covers cloud strategy, data governance, regulatory compliance, and infrastructure sovereignty across European markets. Research presented at the dinner was drawn from IDC’s European Digital Sovereignty Survey and the Semiannual Public Cloud Services Tracker.

Rahiel Nasir

Rahiel Nasir - Research Director, Cloud and Datacenters, Enterprise Infrastructure

Rahiel Nasir is Research Director within IDC’s enterprise infrastructure global research domain and part of the Cloud and Datacenters subdomain. Rahiel is IDC’s global lead on digital, cloud, and AI sovereignty. In this capacity, he covers emerging sovereignty initiatives and…
Duncan Brown

Duncan Brown - Group Vice President, Global Domain Lead: Worldwide Security & Trust

Duncan Brown leads IDC’s worldwide Security and Trust research, encompassing cybersecurity hardware and software products as well as professional and managed services. His analysis and opinions on security, cyber-resiliency, sovereignty and AI governance are widely sought by industry leaders and…