A New Era of AI-Driven Healthcare in Asia Pacific
Asia/Pacific’s healthcare sector is entering a revolutionary era – driven by a surge in clinical data powered by AI and GenAI, and more recently, Agentic AI. This era will be shaped by the need to balance dual priorities of efficiency and effectiveness across workflows and workforce productivity.
To meet these demands, healthcare provider organizations are now focusing their investments on four immediate priorities.
- Workflow automation to increase workflow efficiency for enhanced care outcomes
- Patient-centric care delivery models to ensure care accessibility and convenience
- GenAI solutions to augment clinician efficiency while creating a hyper-personalized patient experience (PX)
- Cybersecurity to maintain cyber-resilience as emerging technologies become the imperative for modernized healthcare
AI-Driven Workflow Automation: Scaling Efficiency and Outcomes
As healthcare providers across the Asia-Pacific region pursue greater operational efficiency, improved quality of care, and scalability, AI and automation are becoming a top priority. Repetitive and data-intensive processes are placing a heavy burden on healthcare providers, draining valuable time and resources. By automating these tasks, organizations can relieve this strain, optimize internal resources, and significantly reduce administrative overload.
At the same time, there is growing pressure from rapidly aging populations—particularly in super-aged nations like Japan and South Korea. This, along with the rising prevalence of non-communicable diseases (NCDs), is increasing demand for more efficient healthcare delivery.
To address these shifts, healthcare providers have identified healthcare-specific use cases for automation in the next two years: clinical workflows, operational workflows, and administrative workflows.
Electronic Health Record (EHR) platform, with its tools and functionalities, serves as a robust foundation for automation investments. One-third of healthcare providers have already invested in CDSS (Clinical Decision Support Systems), while more than half plan to invest within the next two years.
IDC data shows that almost half (47%) of healthcare organizations consider health data platforms as the topmost investment potential, owing to the need for large-scale data integration, data leveraging, and real-time analytics for “Intelligent Automation.”*
New Patient-Centric Care Models: From Telemedicine to Hospital-at-Home
Innovations in patient-centric care delivery solutions continue to accelerate. This is also driven by the rising consumerization of care and supported by a maturing health tech ecosystem.
For example, telemedicine is transforming into comprehensive Telehealth platforms. What began as basic virtual consultations has now expanded to include integrated access to electronic medical records, e-prescriptions, lab results, and patient education—all within a single interface. This empowers patients to make informed decisions and take greater ownership of their health.
In another case, Remote Patient Monitoring (RPM) is progressing into full-fledged “Hospital-at-Home” (H@H) models. Over half of regional care providers are investing in H@H technologies. For example, Singapore General Hospital (SGH) and Khoo Teck Puat Hospital (KTPH), under the National University Health System (NUHS), have launched the Mobile Inpatient Care@Home (MIC@Home) program. Spearheaded by the MoH Office for Healthcare Transformation (MOHT), the program supports patients with general medical conditions such as skin infections, urinary tract infections, and congestive heart failure. Following a successful pilot, the initiative has expanded to four more hospitals: Changi General Hospital (CGH), KK Women’s and Children’s Hospital (KKH), Sengkang General Hospital (SKH), and Tan Tock Seng Hospital (TTSH). Similarly, in Australia, 44 hospitals in Victoria are now offering Hospital-in-the-Home (HITH) services. To scale these models effectively, healthcare providers are increasingly reshaping their investments through Digital Front Door (DFD) strategies. By leveraging the broader healthtech ecosystem and adopting innovative, patient-focused delivery models, they aim to create more efficient, scalable, and responsive healthcare systems across the region.
IDC predicts that by 2027, driven by the demand for enhanced care collaboration, expanded clinician and consumer access, and enhanced digital literacy, 80% of patients in APeJ (Asia/Pacific except Japan) will utilize Hybrid Care.*
Augmenting Clinician Efficiency and Hyper-Personalized Patient Experience with GenAI and Agentic AI
GenAI and Agentic AI.are poised to make healthcare more accessible to underserved populations. Recognizing its potential, over half of the region’s healthcare providers plan to invest in GenAI solutions within the next two years.
Healthcare organizations are set to transition from early experimentation to developing comprehensive, enterprise-wide AI strategies. CIOs from both multi-specialty and super-specialty hospitals are already exploring targeted GenAI use cases, not only to optimize resource alignment but also to identify the prerequisites necessary to become truly GenAI-ready.
IDC predicts that, by 2026 healthcare GenAI investments are expected to double in Asia/Pacific excluding Japan (APeJ), driven by the rapid deployment of use cases, more curated clinical data, and increased organizational buy-in.
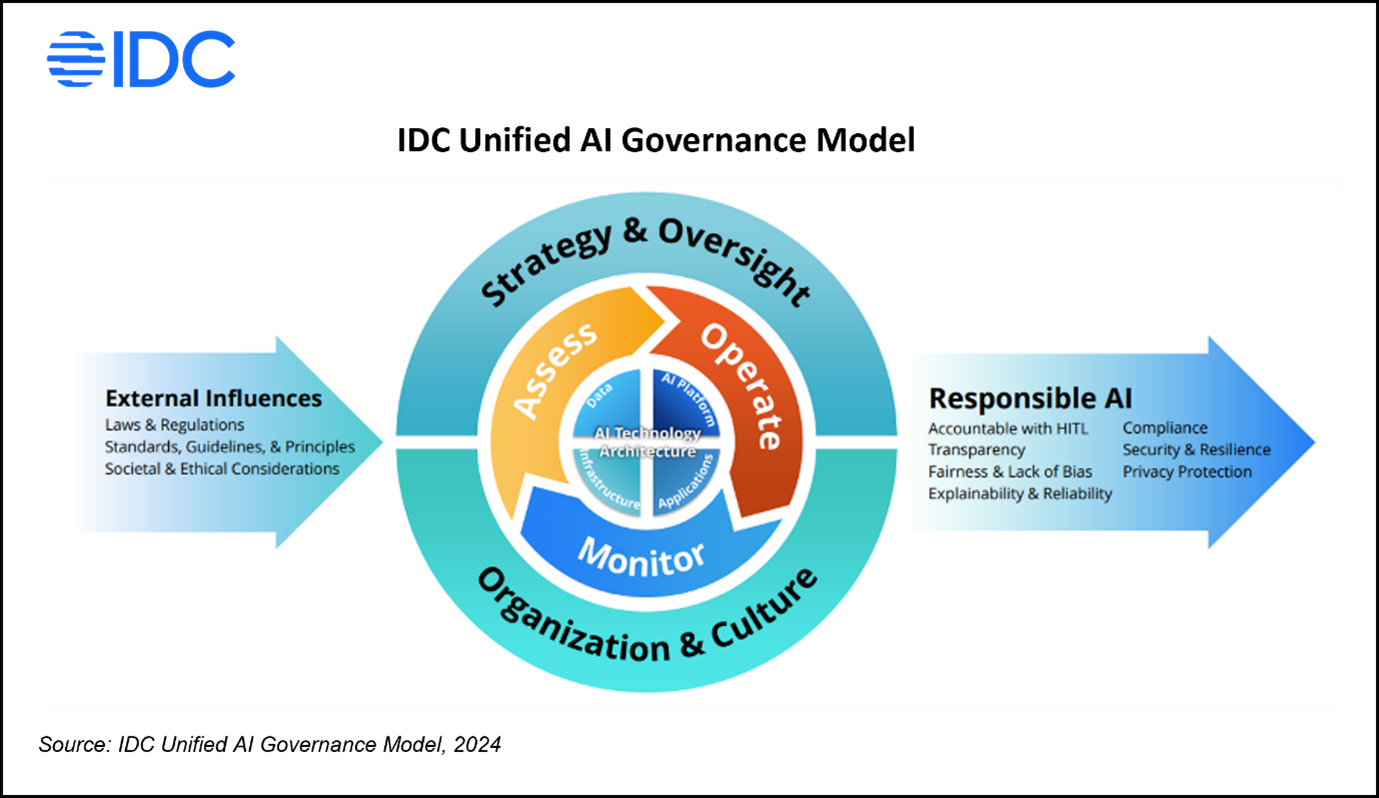
In the context of GenAI, hospital chains across the region have begun integrating data across their networks to effectively deploy large language models (LLMs). For example, Apollo Hospitals in India has developed a Clinical Intelligence Engine (CIE) powered by LLMs, which leverages extensive clinical datasets from its hospital network to deliver faster, more informed patient responses. In Singapore, Synapxe, the national healthtech agency, has implemented a GenAI tool called “Russel GPT”, designed to generate rapid summaries from patient data to boost clinician efficiency and enhance the overall patient experience. As Agentic AI adoption among care providers emerges, the primary focus is on enhancing productivity far beyond that provided by GenAI. This focus will demand for almost a third of the GenAI investments in Agentic AI in 2026. Encouraged by the potential of these use cases, healthcare providers across the region are specifically seeking partners with strong AI security capabilities, cloud ecosystems integrated with AI services, a commitment to responsible AI practices, and robust data governance frameworks to ensure safe and effective deployment of GenAI solutions.
AI-Powered Cybersecurity: Core to Healthcare Resilience and Patient Data Safety
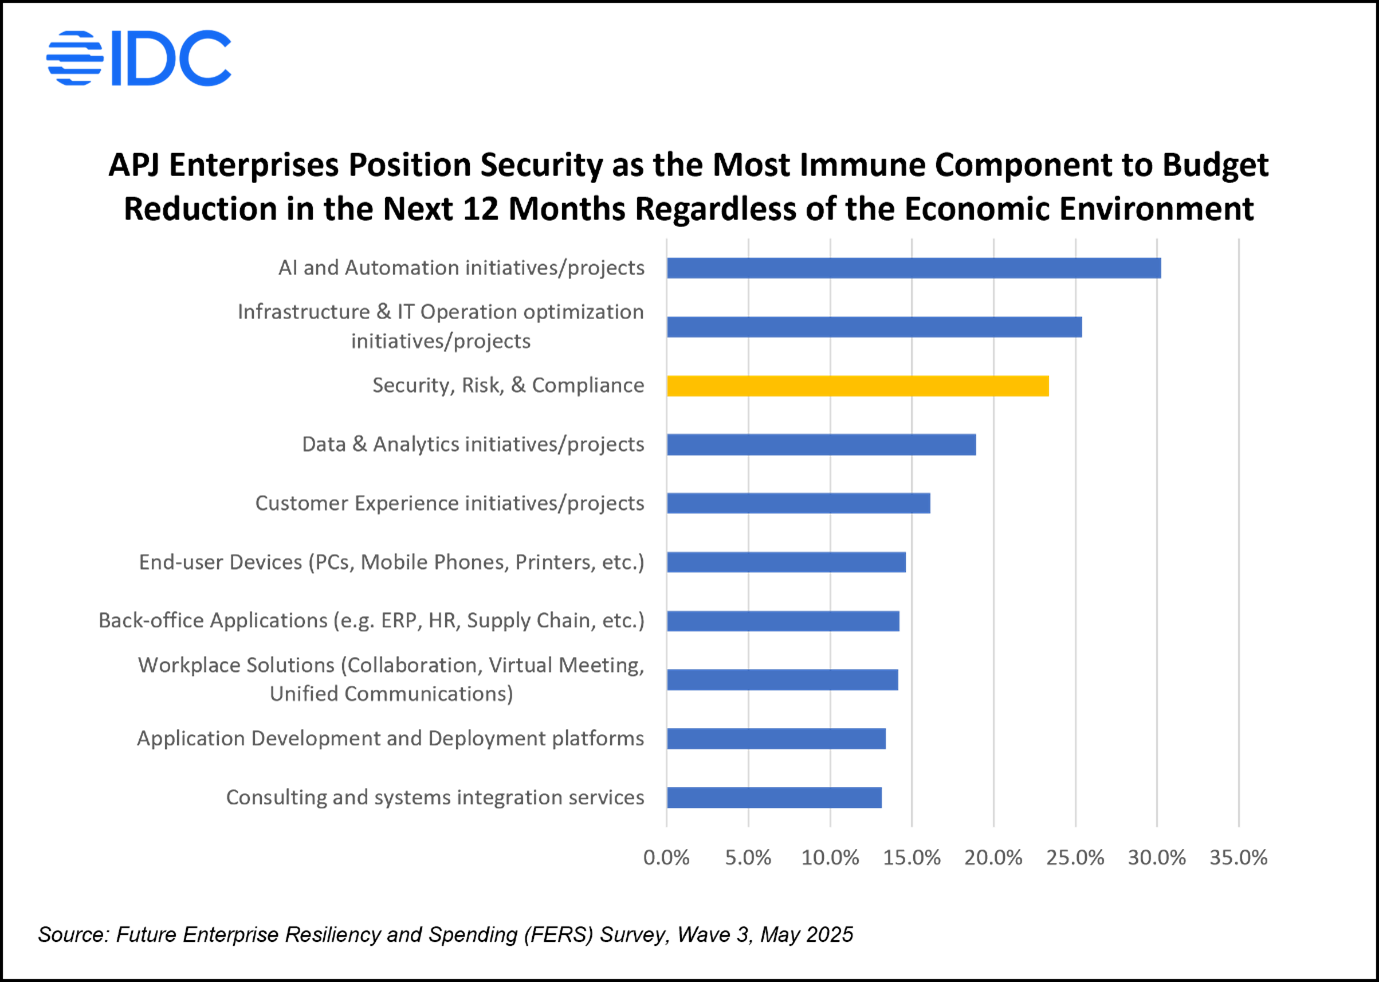
The healthcare sector in the Asia-Pacific region remains highly vulnerable, as the frequency and severity of cyberattacks on major hospitals continue to increase. In India, a recent ransomware attack on AIIMS (All India Institute of Medical Sciences) forced operations into manual mode, disrupting critical services. Similarly, in Australia, a cyberattack led to a significant data breach at St. Vincent’s Health. Considering such incidents, healthcare CIOs across the region are not only prioritizing investments in cybersecurity but are also focusing on cyber-resilience. This translates into proactively detecting and responding to threats earlier through AI-driven security solutions that enhance threat intelligence, response, and recovery.
IDC reports that by 2026, growing cybersecurity risks will prompt 40% of healthcare organizations in APeJ to adopt AI-based threat intelligence solutions to ensure care continuity and safeguard patients.*
A targeted attack on an AI system could compromise its output, potentially endangering patients, such as altered radiation dosages in cancer treatment plans. These threats underscore the critical need for robust security measures to safeguard the integrity and accuracy of AI-driven healthcare applications.
To address these risks, hospitals in the region are heavily exploring AI-specific cybersecurity strategies, including advanced encryption methods to secure data transmission, real-time threat detection systems to identify anomalies, and stringent access controls to prevent unauthorized use.
The current landscape of the Asia/Pacific healthcare sector limits organizations’ ability to enhance their IT security capabilities. IDC data indicate that regional healthcare providers prioritize managing internal and external security risks, achieving greater visibility into the threat landscape, and having proactive threat detection, response, and remediation capabilities. Security service providers need to align their capabilities with these priority areas for initial pitching and successful engagement. CISOs and CIOs of regional healthcare providers have indicated to IDC that real-time threat intelligence and predictive analytics for identifying potential security risks are the most valuable functionalities they seek in AI-powered security tools, reflecting a strong focus on proactive and efficient threat detection and response.
Defining the path ahead to secure the future
To truly unlock the potential of GenAI and Agentic AI, healthcare providers must take a thoughtful and strategic path forward. It starts with building a strong foundation by establishing a data governance framework led by a team of clinicians, data scientists, legal experts, and patient safety officers to guide responsible use. One of the most impactful steps is integrating GenAI into EHR workflows, especially for automating documentation, something IDC identifies as a top priority for care providers. Just as important is strengthening the data architecture behind these systems, ensuring they are secure, scalable, and ready to support the future of AI-powered healthcare.
Take the next step and realize the full business value of AI with our two practical webinars:
If you would like to speak to an IDC analyst about our tech-related insights on healthcare, simply fill out the form.
*SOURCE: IDC FutureScape: Worldwide Healthcare Industry 2025 Predictions — Asia Pacific (Excluding Japan) Implications