Enterprise applications are the foundation of modern business operations. In 2023, the market expanded by 12%, reflecting its continued importance. 

We can attribute this market growth to the following drivers: 

  • AI and Generative AI: The integration of AI and generative AI (GenAI) is transforming enterprise applications. From predictive analytics in CRM systems to personalized recommendations in ecommerce platforms, these technologies are making applications more intelligent and insightful. 
  • Cloud Dominance: Cloud technology is the present and the future of enterprise applications. Its ability to support technologies such as AI, machine learning, and the Internet of Things ensures that businesses can continue to evolve and adapt to internal and external needs and requirements. 
  • Ongoing Investments in Digital Transformation: Continuous digital transformation efforts are driving the adoption of enterprise applications, with organizations modernizing outdated systems and implementing innovative solutions across all business functions.

The Imperative of Enterprise Application Modernization 

With more legacy systems reaching the end of their lifecycle — if only from a support perspective — and older platforms faltering under demand for increased agility, flexibility, and resilience, the modernization of enterprise applications has swiftly ascended organizations’ priority lists. In EMEA, application modernization has become a central focus, with an impressive 96% of surveyed organizations planning to undertake this essential transformation.

Challenges in Modernization

Each organization possesses a distinct approach to application modernization; no singular path forward exists. The complexities involved in modernizing applications across an enterprise demand a variety of tailored strategies — and this will likely remain the case.

Specific routes to modernization differ significantly by market, sector, and organization, with varied strategies emerging to address the diverse needs of different departments and their respective applications.

The Role of Cloud

While these strategies may differ, cloud technology stands out as the unifying force, having rapidly established itself as the preferred framework for both new and existing enterprise applications. Organizations are exploring multiple routes to modernization, with nearly half of those surveyed in EMEA expressing a desire to lift and shift their existing applications to the cloud.

Moreover, 43% aim to migrate to new cloud-based versions of their current applications, while 42% are eager to embrace entirely new cloud solutions.

Cloud: The Catalyst for Enterprise Transformation

Cloud technology is increasingly the foundation of organizations’ efforts to modernize their business applications. It empowers enterprises to swiftly adapt to shifting business needs, deploy updates seamlessly, and leverage cutting-edge technologies such as AI/GenAI, advanced analytics, and next-gen security.

Growth of Cloud-Based Applications

Cloud computing has massively fueled the growth of enterprise applications throughout EMEA. According to IDC’s May 2024 release of its software and public cloud services forecast, the enterprise apps market will continue to expand hugely — from $27.2 billion in 2019 to an estimated $63.7 billion in 2028 — reflecting a significant shift from on-premises to cloud-based applications.

The proportion of enterprise applications in public cloud surged from 36% in 2019 to an astonishing 68% in 2023, reflecting a marked acceleration in the growth of public cloud usage throughout the region. By migrating to cloud, companies can enhance performance, bolster security, and ensure superior disaster recovery. Cloud’s role as a crucial component of modern IT strategies has solidified.

Factors Driving Cloud Adoption

Additionally, the rise of remote work — especially during the pandemic — alongside regulatory compliance needs and the integration of emerging technologies, has further catalyzed cloud adoption. With the ongoing establishment of local cloud datacenters and numerous partnerships formed by enterprise application providers, we predict that cloud-based enterprise applications will continue to expand, reaching nearly 77% of all enterprise applications in 2028. 

Regional Insights: EMEA Market Dynamics

From a subregional perspective, Western Europe commands a dominant position in the region, holding EMEA market share of 88%. This dominance can be attributed to the strong presence of companies like Visma and DATEV, which primarily focus on financial applications, payroll management, and HCM within Western European markets. Global giants such as SAP, Oracle, and Sage also maintain significant footholds in this subregion. 

In contrast, each of the Central & Eastern Europe (CEE) and the Middle East & Africa (MEA) subregions accounts for EMEA enterprise applications market share of 6%.
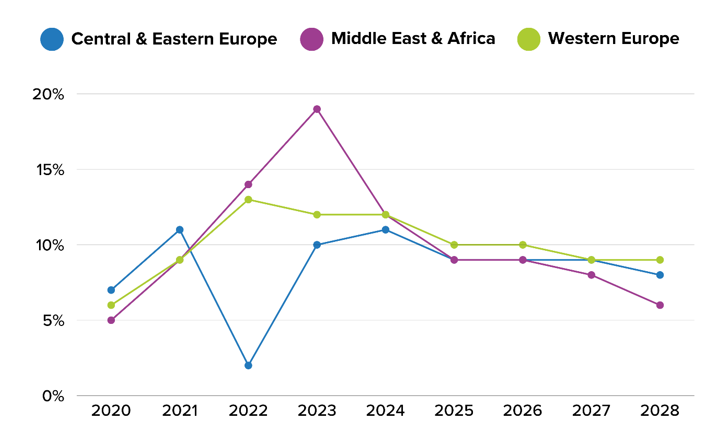
However, CEE has recorded a decline in spending due to several challenging macroeconomic factors.

The protracted Russia-Ukraine War, which began in February 2022, has introduced notable economic instability in the subregion. High inflation rates have diminished the spending power of businesses, while stringent monetary policies have adversely impacted software investments, resulting in a significant decline in 2022 and sluggish recovery in 2023.

On the flip side, MEA has experienced substantial growth over the past four or five years, largely driven by the emergence of cloud and cloud-based services in 2018 and 2019. This growth has been bolstered by considerable investments from cloud providers.

Organizations and large family-owned enterprises in MEA, previously reliant on monolithic legacy applications, have begun adopting SaaS solutions for non-critical workloads such as HCM, procurement, and asset management. They have thus far been successful in their overall application modernization efforts, with a growing number of businesses re-architecting, re-platforming, and re-engineering their in-house legacy systems.

Navigating the Complexity of Cloud Migration

As organizations consider their enterprise application investments and modernization opportunities and the advantages of cloud migration, they are exploring the most effective implementation paths for their new cloud-based applications. In the past, heavily customized implementations were the preferred route, as organizations sought to tailor their applications to better suit their operations.

However, a noticeable shift is occurring as organizations increasingly embrace a more standardized implementation approach.

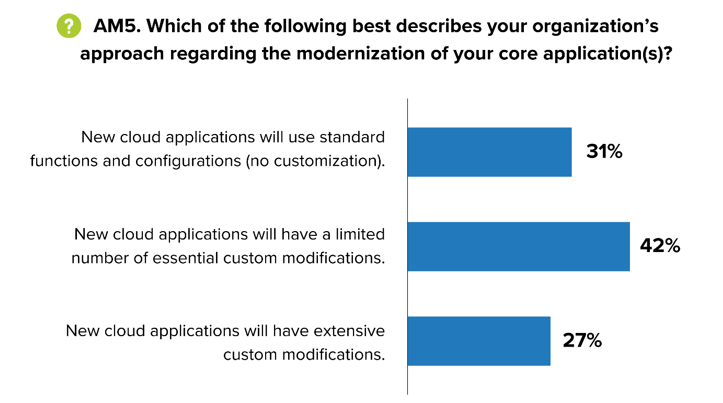
Approximately 31% of respondents plan to rely solely on standard functions and configurations for their new cloud-based applications, while 42% are contemplating only essential modifications — typically, those focused on sector-specific functionality — to maintain otherwise predominantly standardized implementations.
The Benefits of Standardization

The preference for standardized approaches is motivated by clear and tangible benefits. For instance, as new security patches are released, organizations with more standardized implementations can rapidly update their systems without necessitating further testing. This capability ensures the most robust protections are in place as quickly as possible, without requiring additional investments in IT, security, or implementation capabilities. 

Accessing New Features Quickly

Access to new features is another crucial factor. As the pace of change accelerates, organizations are eager to leverage new functionalities — such as GenAI and sustainability tools — immediately upon their release.

Typically, these enhancements are first introduced in cloud-based SaaS versions, with vendors maintaining slower update cadences for on-premises editions. Consequently, a more standardized implementation offers the quickest and most straightforward access to these emerging features and functionalities.

This inclination for less customized implementations ensures that organizations stay current with vendor innovations — ultimately, helping them maximize the benefits of their enterprise application modernization investments. 

Conclusion

Enterprise application modernization is essential for businesses competing in the digital age. Cloud technology is key to this process, enabling agility and innovation. While modernization approaches vary, a trend is clear toward standardized solutions that maximize the benefits of cloud and AI, including GenAI.

To be successful, increase efficiency and competitiveness, and future-proof operations, organizations must take a comprehensive approach to modernization, considering not only specific business needs and appropriate technologies, but also data governance and sustainability.

This blog serves as a summary of the valuable insights shared during our recent webinar on enterprise application modernization. If you found this discussion on the transformative power of cloud technology and AI interesting, we invite you to access the full webinar on demand.
Ashok Patel - Research Manager, European Enterprise Applications - IDC

Ashok Patel is a research manager in IDC’s European enterprise applications team. Prior to joining IDC, he led the Market Trends programme at Source Global Research, providing insights into the latest trends and developments across the professional services market, and has previous experience exploring clients’ perceptions of consulting firms. Prior to working in professional services, Ashok was an editor and consultant in the commodities market, as well as working in the automotive industry.

In three years, I anticipate that around 40% of global engineering-oriented manufacturing companies will leverage digital twins within the industrial metaverse to enhance collaboration and accelerate time to value.

What leads me to this prediction? Let’s start with IDC’s definition of the industrial metaverse as a highly immersive environment that seamlessly integrates the physical and digital worlds, fostering shared presence, interaction, and continuity across engineering, operations, supply chains, and business functions.

In engineering domain, the industrial metaverse functions as a cloud-native, multi-domain platform for 3D visualization and collaboration, bringing products to life through integrated, physically accurate simulations. It acts as a “digital twin of digital twins,” utilizing real-time data from multiple domains such as mechanical, electrical, and software interactions.

Building this environment requires collaboration among key players, including hyperscalers and providers of simulation platforms, 3D visualization, and digital business tools. New partnerships are constantly emerging, involving major companies in digital infrastructure, cloud computing, engineering platforms, visualization technologies, and artificial intelligence — all working together to push the industrial metaverse beyond the traditional digital twin model.

What Do the Numbers Tell?

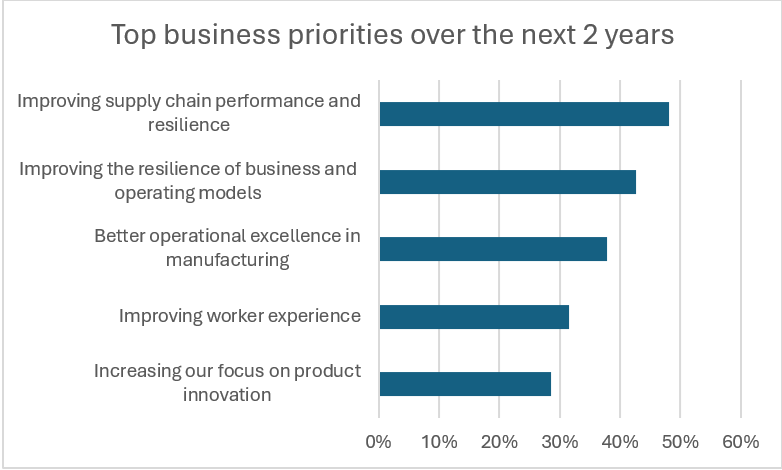
Product innovation remains a key business priority for engineering-focused manufacturing organizations, as highlighted in IDC’s 2024 Global Manufacturing Industry Core Survey (Figure 1).

Figure 1: Question: What are your company’s top business priorities over the next 2 years?

According to IDC’s 2023 Global Product and Service Innovation Survey, 25% of manufacturing respondents considered industrial metaverse technology to be “very important” for product and service innovation. This number was even higher among engineering respondents, with 34% rating it as very important.

Furthermore, 38% of respondents from companies with over 1,000 employees in IDC’s 2024 Global Manufacturing Industry Core Survey stated that Industrial Metaverse technology plays a “moderate to very high” role in supporting their company’s achievement of key operational KPIs.

 As a result, the adoption of the industrial metaverse in engineering-focused manufacturing organizations is anticipated to grow steadily over the next three years.

In Conclusion

My advice for early adopters is to keep a close eye on hyperscalers, leading technology vendors, and the startup ecosystem — to stay up-to-date with the rapidly evolving landscape of industrial metaverse development. Additionally, remember that integrating real-world data with IT data to create advanced simulation and collaboration tools requires time and careful planning.

Building and nurturing digital communities and ecosystems is essential, as they will be key to future success in the industrial metaverse. Lastly, recognize that the value of the industrial metaverse extends beyond product design and engineering, reaching areas like operations, maintenance, quality, procurement, and the supply chain, among others.

As the January 2025 deadline for the EU Digital Operational Resilience Act (DORA) approaches, financial institutions and ICT providers across the European Economic Area (EEA) must urgently assess their readiness, address regulatory gaps, and implement the necessary tools and processes to ensure compliance and safeguard digital resilience.

On January 17, 2025, the EU Digital Operational Resilience Act will take effect across all European Economic Area countries. It will impact financial institutions and their ICT service providers even beyond these borders in certain circumstances.

With only three months remaining, more than 20,000 financial entities must comply with DORA’s regulatory requirements. However, in IDC’s European Security Technologies and Strategies Survey 2024 (May 2024), 49% of respondents stated, “We are aware of DORA but have not yet undertaken exploratory work,” and 14% admitted, “We are not aware of DORA.”

Since then, progress has hopefully been made, driven by active market debates and numerous educational initiatives aimed at increasing awareness. Still, with just a few weeks before the deadline, financial entities and ICT providers must assess their current standing and identify the efforts required to bridge the gaps. Now is the time to prioritize, plan, and comply:

  • PRIORITIZE the gaps that need addressing
  • PLAN for tools and process improvements (extending beyond January 2025)
  • COMPLY with the deadline

Let’s take a step back to recap the scope and objectives of this EU regulation.

Scope: Harmonization and Augmentation

DORA introduces two key innovations:

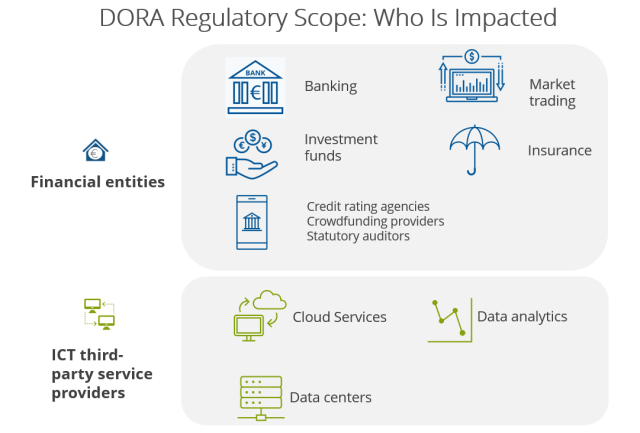
  • Harmonization: DORA harmonizes regulatory requirements across different financial industries, covering banking, insurance, capital markets players, and adjacent players such as credit rating agencies. This harmonization eliminates fragmentation across jurisdictions by implementing a regulation (not a directive), ensuring common requirements across all member countries.
  • Augmentation: DORA marks a paradigm shift, bringing ICT third-party providers under the direct scrutiny of the European Financial Supervisory Authorities. As previously discussed in our blog, EU regulators have acknowledged the growing dependency of financial organizations on ICT and cloud service providers. Given that digitalization and operational resilience are two sides of the same coin, implementing a robust digital operational resilience framework significantly enhances security for banking operations. By placing critical third-party ICT service providers under direct supervision, regulators have reshaped the dynamics between financial entities and their ICT partners.

For financial entities, DORA provides the framework for tighter collaboration with ICT partners to ensure end-to-end operational robustness. For ICT partners, DORA is not just a new regulatory burden, but an opportunity to deepen relationships with clients and explore new business avenues, as financial entities are required to conduct market research and define alternate solutions for each critical function.

Objectives: Mitigating Systemic Risk

The primary objective of DORA is to address the systemic risk posed by critical ICT service providers in the financial industry. By involving European supervisory authorities (e.g., EBA, ESMA, EIOPA) directly, regulators aim to mitigate this risk and enhance the overall digital resilience of the financial sector.

DORA’s requirements fall under five pillars:

  • Risk management
  • ICT third-party risk management
  • Digital operational resilience testing
  • Mandatory incident reporting
  • Voluntary information and intelligence sharing

Additionally, financial entities must define clear exit strategies to mitigate systemic risk in the event of operational issues with an existing ICT partner. Each entity must identify and choose alternative solutions and service providers to ensure the smooth transfer of critical services, if necessary.

For ICT vendors, DORA is a double-edged sword: While it opens up new opportunities and makes the market more fluid, it also imposes additional compliance obligations.

It is important to note that many DORA requirements are not new to large institutions, particularly significant banks subject to the ECB’s Single Supervisory Mechanism. The principle of proportionality still applies under DORA. Nonetheless, its impact is extensive, as evidenced by the IDC survey, wherein 38% of respondents cited digital operational resilience testing as their biggest challenge, while 33% identified ICT third-party risk management as a major hurdle.

Final Steps: Self-Assessment and Planning

With the deadline approaching, each institution must conduct a self-assessment to identify gaps. Where significant gaps remain, organizations must prioritize efforts to meet compliance requirements. Meanwhile, financial entities should plan for the adoption of new tools and processes, such as integrated procurement solutions, to enhance third-party governance and address DORA holistically as part of their ongoing journey toward digital operational resilience.


Are you ready for DORA? Discover the 10 critical steps financial entities must take before the regulation comes into effect in January 2025: IDC PlanScape: Last-Call DORA Compliance Checklist to Achieve Digital Operational Resilience

Maria Adele Di Comite - Research Director, IDC Financial Insights Corporate and Retail Banking - IDC

Maria Adele is Research Director for IDC Financial Insights European research team and is responsible for the IDC Financial Insights Corporate Banking Digital Transformation Strategies program. She has strong competencies in financial services strategy, cybersecurity, and regulatory evolution. She has been living and working in three different countries (Germany, Belgium, and Italy) and she speaks 5 languages. She is an expert in B2B business strategy, with significant experience in Financial Services, System Integration, and Consulting.

The time has come for the contact center and customer handling environment to jettison the term, ‘deflection.’  There is an inherent prejudice in the word when used in the context of customer service, that is, it is an operational view.   

The word itself comes with some psychological baggage. I hate to resort to the dictionary, but I must in this case, as it is illuminating. Deflect carries the meaning to ‘redirect from oneself blame or guilt.’ Ouch. Were the adopters of this word subconsciously interpreting a customer’s issue with a product as pointing blame at the organization for a deficient product?  Hmm.

Regardless of the underlying evolution, it’s time the industry stopped using this language in customer handling.  The idea of ‘deflection’ belies the thinking that it is very much a cost savings behavior; move this customer’s inquiry from the costly telephony agent channel to a less costly channel such as self-service or a digital channel. This thinking has no place in a customer handling environment.  

I’ve heard many arguments in support of the routing to alternative channels away from voice. Among them ‘customers like to help themselves,’ or ‘we are getting them to a channel where there isn’t a wait,’ and ’customers don’t like talking to an agent.’ It must be acknowledged that these assertions are partially true. With an increase in the volume of inquiries, the difficulty in hiring & training agents, and the high attrition rate of agents means that contact centers are always woefully understaffed and in a perpetual state of training. Providing alternative channels is a sound strategy. 

However, the idea that customers don’t want to talk to agents is not exactly true. IDC’s recent CX Path Survey, which surveyed individuals familiar with their contact center, gave some interesting insight into why customers choose agent-assisted channels such as Web chat, SMS and telephone. In the multi-response question 50.5% of the organizations indicated that ‘comfort with talking to a human’ was the number one reason for selecting an agent-assisted channel closely followed by ‘convenience’ at 47.3% and ‘complexity of interaction,’ at 43.1%.  While use of AI and automation can address aspects of ‘convenience’ and ‘complexity of interaction’ with channel availability and generative AI for specific content, replacing ‘comfort with talking to a human’ is more difficult. 

Another thought on the motivations behind ‘deflection;’ specifically cost savings. ‘Deflection’ to less costly channels may not be the panacea to the cost problem. Again, according to the IDC CX Path survey, 44% of the respondents indicated that on average their customers moved through three channels before achieving a final resolution to an issue. Of the respondent base 22.1% indicated two channels, 20% four channels and 8.4% five or more channels.  Astoundingly, only 3.2% of the respondents estimated that a typical customer used only one channel before reaching a resolution.  

Consider the customer’s perspective at the point they reach the resolution, either by themselves or with an agent after escalation. The customer has used a number of resources and still ultimately may have ended with an agent-assisted channel and potentially voice. There is a cost in this scenario in terms of customer tolerance/happiness etc., as well as the cost of putting these channels in place. 

What is my solution then? Don’t have multi-channels? Don’t move customers to other channels if agents will be the ultimate answer? No. Stop thinking about ‘deflection’ and focus on ‘the path of resolution’. I know, I know, everyone is trying to resolve problems. My thesis is to consider all channels part of the solution and leverage it as part of the journey. If a customer escalates, that isn’t a bad thing in and of itself. It is a bad thing if the flow through the channels wasn’t leveraged. Each channel should collect information that is context rich, and that context should move with the customer as they move across channels. Assume your customers are going to move through multiple channels. Each channel should perform its own triage so that when the customer reaches the agent, the agent is fully prepared to quickly help resolve the issue.

But what should the new word be that better represents a customer-centric viewpoint of the contact center?    

It needs to reflect:

  • You deserve our time. You paid money to us and bought our product; you have a right to service. This is a business transaction.
  • We want to help you. Really, you showed us your confidence in buying our product. We want to honor that.
  • We want to help you as quickly as possible, in the channel you prefer, at the time you prefer. At this moment, it is about you and not about us.
  • If you start with self-service, that is ok, but if it doesn’t resolve or satisfy your issue we will capture all that you have communicated and carry it along to the next channel with context to resolve the issue as quickly as we can.
  • If we do a good job in honoring our commitment to service a product that you deserve timely service on, then we hope to have earned your continued business. Only then does it become a ‘relationship.’ (Don’t get me going on loyalty.  That is one-sided. We’ll save that for another day.)

Back to the question of what to call it? What is a better name? We used to have What-You-See-Is-What-You-Get in publishing applications – WYSIWYG – it was pronounceable. 

  • Right-Channel-Right-Time – RCRT?
  • Efficient Handling?
  • Simply ‘Resolution?’

We’ll work on the name. Please send suggestions. The point is, deflection is out, and ‘positive customer handling with the customer in mind’ is in.

On October 3, I had the privilege of participating in a thought-provoking panel at DTX London 2024. The discussion revolved around one of the most pressing questions in the telecommunications industry: 5G versus Wi-Fi: Which technology will drive the future of connectivity?

As a 5G/mobility analyst at IDC in Europe, I was invited to join Paul Ridge, Director Consultant at 4C Strategies, and Dan Jones, Technologist at Hamina Wireless, to explore the opportunities, challenges, and future landscape of these two critical technologies.

The European Telecom Market: Facing Stagnation and Seeking New Growth

Before diving into the core debate, it’s essential to acknowledge the broader telecom market dynamics. The European telecom sector faces an array of challenges, including stagnating revenues, intensified competition from both traditional telcos and OTT players, and strict regulatory pressures.

Working closely with our telco colleagues around the world, IDC covers these issues across a range of research programs. As shown in IDC’s European 5G program (European 5G and Internet of Things Monetization and Adoption Strategies), price wars have squeezed margins, leaving telcos struggling to raise prices while shouldering the costs of 5G and fiber rollouts.

Telecom operators are pivoting toward service diversification, investing heavily in digital services, and shifting their strategies to seek new revenue streams beyond connectivity. This is where the conversation around 5G and Wi-Fi becomes especially significant.

5G: A Game-Changer for Telecoms

5G, particularly standalone (SA) networks, offers a lifeline for operators seeking to overcome revenue stagnation and expand into new business models. During the panel, I emphasized five key aspects of 5G SA that make it a cornerstone of future connectivity.

  1. Clean-Slate Architecture: 5G SA doesn’t rely on legacy technologies. This enables optimized network design, enhanced innovation, and greater flexibility.
  2. Cloud-Native Core: With a cloud-native foundation, operators can scale services dynamically, implement tailored network slices, and respond in real time to evolving user needs.
  3. Mobile Private Networks (MPNs): These enable businesses to deploy their own secure, private 5G networks that offer enhanced security, control, and reliability. MPNs also enable enterprises to run mission-critical applications independently from public networks.
  4. Network Slicing: This enables the creation of virtual, customized networks that cater to specific application requirements, such as ultra-reliable connectivity for autonomous vehicles or low-latency service for Smart Cities.
  5. Support for Key Traffic Types: The flexibility of 5G SA accommodates enhanced mobile broadband (eMBB), massive machine-type communications (mMTC), and ultra-reliable low-latency communication (URLLC), optimizing the network for a wide variety of use cases.

5G’s potential is immense — but its deployment in Europe has been slower than anticipated. To date, just 18 operators have launched 5G SA networks in Western Europe, and only a handful have commercialized network slicing capabilities.

Wi-Fi: The Complementary Force

5G offers compelling advantages, but Wi-Fi continues to be a dominant force, especially in residential and enterprise environments. The ubiquity of Wi-Fi, its ease of deployment, and lower cost make it an attractive option for fixed-location connectivity. However, Wi-Fi has limitations in mobility, security, and reliability — which is where 5G shines.

During the panel, we discussed how Wi-Fi remains ideal for specific customer requirements, such as indoor environments or smaller businesses with less demanding connectivity requirements. However, when mobility, low latency, and security are paramount, 5G emerges as the superior choice.

When 5G Outshines Wi-Fi

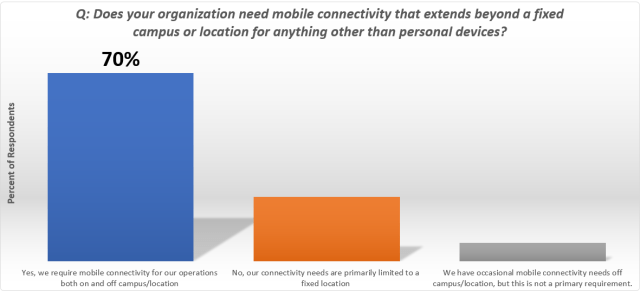
The results of IDC’s European 5G/IoT Survey 2024 highlighted that organizations are increasingly demanding mobile connectivity that extends beyond fixed locations. Nearly 70% of respondents said yes when asked, “Does your organization need mobile connectivity that extends beyond a fixed campus or location for anything other than personal devices?”

Businesses are looking for mobile solutions that enable them to monitor supply chains, manage remote operations, and ensure connectivity in dynamic environments.

Security remains a top concern, with 33% of survey respondents identifying enhanced security for data transmission and communication as their primary challenge. This has led to an increasing preference for keeping data in-house: Almost 49% of businesses cited trust and security concerns as a key reason for this choice.

This is where 5G MPNs come into play, offering businesses the security and control they need to manage sensitive data while generating new revenue streams through advanced digital services. According to IDC’s forecasts, the European MPN managed services market is expected to expand to a value of $818 million in 2028, with the MPN professional services market (including integration and consulting) projected to reach $615 million the same year.

In industries where deploying MPNs may not be feasible — such as public transportation or emergency services — 5G SA network slicing offers a flexible, secure alternative. With 5G network slicing, operators can create customized virtual networks, guaranteeing service-level agreements (SLAs) and ensuring reliable service for applications like connected ambulances or public transport vehicles. More than one-third (36%) of respondents in IDC’s European Telco Survey 2024 identified network slicing as a key driver of implementing 5G SA.

The reasons why businesses might choose 5G over Wi-Fi in certain campus or short-range scenarios include:

  • Security and End-to-End Control: 5G operates on licensed spectrum, offering higher levels of security compared to Wi-Fi, which uses unlicensed spectrum and is more vulnerable to interference and attacks. 5G networks enable operators to control and secure every part of the network from end to end, making it ideal for industries in which data protection is crucial.
  • Mobility: When mobility is important — such as in scenarios involving moving machines or vehicles — 5G excels due to its ability to maintain seamless connections during handovers between cells. Wi-Fi struggles with handover scenarios, leading to potential service drops when devices move across different access points. This makes 5G the better option for uninterrupted service in mobile environments.
  • Reliability in Aggressive Radio Environments: In radio-aggressive environments like factories, with machines and boxes creating interference, 5G’s micro-diversity and advanced signal handling capabilities make it more reliable than Wi-Fi. 5G’s ability to handle dark zones (areas with poor signal coverage) through reconfiguration also ensures consistent performance. Wi-Fi, however, may struggle in these areas.
  • Ability to Offer SLAs: 5G allows network operators to guarantee SLAs, providing commitments on performance, uptime, and latency. Wi-Fi cannot consistently offer these assurances. This is especially important in industrial applications requiring high reliability and low latency. 5G can provide predictable and measurable outcomes.
  • Control Over Different Parts of the Network: In 5G networks, operators have full control over network slices, traffic, and reconfigurations. This is essential in environments like manufacturing, where specific areas may need different levels of service or control. Customization at this level is difficult to achieve with Wi-Fi.

Blending 5G and Wi-Fi: The Future of Connectivity

Ultimately, the future of networking lies in the integration of 5G and Wi-Fi technologies. Each serves a distinct role in addressing the varying demands of consumers and businesses. Smartphones, for example, effortlessly switch between Wi-Fi and 5G depending on network quality, and this hybrid approach will likely become the norm across multiple industries.

Looking ahead, the combination of 5G’s robustness and Wi-Fi’s accessibility will enable a more flexible, efficient, and connected future. Telecom operators will continue leveraging both technologies to build the next generation of networks that deliver high-speed, secure, and reliable connectivity for all.


For more info on addressing growth in the telco space, please register for the following webcast: Addressing the telco growth imperative in EMEA

Masarra Mohamad - Senior Research Analyst, European 5G Enterprise Strategies - IDC

Masarra Mohamed is a senior research analyst specializing in analysing the connectivity and communications services markets, focusing on the changing networking requirements, trends, and competitive dynamics that support enterprises in their digital transformation. She explores how enterprise network strategies evolve to enable cloud, AI, and security.

Telcos in Europe, The Middle East, and Africa (EMEA) are coming under increasing investor pressure to deliver stronger growth. The average year-on-year (YoY) revenue growth rate among the “big 5” European telcos — BT, Deutsche Telekom, Orange, Telefonica, and Vodafone — in 2023 and the first half of 2024 was 0% and 1%, respectively.

The group of four leading Middle East and Africa telcos, namely Etisalat, MTN, Mobily and STC, are doing better, with a collective year-on-year revenue growth rate of 5% in H1 2024, but investors are noting that this is slower than their collective 9% year-on-year revenue growth in 2023.

What is going on here? First, the core telco business of providing network connectivity and communications services to consumers and business — which accounts for over four fifths of the revenues of most telcos — is challenged by a new breed of competitors. Users increasingly rely on the more convenient MS Teams and Zoom apps for their business calls, and WhatsApp or Viber apps for their personal calls and messages, which is hurting telco revenues.

And a whole host of disruptive players are challenging telcos’ broadband and enterprise networking business, from new entrant fibercos offering full fiber at attractive prices to consumers and small businesses to systems integrators pitching SD WAN and private 5G solutions to large enterprises.

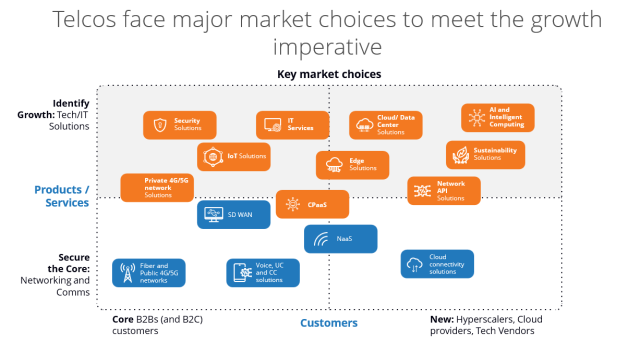
Second — and more important — is the fact that EMEA telcos’ efforts to expand into “beyond connectivity” solutions have not had a major impact on the growth needle so far. Telcos have a bewildering range of market positioning, customer, and technology choices to make in this area, as we show in this diagram:


From a customer perspective, telcos need to not only find ways to serve existing consumer and business customers better, but they also need to consider targeting new customer segments in the broader ICT ecosystem. But the real maze of choices is in the top part of this growth diagram, where telcos need to decide if and how they play effectively in technology areas such as security, CPaaS, cloud/datacenter, and sustainability.

The complexity is compounded by the myriad of sub-segment (i.e., IoT software and services versus IoT connectivity), vertical (manufacturing versus healthcare), and geographic considerations.

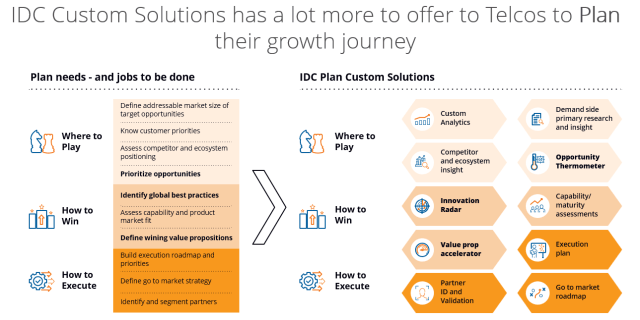
As it stands, telcos need to address dozens of “where to play,” “how to win,” and “how to execute” jobs to be done — and do these extremely well — as they seek to address the growth imperative, illustrated on the left-hand side of the diagram below:

And yet, there are three big jobs that telcos need to do particularly well:

  • Prioritize Growth Opportunities: No telco will have the capacity to address every segment in every solution box outlined in the growth matrix above, so either/or choices will have to be made.
  • Identify and Incorporate Global Best Practices: Telcos do not need to reinvent the wheel in each of the adjacent growth opportunities, innovative solutions by both telcos and non-telcos across the world offer valuable lessons for those willing to look.
  • Define Winning Value Propositions: Telcos often have good value propositions in a range of “beyond connectivity” areas, but crucial ingredients that would make them great and irresistible to clients are often lacking.

IDC can help telcos address these critical growth jobs to be done with three well-established custom solutions:

  • IDC’s Opportunity Thermometer helps CSPs identify, select and prioritize the best and most attractive growth opportunities within or outside current product and geographic markets — that are within client’s capabilities to exploit.
  • IDC’s Innovation Radar helps CSPs identify and integrate inventive best practices and/or value propositions — and leverage the insights from these to accelerate revenue growth and boost customer loyalty.
  • IDC’s Value Prop Accelerator solution helps CSPs build or validate winning value propositions in target growth areas that often sit outside the connectivity and communication perimeter (e.g., cloud, security, APIs).


Should you wish to learn more about these and other IDC Custom Solutions, please get in touch.

For more info on addressing growth in the telco space, please register for the following webcast: Addressing the telco growth imperative in EMEA

Angel Dobardziev - Senior Consulting Director, European Consulting - IDC

Angel Dobardziev is a senior director, consulting, for IDC’s European Telecoms, IoT, and Infrastructure Groups. Based in London, Dobardziev works with IDC’s clients to define and deliver custom advisory solutions to their critical business and technology problems. Angel has consulted for global technology vendors and service providers on a range of areas including recent work on 5G, IoT, and cloud services. Recent engagements include extensive work for a global mobile operator trade body on developing its 5G program, helping to develop its in-depth (300 page) 5G Operator Guide, and more recently, its 5G Cost Optimisation study. He also led an engagement assisting a global mobile operator with its IoT go-to-market strategy, as well as numerous projects for a tier one software vendor supporting its on-premise-to-cloud migration strategy.

State of the India Smartphone Market

India ships around 145-150 million new smartphones per year for the domestic market, ranking it second globally after China in annual shipping volume. There are approximately 650 million smartphone users in India or about 46% smartphone penetration in the country. There is no other market of this size with such huge untapped potential, making India a very attractive market for all smartphone ecosystem participants from brands to component makers.

India’s smartphone market grew modestly in 2021, coming out of a challenging 2020 (due to pandemic-led shutdowns). This growth was driven by the need of a better device for remote learning/work and increasing media consumption on the go. However, in 2022 and 2023 the market faced challenges because of the rising average selling price (ASP) for devices (growing by a CAGR of 38% from 2020 till 2023), improving device quality, and continuing income stress especially in the mass consumer segment. This in turn has elongated the average smartphone replacement cycle in India from 24 months to almost 36 months currently, further restricting the growth of the new smartphone market.

Why Are Consumers Choosing Used Smartphones?

All the above mentioned factors are contributing to the increasing popularity of used smartphones in the past few years. As the quality of smartphone hardware improves, increasing device prices are keeping the new smartphone models out of reach of the mass segment. The aspiration to own a good device without paying much is making the used smartphones a very attractive choice for consumers wanting to upgrade or even with first-time smartphone users.

Another important factor in the popularity of used smartphones is the rising preference for 5G smartphones. As of now only approximately a third of the 650 million Indian smartphone users have a 5G smartphone, the rest are still using 4G phones.  However, the price differential between 4G and 5G smartphones and the lack of wide availability of 5G models under INR 10K (US$125) is restricting their upgrade to a 5G device thus forcing many consumers to go for mid-priced used smartphones.

According to the latest IDC research (IDC Used Device Tracker), India ranks third globally in used smartphone units’ annual volume after China and the USA, and is one of the fastest growing markets.  In 2024, IDC forecasts 20 million used smartphones will be traded in India with a YoY growth of 9.6%, outpacing new smartphone shipments of 154 million units in 2024, growing at 5.5% YoY.

Apple and Xiaomi Are the Top Choices!

The “premiumisation” of India’s smartphone market or more aptly the rising aspirations of the Indian consumer to upgrade to a mid-premium or a premium phone is also contributing to the popularity of used smartphone space. While Apple has seen healthy growth of new iPhone shipments in India in the past few years, it is also leading the used smartphone space, capturing a quarter of the market as per IDC Quarterly Used Device Tracker. Everyone in India wants to buy an iPhone because of its premium brand positioning and status signaling value, but not everyone can afford one. The used phone market comes to the rescue of many such aspirational consumers going for previous gen models like iPhone 11, 12 and 13 series.

Xiaomi led India’s new smartphone market for 20 straight quarters from 3Q17-3Q22. As a result, it has a huge user base which is reflected in the used smartphone market as well. Xiaomi sits at the second position followed by Samsung. These top 3 brands combined make up around two-thirds of the used smartphone market in India.

Who are the Market Players?

IDC’s used smartphone research tracks both second hand and refurbished smartphones being traded via organized refurbished players in the market. It excludes the peer to peer sales. In India, several startups in this space like Cashify, Budlii, Instacash, Yaantra, etc. have tried to organize this hitherto largely unorganized market. With their efforts around marketing and omnichannel presence across both online and offline counters, these players have been able to build confidence and trust among consumers regarding the quality of the used smartphones on their platforms.  Cashify is one of the biggest platforms in this market with over 200 stores in 100 cities, many in Tier 2 & 3 towns.

For Yaantra, the company is owned by Indian e-commerce giant Flipkart, with branding named as Flipkart Reset. It is mainly focused on its online portfolio. For offline space, the company has partnered with Airtel to be available in the telco stores in only two Indian cities for now (Delhi & Hyderabad).

From Here, the Only Way Is Up!

IDC forecasts the used smartphone market in India to grow at 8% CAGR in the next 5 years, reaching 26.5 million units per annum in 2028.

It is evident that the used smartphone market in India is gradually taking shape with interesting channel play by key trading players making smartphones more affordable to a larger audience. This is also reassuring for the ever-discerning Indian consumer when they explore buying a used smartphone without worrying about the quality of the device and spending too much.

From an overall market perspective, growth in used smartphone market in India can certainly be a factor in increasing smartphone adoption in India, creating a parallel revenue stream for channel players, help vendors in addressing e-waste concerns around discarded devices, and generate employment (skilled/unskilled).

This market can certainly play a major role in achieving the goal of bringing a billion Indians in the smartphone fold in the next few years.

Navkendar Singh - Associate Vice President - IDC

Navkendar Singh is a Associate Vice President with IDC India, based in Gurgaon. His research domains encompass deep-dive research and insights in and around mobile devices, smart homes, PCs, tablets, wearables, and the printing market in India, Bangladesh, and Sri Lanka. He is also involved in building IDC's successful channel research programs for these domains at city and state levels. Navkendar also leads research related to analyzing the role of devices, emerging business engagement models, the impact of emerging technologies on devices, and emerging personas related to Future of Work.

The deployment of 5G networks has reached a crucial point: We now have spectrum assigned, rollouts are nearly complete, devices are 5G compatible, and 5G Standalone (SA) is gaining ground.

Uncertainty remains, however, regarding monetization. The telecommunications sector is still searching for innovative use cases that can justify the massive investment. Finding that definitive “killer” use case has not been easy.

We need to understand, however, that 5G isn’t about a single blockbuster application. Instead, it’s about enabling multiple opportunities in a dynamic ecosystem where technologies like OpenAPIs will play a key role in success.

Show Me the Use Case — Where’s the Killer App?

Historically, each new generation of networks has been driven by a killer app that fueled its adoption. 2G was driven by voice, while 3G and 4G saw data and mobile browsing become the catalysts.

But with 5G, the industry is learning there won’t be a single, all-encompassing app to justify the investment. Such a mindset no longer applies.

With 5G, we aren’t looking for an application that will endure for decades. Instead, we need a network that enables a flexible range of services that can evolve over time.

The Real 5G Use Case: Flexibility and OpenAPIs

The true value of 5G lies in its flexibility. What’s pivotal isn’t a killer app but an infrastructure that can capitalize on a continuous flow of opportunities.

This is where innovation driven by network OpenAPIs comes into play. These open interfaces allow operators to provide a technological foundation on which third parties can build and monetize their services, creating a far more dynamic and diversified ecosystem.

Recently, Ericsson, in collaboration with 12 leading global operators, launched a joint initiative to enable the commercialization of network OpenAPIs, further solidifying their role in shaping a dynamic 5G ecosystem. This collaboration aims to redefine the industry by creating open interfaces that allow third parties to develop, deploy, and monetize their services on 5G infrastructure.

By fostering interoperability and innovation, this initiative positions OpenAPIs as a critical enabler for unlocking the full potential of 5G, allowing businesses across industries to tailor solutions that maximize their 5G investments.

Network OpenAPIs enable businesses to develop specialized, customizable solutions tailored to specific needs across industries such as manufacturing, healthcare, smart ports, and logistics. The key is that this ecosystem of services can be monetized collectively, allowing 5G networks to capture value from multiple sources simultaneously.

5G: A Technology for the Enterprise World

5G is primarily designed for the enterprise world, in which each company has unique requirements and seeks differentiation in the market. This creates the scenario in which a single use case may not justify the investment.

Companies must therefore leverage 5G and OpenAPIs to deploy tailored solutions that meet their specific needs. A hospital, for example, will have entirely different latency and reliability requirements than a factory or a smart port.

It’s 5G’s ability to meet these demands that brings real value. The possibility of real innovation lies in the ability of 5G networks to adapt to the specific challenges of each business sector and to do so in a scalable, flexible manner.

This agility is central to monetization, as it allows for the creation of custom solutions in an ecosystem that’s constantly evolving.

Enabling Technology: The Challenge and the Opportunity

We need to keep in mind that 5G is an enabling technology. This sets it apart from previous network generations. Instead of being the direct star, its success depends on services and solutions that can take advantage of its capabilities.

Here, OpenAPIs play a fundamental role: They allow businesses to integrate with the network and create their own applications using the operator’s infrastructure as a platform. The success of enabling technologies will be directly proportional to how easy they are to implement and how well they connect with customer needs.

5G monetization will not rely on finding a killer app but rather on enabling an ecosystem in which multiple services can thrive simultaneously. Collaboration between operators and developers is critical to unlocking the value of 5G.

OpenAPIs enable precisely this. They open access to the infrastructure, allowing each industry to design and deploy its own solutions.

The Key to Monetization: A Shift in Mindset

Successfully monetizing 5G requires a shift in mindset on how networks are operated and monetized. It’s no longer about searching for a central application to justify the investment, but about creating a flexible architecture, supported by OpenAPIs, that enables companies to innovate and fully leverage 5G’s capabilities.

This change is already happening. Complementary technologies such as GenAI and edge computing are accelerating the transformation.

As organizations adapt to this mindset, they will identify and capitalize on real-time opportunities. At that point, the flexibility and service ecosystem enabled by OpenAPIs will unlock the true monetization potential of 5G.


For more info on addressing growth in the telco space, please register for the following webcast: Addressing the telco growth imperative in EMEA

Alejandro Cadenas - Associate Vice President - IDC

Alejandro Cadenas leads the European Telco Mobility unit, comprising the CISs European 5G Monetization and Adoption Strategies, European Consumer Telecoms Strategies, and European Internet of Things Ecosystem and Trends. The focus of these three programs is to address the Monetization strategies, best practises, challenges and recommendations for all players across the telecom sector. The key areas addressed include, but are not limited to, OpenAPis monetization, 5G monetization in the Enterprise (Mobile Private Networks, Slicing) and Consumer (digital products categories) segments, Partnerships, Commercial stratregies, key customers and pain points, LEO satellite connectivity, Mission Critical systems, as well as all strategies to take these to the market.

Regulations Are Reshaping the Way Companies Transact with Each Other

In the first blog of our e-invoicing series, we explored the pivotal role of e-invoicing in pioneering the transformation of business-to-business (B2B) transactions. This foundational piece highlighted how e-invoicing is reshaping the landscape of business interactions by streamlining processes, enhancing accuracy, and driving efficiency. In the current post, we delve deeper into the regulatory frameworks influencing these digital transformations, examining the opportunities and challenges that arise as businesses adapt to evolving compliance requirements.

The Emergence of a New Transaction Ecosystem

After decades of paper-based dominance, business-to-business transactions are digitalizing and digitally transforming. e-Invoices and digital networks are streamlining accounts payable and receivable processes, enhancing efficiency and accuracy. Transactions are also becoming enriched with data, especially to display sustainability-related information.

Prompted by new regulation, digital-first thinking, and good corporate governance, businesses are changing how they collaborate and transact. This presents an opportunity for vendors to develop innovative solutions that meet the needs of today’s B2B landscape.

Regulators face the constant challenge of implementing measures that ensure market integrity, consumer protection, and alignment with public interests, while simultaneously fostering innovation and economic growth.

Regulations and the Burden of Responsibility

Reducing costs and improving efficiency are constant concerns for businesses. Companies explore every avenue to achieve these goals, from leveraging technology to optimizing workflows.

However, businesses must also contend with numerous external factors that can influence their operational effectiveness. Regulations are one of these external factors. Enterprises and their leadership are entrusted with the responsibility of ensuring compliance, which requires investments in personnel, technology, and training — oftentimes, all three.

Personnel

To stay compliant with evolving laws and regulations, companies must proactively recruit, train, and retain specialized personnel. These experts ensure adherence to current legal frameworks and monitor upcoming changes, like the introduction of new regulations or amendments to existing ones.

For example, the General Data Protection Regulation (GDPR) mandates that companies handling large volumes of personal data appoint a Data Protection Officer (DPO).  Highly regulated industries like banking and healthcare often require multiple layers of compliance personnel throughout their organizations, in addition to industry-specific regulations and overarching ones.

As digital businesses increasingly rely on complex technologies, leadership must ensure their workforce possesses the necessary skills to navigate both current and future regulatory landscapes. This involves establishing management structures that can anticipate staffing needs and strategically invest in technology and training to maintain compliance. Public and private companies have distinct compliance needs and requirements. While technology can assist in meeting these needs, it cannot replace dedicated teams responsible for ensuring operational compliance. That is why technology and training is so important.

Technology

Technology and regulations are intertwined, existing in a state of interdependency with stronger linkages than often recognized. Regulators face the constant challenge of fostering innovation and economic growth, simultaneously safeguarding consumers and the public interest. This requires ongoing assessment of the benefits and drawbacks that new technologies bring to society.

In the European Union (EU), policymakers understand the importance of this dynamic and actively foster dialogue and collaboration between regulators, industry leaders, enterprises, technology experts, and vendors. To facilitate change management within organizations when it comes to regulation and technology, the EU provides support and self-service tools.

This collaborative approach is crucial, because while regulatory changes drive transformations in business-to-business transactions, technology provides the tools and solutions for effective compliance.

By understanding and proactively adapting to this interplay, businesses can leverage technological advancements to navigate the evolving landscape of B2B transactions and gain a competitive advantage. Vendors will play their part by supporting their clients in ensuring that they bring the right systems online at the right time.

Training

Sustainable compliance requires more than just training; it demands a culture of open communication and employee empowerment. Management must proactively inform employees about evolving regulations and the rationale behind them, providing the necessary resources and support to adapt without disrupting workflows.

Ensuring that the training covers both the law and technologies that are either being regulated or used to ensure regulation is key. This transparent approach fosters trust, reduces resistance to change, and enables employees to confidently contribute to a compliant organization.

Regulators must ensure a level playing field for businesses of all sizes, as multinational corporations have greater resources to invest in compliance compared to smaller enterprises. While not always perfect, European regulators have been leaders in promoting inclusive dialogue and collaboration among stakeholders to address these challenges.

Regulation as an Innovation Driver in B2B

At first glance, new invoice-related regulatory changes may easily be perceived as an added burden, however, within these changes there exists a significant area of opportunity if organizations successfully broaden the scope to include finance process improvements.

e-Invoicing could serve organizations as a catalyst for organizations to spearhead the introduction of more efficient practices for finance departments, facilitated through process automation.

Additional protocols in B2B document exchanges, particularly invoices, increase data accuracy while reducing manual intervention, which then enhances operational efficiency.

Fraud prevention

e-Invoicing unlocks new potential for tax authorities to combat value added tax (VAT)- related fraud, addressing the blind spots for VAT evasion and avoidance. The starting point for EU tax authorities begins with invoking greater controls in monitoring the integrity of VAT data being reported by organizations. For this tax enforcement modernization effort to serve its true purpose, several European tax authorities are establishing their own document exchange screening and approval processes, commonly referred to as continuous transaction control (CTC).

This is an important step in the future of the transaction that veers towards creating transparency and mitigating fraud at the point of the transaction. This involves new technical elements requiring organizations to submit invoices to designated regulatory platforms for approval prior to delivery to the end recipients.

Audit readiness

An advantage for both organizations and tax administrations that arises through e-invoicing is advanced audit readiness.  European governments are tasked with, among other things, implementing two of the common transaction control models: the post-audit and clearance models.

Each having their own benefits, tax authorities will have more control in performing audits at will. Previously performed solely after the event, tax authorities that have adopted clearance models are able to carry out audits in real-time and/or upon request for each transaction. This removes the need to request and wait for information from taxpayers. Some European tax authorities are using this as an opportunity to explore new ways of incentivizing organizations.

For example, the Italian government initially introduced e-invoicing for B2G transactions in 2014; now it has gone on to introduce remote audit checks that will lower government interference with tax remittances for B2B exchanges.

Organizations looking to deploy e-invoicing will need to overcome significant hurdles such as breaking down data silos, improving data quality and consistency, and, in some instances managing high volumes of complex data, to avoid non-compliance penalties

Conclusion

As the landscape of B2B transactions evolves under the influence of new regulations, businesses must embrace the opportunities presented by e-invoicing and digital transformation.

This transition not only meets compliance needs, but also drives efficiency and innovation within organizations. Businesses must actively leverage the interconnectedness of technology, personnel training, and regulations to shape the future of transactions and drive growth.


Ready to elevate your solutions and empower your teams? Contact us for a deeper dive on how IDC can help.

As generative AI (GenAI) continues to disrupt various industries, its impact on cybersecurity has become a central topic of discussion. With the power to transform threat detection, response strategies, and overall security posture, GenAI introduces both significant opportunities and complex challenges.

This blog delves into five critical questions about how GenAI is reshaping cybersecurity analytics, offering insights for organizations looking to navigate this evolving landscape.

1. What Makes GenAI Different from Traditional AI in Cybersecurity?

Artificial Intelligence has long been a cornerstone of cybersecurity, driving significant advancements in threat detection, endpoint protection, and automated responses. Traditional AI systems excel at analyzing historical data, identifying patterns, and detecting anomalies based on past behaviors. These capabilities have been instrumental in helping organizations fend off cyber threats by anticipating actions that mimic known attack signatures.

However, GenAI represents a new frontier in AI capabilities, fundamentally altering how cybersecurity operates. Unlike traditional AI, which is reactive, GenAI can generate new data, content, and even potential attack vectors in real-time. This shift means that GenAI can be leveraged to create highly personalized phishing attacks, automate the generation of sophisticated malware, and simulate complex cyber-attacks with unprecedented precision.

For instance, traditional AI might analyze email traffic to identify potential phishing attempts based on known patterns. GenAI, on the other hand, could create entirely new and convincing phishing emails tailored to individual targets, making it much harder for employees to discern legitimate communications from malicious ones. This ability to generate novel content on the fly dramatically increases the challenge for cybersecurity teams, who must now defend against threats that have never been seen before.

In essence, GenAI is not just an evolution of existing AI technologies but a transformative force that introduces new dynamics into the cybersecurity landscape. It offers defenders powerful tools for proactive security measures but also empowers attackers with enhanced capabilities, necessitating a rethink of traditional defense strategies.

2. Does GenAI Favor the Attacker or the Defender?

In the ongoing battle between attackers and defenders in cybersecurity, GenAI appears to have initially tipped the scales in favor of the attacker. The inherent asymmetry in cybersecurity—where attackers need to succeed only once, while defenders must protect against every possible threat—becomes even more pronounced with the introduction of GenAI.

Attackers can exploit GenAI to conduct volume attacks, generating countless variations of malware, phishing campaigns, and other cyber threats with minimal effort. This capability allows them to overwhelm traditional defenses, which may not be equipped to handle the sheer volume and diversity of attacks that GenAI can produce. For example, GenAI can create hundreds of phishing email variations, each slightly different, making it difficult for automated filters to catch them all.

Moreover, GenAI enhances the precision of these attacks. By ingesting large datasets, GenAI can tailor attacks to specific individuals or organizations, increasing the likelihood of success. For instance, a GenAI-powered attack might analyze social media profiles, public records, and previous interactions to craft a highly personalized phishing email that is nearly indistinguishable from legitimate communication.

Another area where GenAI gives attackers an edge is in the realm of endless simulation. Attackers can use GenAI to simulate defenses, testing various attack strategies in a controlled environment before launching them in the real world. This capability allows them to refine their tactics, identify potential weak points in a target’s defenses, and optimize their attacks for maximum impact.

However, defenders are not without recourse. To counter these sophisticated threats, defenders must harness GenAI’s capabilities for their own advantage. This involves leveraging GenAI for advanced threat detection, dynamic risk assessment, and automated response strategies. For instance, defenders can use GenAI to analyze network traffic in real-time, identifying and mitigating threats as they emerge.

The challenge for defenders is to stay ahead of the attackers in this rapidly evolving landscape. This requires a proactive approach, continuous adaptation, and a deep understanding of how GenAI can be both a tool and a weapon in the cybersecurity arsenal.

3. What Are the Biggest Challenges of Implementing GenAI in Cybersecurity?

While the potential of GenAI in cybersecurity is immense, its implementation comes with a host of challenges that organizations must navigate carefully. One of the primary concerns is data privacy and security. GenAI systems require vast amounts of data to function effectively, and this data often includes sensitive information such as personally identifiable information (PII), proprietary corporate data, and intellectual property.

The collection, storage, and processing of this data introduce significant risks. If not managed properly, there is a danger that this data could be misused, exposed, or even compromised by malicious actors. For instance, a breach in a GenAI system could potentially expose not just the data it was trained on but also the AI models themselves, leading to a cascade of security issues.

To mitigate these risks, organizations must implement robust data governance policies. This includes ensuring that data is anonymized where possible, implementing strict access controls, and regularly auditing data usage to ensure compliance with regulatory requirements. Additionally, organizations must be transparent with stakeholders about how their data is being used by GenAI systems, addressing any concerns about privacy and security.

Another significant challenge is the accuracy and reliability of GenAI outputs. Unlike traditional AI systems, which are designed to recognize patterns in existing data, GenAI creates new content based on its training data. This means that if the training data is incomplete, biased, or otherwise flawed, the outputs of the GenAI system can be inaccurate or misleading.

For example, a GenAI model trained on biased data might produce skewed threat assessments, leading to false positives or, worse, false negatives that leave critical threats undetected. The phenomenon of “hallucinations,” where GenAI fills in gaps with incorrect information, further complicates matters. In a cybersecurity context, this could result in flawed defense strategies or misguided responses to perceived threats.

To address these challenges, organizations must implement continuous monitoring and validation of GenAI outputs. This involves regularly testing the AI models against known benchmarks, auditing the decision-making processes of the AI, and ensuring that human experts are involved in reviewing and validating critical outputs. The concept of “human in the loop” is particularly important here, as it allows organizations to combine the speed and efficiency of GenAI with the judgment and experience of seasoned cybersecurity professionals.

Finally, the cost associated with implementing and maintaining GenAI solutions can be a significant barrier. GenAI systems require substantial computational resources, including powerful hardware, vast amounts of storage, and advanced software tools. Additionally, the ongoing costs of supporting these systems—such as updates, model retraining, and data management—can strain IT budgets.

Organizations must carefully weigh the costs and benefits of GenAI adoption, considering not only the immediate expenses but also the long-term implications for their cybersecurity strategy. In some cases, the investment in GenAI may be justified by the potential for enhanced security and operational efficiencies, while in other cases, it may be more prudent to focus on optimizing existing AI systems.

4. Will the Adoption of GenAI-Powered Cybersecurity Products and Procedures Happen Rapidly?

The adoption of GenAI in cybersecurity is likely to follow a pattern of slow initial uptake followed by rapid acceleration. Early adopters, particularly large enterprises and tech-savvy organizations, are already integrating GenAI into their security frameworks. These early implementations focus on tasks such as automated threat detection, natural language processing for security logs, and predictive analytics.

However, several factors will influence the pace of broader adoption. Trust in GenAI’s outputs is paramount—organizations need to be confident that the AI’s decisions are accurate, reliable, and free from bias. This trust must be built through transparency, rigorous testing, and clear communication about how GenAI systems work and how decisions are made.

The cost of implementation is another critical factor. As mentioned earlier, GenAI systems require significant investment in hardware, software, and ongoing support. For many organizations, particularly small and medium-sized enterprises (SMEs), these costs may be prohibitive. However, as the technology matures and economies of scale take effect, the costs are expected to decrease, making GenAI more accessible to a wider range of organizations.

The ability to integrate GenAI with existing security infrastructures will also play a significant role in adoption. Many organizations have already invested heavily in traditional AI and cybersecurity tools, and they may be hesitant to replace or overhaul these systems. However, as GenAI demonstrates its value—whether through enhanced threat detection, faster response times, or improved operational efficiencies—organizations are likely to increasingly embrace it as a complement to their existing security measures.

Regulatory compliance is another area that will impact the adoption of GenAI. As governments and industry bodies begin to regulate AI use, particularly in sensitive areas like cybersecurity, organizations will need to ensure that their GenAI implementations comply with these regulations. This could include requirements around data privacy, transparency, and accountability, as well as specific guidelines for how AI systems should be tested and validated.

Cyber insurers will also play a crucial role in determining how quickly GenAI is adopted. If insurers begin to offer lower premiums or more comprehensive coverage to organizations that use GenAI-powered cybersecurity tools, this could incentivize broader adoption. Conversely, if insurers view GenAI as introducing new risks, they may increase premiums or impose stricter conditions on coverage, potentially slowing down adoption.

As more GenAI-powered products become available, we can expect a surge in adoption as businesses seek to capitalize on the efficiencies and enhanced capabilities that GenAI offers. However, this will require a careful balance between innovation and risk management to ensure that GenAI is deployed safely and effectively.

5. What Role Will Trust Play in the Future of GenAI in Cybersecurity?

Trust will be the cornerstone of any successful GenAI implementation in cybersecurity. Organizations must not only trust that the data being used by GenAI systems is handled securely but also that the AI-generated insights and outputs are reliable, accurate, and free from bias. In an environment where false positives can lead to wasted resources and false negatives can result in catastrophic breaches, establishing this trust is paramount.

Data Privacy and Security
One of the primary concerns with GenAI is the handling and treatment of data. Cybersecurity professionals need to ensure that sensitive information, including personally identifiable information (PII) and proprietary corporate data, is protected when used by AI systems. In this context, cybersecurity vendors must be transparent about how data is processed, stored, and managed. If a third party manages a GenAI system, what happens to the data it handles? Is it stored securely? How is it used in future iterations of the AI model? These are critical questions that organizations must address to maintain trust in the system.

In addition, the potential for exposing sensitive data through poorly governed AI systems could lead to severe regulatory consequences, reputational damage, and financial losses. The role of robust data governance and strict adherence to compliance standards will become increasingly important as organizations integrate GenAI into their cybersecurity workflows.

Accuracy and Reliability of AI Outputs
Trust also hinges on the accuracy of GenAI’s outputs. GenAI models are probabilistic, meaning they generate outputs based on likelihoods, not certainties. This can introduce errors, especially when the underlying data is incomplete or biased. In cybersecurity, where precision is critical, the risk of AI-generated “hallucinations”—outputs that are not grounded in factual data—can have serious implications. These hallucinations could lead to misidentification of threats, incorrect incident responses, or overlooked vulnerabilities.

To mitigate these risks, organizations must implement processes that ensure the continuous auditing, testing, and validation of GenAI outputs. This is where the concept of “human in the loop” becomes essential. While GenAI can rapidly process and analyze vast datasets, it is vital that human experts remain involved in reviewing and validating its findings. Cybersecurity professionals bring context, judgment, and experience that AI models lack, making their oversight crucial to ensuring that GenAI’s decisions are sound.

Transparency and Governance
Another critical component of trust is transparency. Organizations using GenAI must have visibility into how the AI systems make decisions. Gone are the days of “black box” AI, where models operate in a vacuum without explanation. Today, cybersecurity professionals expect to understand the logic behind AI outputs, especially when these outputs are used to inform critical security decisions.

GenAI vendors must prioritize transparency, offering clear insights into how their models function, how data is used, and how conclusions are reached. This level of visibility allows organizations to audit AI-driven decisions, identify potential flaws in the system, and continuously refine their models to improve performance.

Building Long-Term Trust
Trust in GenAI is not a one-time achievement but an ongoing process. As AI systems evolve and learn, so too must the frameworks for monitoring and governing their use. Organizations that invest in strong governance models, foster a culture of transparency, and integrate human oversight into their AI processes will be better positioned to harness the full potential of GenAI while minimizing its risks.

Conclusion: Navigating the GenAI Frontier in Cybersecurity

Generative AI represents a transformative force in cybersecurity, offering unprecedented capabilities to enhance threat detection, response strategies, and overall security posture. However, with these advancements come significant challenges that must be carefully managed. Organizations must weigh the benefits of GenAI against the risks it introduces, particularly when it comes to data security, trust, and the evolving dynamics between attackers and defenders.

By addressing the five critical questions outlined in this blog, businesses can better prepare for the future of GenAI in cybersecurity. They must recognize that while GenAI offers immense potential, its success depends on robust data governance, transparency, continuous oversight, and the integration of human expertise. The future of cybersecurity will be shaped by how well organizations can balance innovation with the responsibility of safeguarding their digital environments.

The key takeaway is clear: GenAI is a powerful tool, but it must be implemented with care. As we move into an era where AI-driven solutions become increasingly central to cybersecurity strategies, businesses that prioritize trust, transparency, and collaboration between human and machine will be the ones that thrive in this new frontier.

This blog is based on the latest IDC Research on cybersecurity and GenAI. We recommend the following resources for more information on the latest trends in cybersecurity:

To access more insights and would like to learn more about the benefits of IDC and how our IT Executive Programs can help you with your IT strategy, implementation, and digital transformation, click the button below.

Learn what matters most to your customers with IDC’s AI Use Case Discovery Tool—find out more.