第三季度中国平板市场出货量同比下降22.3%,成本压力加速向需求端传导,市场调整幅度进一步扩大。消费市场受涨价影响持续收缩,商用市场则在需求前置后逐步回归常态,厂商竞争及市场需求结构也随之发生变化。

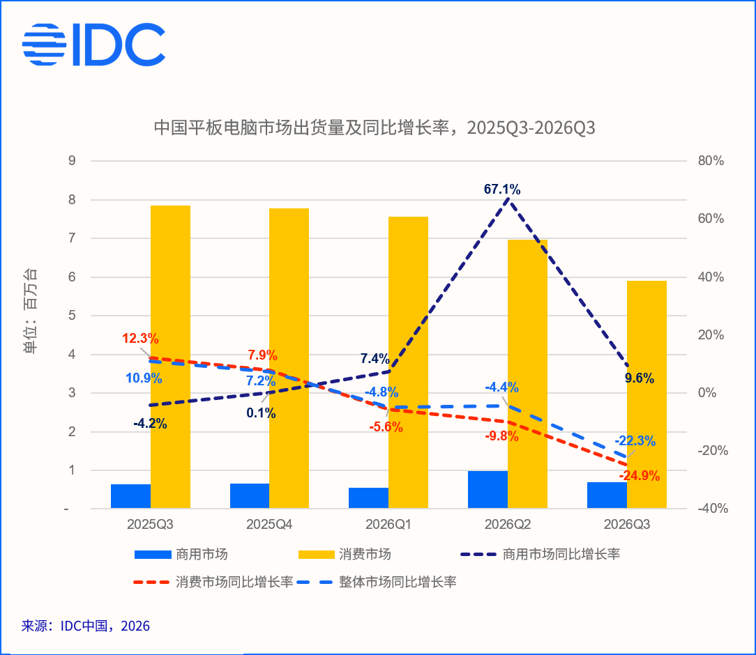
国际数据公司(IDC)发布了2026年第三季度中国平板电脑市场季度跟踪报告。数据显示,2026年第三季度,中国平板电脑市场出货量为660万台,同比下降22.3%。伴随成本上涨压力充分向销售端传导,市场出货量降幅较上半年显著扩大,单季度出货量在连续12个季度后首次低于700万台,降幅也创下2020年第一季度新冠疫情以来的最大值,市场首次迎来同比双位数下滑。

从市场表现来看,第三季度有三个值得关注的变化:一是消费与商用市场的表现背离仍在延续,但商用市场增长恐难持续;二是头部厂商格局相对稳定,中游厂商份额继续提升;三是成本上涨推动市场需求加速分化,入门级市场收缩与中高价位段升级同步发生。
消费市场涨价导致销量折损,商用市场库存补充进入尾声

2026年第三季度,中国消费与商用平板市场出货量继续呈现背离趋势。消费平板出货量同比下降24.9%,伴随头部厂商接连上调产品售价,市场均价环比提升8.6%,价格上涨对消费者购买意愿的抑制进一步显现。

商用平板市场出货量同比增长9.6%。作为教育行业需求高峰期,7、8月厂商继续加码教育市场布局,但9月需求已明显减弱。与此同时,华为、荣耀自7月起上调商用平板售价,也对后续市场需求带来压力。随着前期需求前置及渠道库存补充逐步进入尾声,商用市场增长势头预计难以延续。
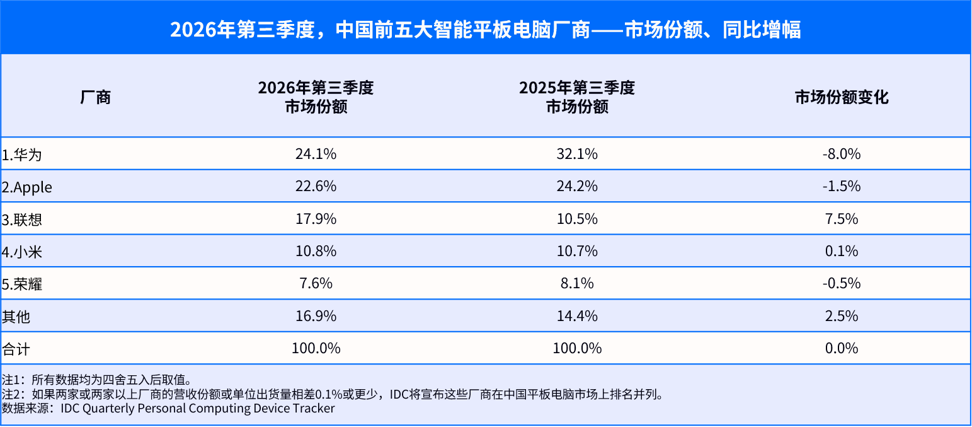
竞争格局稳中有变,厂商持续调整产品布局以缓和涨价压力、寻求增长轨道

2026年第三季度,中国平板市场前五厂商排名与上一季度保持一致,但中游集团市场份额继续提升。成本上涨背景下,厂商在产品结构、渠道布局及价格调整节奏上的差异进一步显现。

  • 华为继续位列市场第一。尽管其消费及商用平板均迎来较大幅度的价格上调,但凭借鸿蒙生态互联能力、品牌影响力及完善的渠道布局,华为仍保持市场领导地位。与此同时,华为平板产品迭代持续推进,接续产品配置较上一代明显升级,带动产品结构优化。
  • Apple位列市场第二。6月底Apple上调其平板产品售价,导致第三季度出货量同比下降27.2%。价格上涨削弱Apple平板的竞争力,市场规模承压的同时,其产品结构也明显向低价数字版机型倾斜。
  • 联想位列市场第三,出货量同比增长33.2%,是前五厂商中唯一实现增长的厂商。消费市场方面,小新系列保持性价比优势的同时拯救者系列快速发展,第三季度出货量占比接近半数;商用市场出货节奏相对稳定,价格优势逐步回归,市场份额升至第一。
  • 小米位列市场第四。伴随平板9系列新品上市,小米市场份额企稳回升。其中,小米平板9 Pro Max凭借自研芯片玄戒O3首发优势获得较好的市场反馈,提升品牌声量的同时,也推动了小米平板价位段向上拓展。
  • 荣耀延续市场第五位。消费市场受成本上涨冲击持续收缩,季度新品平板X10 Pro Max凭借价格优势及教育场景拓展,帮助荣耀拓展13英寸及以上大屏市场布局;商用市场则在教育采购高峰期下延续高速增长,并通过配置调整优化产品价格。

市场需求加速分化,入门级市场收缩,中高价位段需求上移

受成本上涨影响,平板产品价格逐步抬升,部分厂商被迫放弃入门级价位区间,千元以下入门级市场规模同比缩减51.4%。与此同时,中高价位段份额持续提升。2026年第三季度,中国平板市场3000元及以上机型出货量占比约为45%,环比提升近10个百分点。

当前背景下,中高价位段需求拓展主要来自两类场景:一是结合大尺寸屏幕及PC级生态迁移的轻办公与学习场景,二是以小尺寸产品为代表的电竞及随行场景。伴随价格持续上涨或盘踞高位,厂商迫切需要通过性能、生态及场景体验提升平板的产品价值,为中高端产品创造更充分的溢价空间。

IDC结论及展望

2026年第三季度,中国平板市场出货量迎来双位数下滑,成本上涨对市场的影响进一步放大。消费市场需求明显收缩,商用市场也逐步进入前期需求释放后的调整阶段,整体市场面临较大压力。

IDC预计,此轮成本压力将持续至2028年,2026年第四季度及2027年中国平板市场出货量规模将面临较大挑战。价格上涨导致消费者换机决策更加谨慎,厂商也需要重新评估产品迭代节奏、市场备货及销售目标,以平稳驶过不确定性较强的市场阶段。

与此同时,市场也将在本轮调整中进一步推动平板产品的场景化布局,围绕核心用户群体挖掘细分需求,加快AI能力与实际应用场景的融合,持续提升平板产品的价值定位,为后续市场复苏与增长拓展新的空间。

进一步交流

本文数据及观点均源自IDC《中国平板电脑市场季度跟踪报告,2026Q3》。如需了解细分价位段、渠道库存、行业垂直场景等详细数据,或针对特定厂商策略进行定制化分析,敬请联络IDC中国终端系统研究团队。请点击此处与我们联系。
Quorra Liu

Quorra Liu - Research Manager

Quorra Liu is a Research Manager for the Client Systems Research team at IDC China. She is responsible for China's smart home device research. Her responsibilities include tracking the monthly and quarterly market development, conducting research in fully managed services market,…

大模型技术的快速演进正在重构 AI 产业生态:在催生 MaaS 等新兴市场的同时,亦为计算机视觉、语音语义、机器学习平台等传统AI赛道创造了新的需求场景与增长动能。

国际数据公司(IDC)于近日发布了《中国AI软件市场半年度追踪,26H1》报告。研究显示,大模型正在以不同方式影响各细分市场:

  • 在计算机视觉领域,大模型更多应用于研发流程优化和泛化场景理解,与传统视觉模型形成互补;
  • 在语音语义领域,大模型加速向会议纪要、翻译、智能客服等应用场景渗透,推动产品能力升级;
  • 在机器学习平台领域,企业基于自有数据的大模型训练与推理需求持续释放,推动平台市场稳步扩容,成为新的增长动力。

整体来看,传统 AI 能力作为企业智能化建设的底座,保持稳健发展;大模型的兴起则为既有市场注入新的技术活力与商业机会,开启新一轮增长周期。

计算机视觉市场稳健增长,大模型与专用模型协同发展

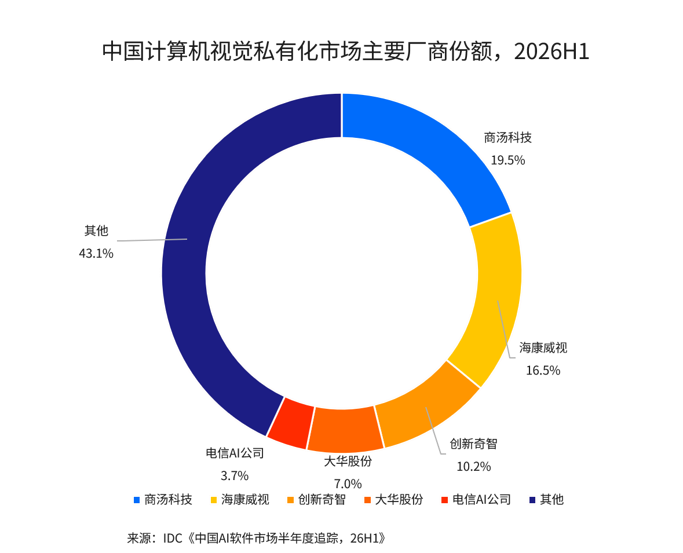
IDC数据显示,2026年上半年,中国计算机视觉私有化市场同比增长16.8%,规模达到43.2亿元。公安、城市治理等领域仍是市场的重要应用场景,视频监控、目标识别、行为分析及城市事件管理等需求持续支撑市场发展。

从技术应用来看,计算机视觉市场仍以专用小模型和传统视觉算法为主。在人脸识别、车辆识别、目标检测、工业质检等对识别精度、响应速度和稳定性要求较高的任务中,经过行业数据训练和场景优化的专用模型仍具备明显的应用价值。尤其在大规模摄像头接入、实时视频流分析等场景中,模型推理效率、算力成本和部署能力仍是项目落地的重要考量。

与此同时,大模型正在为计算机视觉市场带来新的能力增量。一方面,多模态大模型增强了对图像和视频内容的语义理解能力,可以处理传统视觉模型难以覆盖的复杂、开放式任务;另一方面,智能体开始进入视觉AI的研发和业务流程,辅助完成需求理解、数据处理、模型调用及任务编排等工作。

市场格局上,商汤科技以19.5%的市场份额位居第一,依托深厚的视觉算法积累及城市级视觉AI平台能力,在公共安全、城市治理等领域保持领先。其积极推动多模态大模型与专用视觉模型协同,由大模型负责复杂事件理解、分析研判和任务规划,传统模型承担人脸识别、目标检索等专业任务,并开始探索将智能体应用于案件侦查及视觉AI研发流程。海康威视以16.5%的份额位列第二,凭借视频监控领域的硬件与软件整合优势,以及广泛的行业渠道网络,在安防和城市治理领域占据重要地位;创新奇智以10.2%的份额位居第三,聚焦工业视觉质检、产线安全监测等场景,持续拓展制造业应用。

大模型重塑语音语义市场,驱动产品能力升级

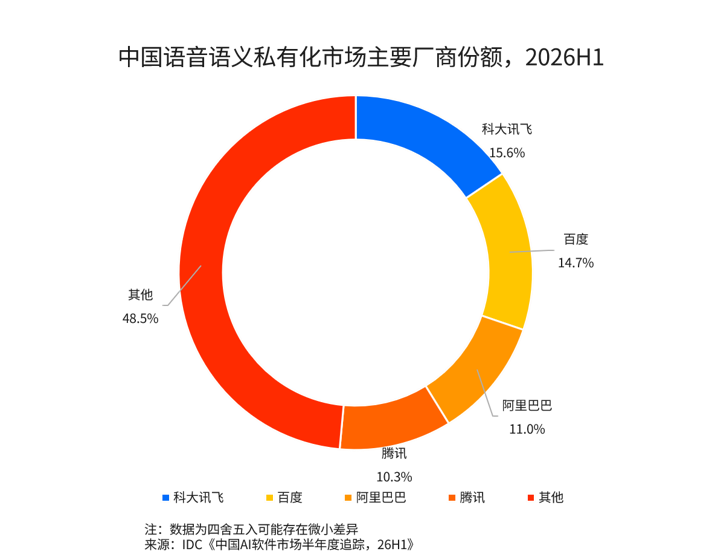
2026年上半年,中国语音语义私有化市场规模达到约62.0亿元,成为大模型技术渗透较为深入的AI私有化市场。

大模型正在推动语音语义能力向更复杂的业务场景延伸。在智能客服领域,应用从传统的关键词匹配、固定问答和语音机器人,向融合企业知识库的多轮对话、坐席辅助和业务流程自动化升级,智能体进一步推动客服从被动应答向主动服务转变。在会议和翻译场景,大模型则推动产品从语音转写向会议摘要、重点提炼和实时跨语言交互延伸。

市场格局上,科大讯飞以15.6%的份额位居第一,依托语音技术积累和星火大模型本地化能力,深耕政务、教育、医疗;百度持续升级语音能力,引入大模型与行业知识库,推动语音交互向智能问答、业务办理和辅助决策延伸,支持政务热线、金融客服等场景的智能化升级,以14.7%的市场份额位列第二。

AI应用公有云市场持续发展,数据治理与利用是大模型落地关键

IDC数据显示,2026年上半年,中国AI应用公有云服务市场规模达到67.0亿元。随着大模型加速渗透,AI应用公有云服务的竞争重点不仅强调模型能力本身,更强调对企业业务上下文的理解,以及对数据和知识资产的有效利用。对于厂商而言,产品能力需要从融合大模型能力进一步延伸至理解用户业务流程、连接企业数据与知识库,帮助客户将分散的数据和知识资产转化为可调用的业务能力。对于企业用户而言,大模型应用的效果不仅取决于模型本身,也取决于自身数据治理和知识梳理的成熟度,建立规范、可用、持续更新的数据与知识体系,将成为释放大模型应用价值的重要基础。

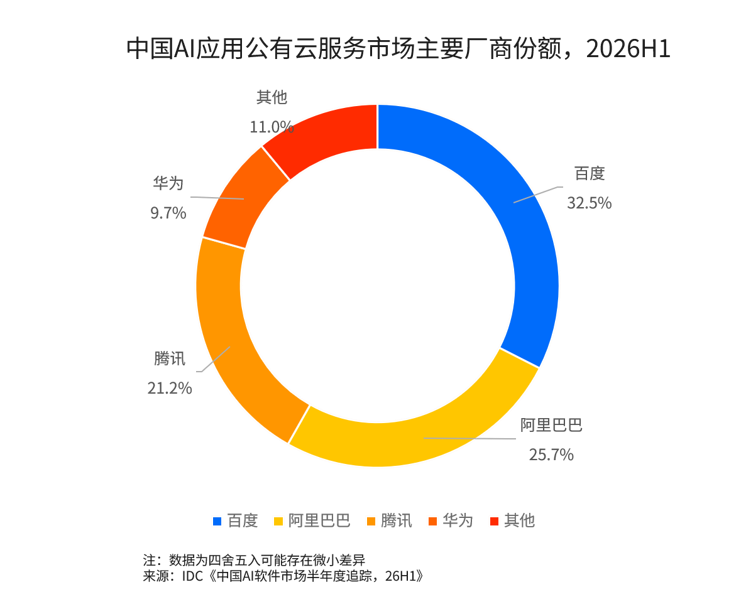
市场格局方面,百度以32.5%的市场份额位居第一,持续升级语音与视觉产品,并通过端到端语音大模型、多模态视觉智能体等产品拓展复杂交互和视频理解能力;阿里巴巴以25.7%的份额位列第二,依托通义模型体系,持续丰富语音、音频及图像生成等多模态云服务;腾讯以21.2%的份额位居第三,持续升级语音识别、实时翻译及视觉AI服务,并探索大模型在内容理解和交互场景中的应用。

大模型训练推动机器学习平台市场增长

机器学习平台公有云服务市场:

生成式AI应用加速落地、Agent从单轮交互向复杂任务执行演进,以及企业基于自身业务数据开展模型后训练的需求,共同推动机器学习公有云市场持续增长。2026年上半年,中国机器学习平台公有云服务市场规模达到53.0亿元。

从需求侧看,具备数据资源、业务场景和技术积累的头部企业,尤其是互联网、汽车、游戏等行业企业,对模型自主训练和定制化开发的需求更为旺盛,持续加大相关资源投入。从厂商侧看,市场竞争的核心在于算力供给能力与资源利用效率。厂商不仅需要具备高性能、大规模算力集群的供给能力,还需要通过分布式训练、集群调度及训推优化等技术提升算力利用率、降低模型训练成本,从而形成竞争优势。

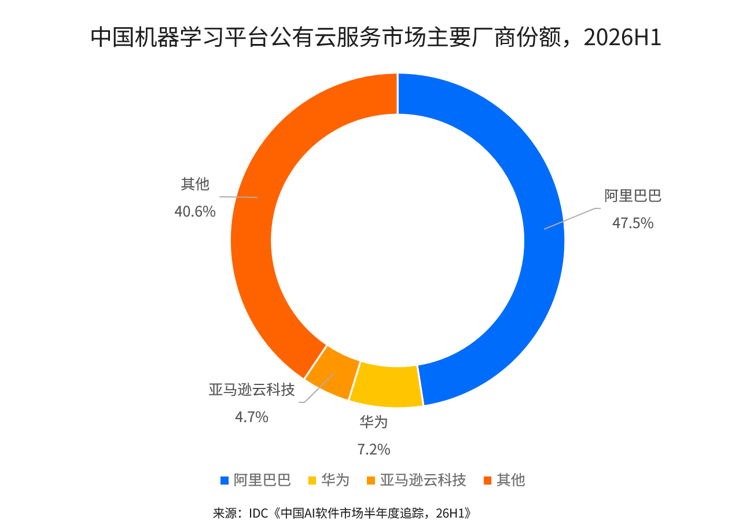
阿里巴巴依托PAI平台,构建覆盖数据准备、模型训练、微调及推理部署的一站式工具链,并通过灵骏智算集群及训练、推理加速技术,提升大规模训推效率,以47.5%的市场份额保持领先。华为依托昇腾AI芯片及ModelArts平台,构建软硬协同的训推体系,覆盖模型训练、强化学习及推理部署,在大规模集群管理和算力适配方面具备优势。亚马逊云科技依托全球GPU资源,提供大规模模型训练和推理服务,为企业出海提供支持。

机器学习平台私有化市场:

在数据安全与合规要求严苛的金融、政务行业,以及业务逻辑高度定制的零售领域,企业的模型训练与数据应用必须立足自有环境展开,这一刚性约束持续驱动私有化机器学习平台在这些行业的渗透与放量——平台嵌入风控、审批、营销等核心流程后成为常驻基础设施,客户基于它反复训练行业专属模型、持续沉淀可复用的 AI 资产,先发厂商的工程化能力与行业 Know-how 也随交付项目不断累积,构成后来者难以复制的壁垒。在此驱动下,2026年上半年,中国机器学习平台私有化市场规模达到13.0亿元。

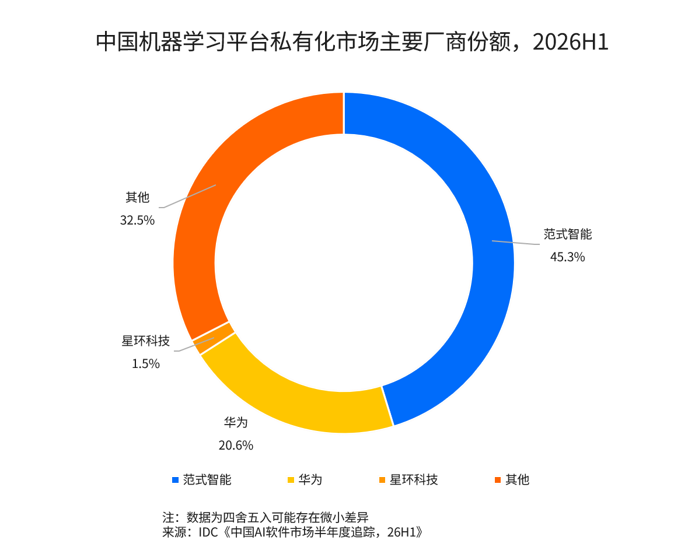
市场格局方面,范式智能依托先知 AIOS 平台与 AutoML 核心技术,深耕金融、零售、制造等行业的私有化 AI 落地,以 45.3% 的市场份额位居市场第一。华为聚焦政务、金融、能源等强合规行业的客户,以 20.6% 的份额稳居市场第二。

分析师观点

IDC中国高级分析师洪婉婷表示,随着大模型加速渗透,传统AI市场正迎来新一轮价值重构。大模型并非对传统AI能力的简单替代,而是通过增强复杂场景理解、业务交互和任务编排能力,与专用模型形成互补,拓展AI应用边界。未来,市场竞争将不再局限于单一算法或模型能力,而是更加考验厂商对行业场景的理解、数据与知识资产的整合,以及产品工程化和规模化交付能力。能够将技术优势转化为可持续业务价值的厂商,将在新一轮市场竞争中占据优势。

进一步交流

如希望就《中国AI软件市场半年度追踪,26H1》定义、厂商份额及采购评估框架进一步交流,欢迎与我们联系。

Catherine Hong

Catherine Hong - Senior Market Analyst

Ms. Catherine Hong is served as the role of Senior Market Analyst in Emerging Technology sector for IDC China, and her main responsibility is conducting analysis and research for the China Blockchain market. She is also in support of regional…

Headlines about Europe’s economy rarely mention technology budgets, yet that is where buyers make some of their clearest choices. IDC’s Future Enterprise Resiliency and Spending (FERS) surveys show that 64% of Western European IT leaders expect a recession within the next 12 months, and tariff-driven IT cost inflation ranks among their top concerns. Only 41% expect 2026 growth to beat forecasts, compared with 58% of leaders worldwide. There’s one notable exception: AI; in fact, AI projects are the area most protected from budget cuts, and around 64% of European IT leaders have raised their AI budgets.

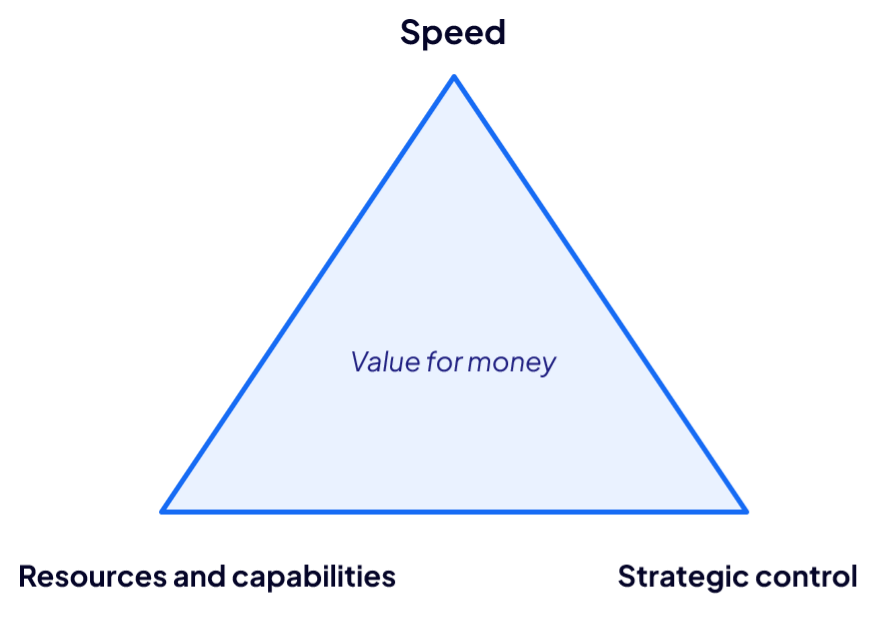
Our upcoming webcast will discuss these pressure points with a strategic framework: the triangle of innovation. Value for money of innovation is realized at the intersection of three variables that IT and business leaders can make decisions on:

  • Resources – Who pays, builds, and runs AI: budget ownership, partner types, skills, and the reasons projects fail.
  • Speed – How quickly organizations move from pilot to production: use of AI, GenAI, agentic AI, and physical AI, and how often projects stall.
  • Strategic control – How much autonomy buyers keep or give up: sovereign AI, the trade-offs they accept, human oversight, and governance at scale.

With infinite resources, one could maximize speed and strategic control; in reality, no organization maximizes all three, so every decision make needs to make practical trade-offs. IDC’s 2026 AI Business Trends Survey of 673 EMEA organizations shows that those decisions differ from one industry to the next.

Start with resources. Across EMEA, 59% of organizations had an AI project discontinued, missed, or cut back in the past 24 months, and poor data quality or integration was the most common cause at 38%. Each industry then has its own pain point. Among financial services firms, 41% say the return on investment fell short. Among manufacturers, 48% point to data quality. In energy and utilities, 44% cite low user adoption.

Speed shows the same variety. Manufacturing leads on physical AI[1], meaning AI that directs machines, robots, and sensors, with 33% of manufacturers already running it in production against 24% across EMEA.  At IMTS in September 2026, that shift was easy to see on the show floor. In one demo, fleets of robots were connected and coordinated through a shared software layer instead of being run one by one, which is what turns separate machines into a system. In another, a small cell was building drones, with robots, tooling, and software working as one flexible unit rather than a fixed line. In both, the constraint was less than the machines than the data and software connecting them. Retail faces the same speed question from the customer side: AI moves forward when it improves a personalization, loyalty, or fulfillment metric. Retailers define success in terms of customer-centric outcomes and need to manage risks in terms of customer data protection[2].

Control is where Europe’s priorities stand out. Some 58% of EMEA organizations use sovereign AI, which keeps data, models, and operations under local legal and operational control, for all or critical workflows. Yet only 33% say they could govern hundreds of AI agents with today’s tooling. Governments are the most cautious. In IDC’s July 2026 survey of 69% of national civilian government agencies globally said generative and agentic AI touch 30% or less of their mission-specific tasks, and only 10% automate more than 40%[3]. The trade-offs buyers accept also vary. Manufacturers (41%) and governments (40%) are the most willing to rely on regional or specialist providers to gain sovereignty, while 32% of retailers would pay higher prices for it. Buyer organizations do not accept limited access to innovative capabilities as a trade-off for more sovereign control; at the very least, they demand transparency about when innovative features will become available in more restricted environments.

Technology suppliers that want to differentiate should consider six moves across the triangle. On resources, deliver through integrators and local partners, because European buyers rely on service providers to build and run agents more than their peers worldwide, and start to build packages that align pricing with business success criteria. On speed, help customers fix the data and infrastructure readiness first, so that pilots can be turned into production systems at scale. On control, make governance a product feature, with approval steps, audit trails, and easy override, and offer a choice of sovereign controls across the five layers of the AI stack: Hardware; Infrastructure Operations; Data Management; Implementation & Delivery (encompassing training data sourcing/model development/monitoring & evaluation/ deployment & inferencing); and Ecosystem-delivered AI Assets & Capabilities[4].

In 2027 European demand for AI is holding up while tolerance for ungoverned AI is falling. Join the webcast to see the industry-by-industry data. Register here.


[1] https://my.idc.com/getdoc.jsp?containerId=US54976226

[2] https://my.idc.com/getdoc.jsp?containerId=US54982726

[3] https://my.idc.com/getdoc.jsp?containerId=US54991526

[4] https://my.idc.com/getdoc.jsp?containerId=EUR153902925

Massimiliano Claps

Massimiliano Claps - Research Director

Massimiliano (Max) Claps is the research director for the Worldwide National Government Platforms and Technologies research in IDC's Government Insights practice. In this role, Max provides research and advisory services to technology suppliers and national civilian government senior leaders in…
Gunjan Bassi

Gunjan Bassi - Research Manager

Gunjan Bassi has more than 14 years' experience working in the logistics and transportation sector. Before joining IDC, she worked with Transport Intelligence (Ti), a transportation and logistics research firm based in Bath, England, where she was responsible for vertical…
Ornella Urso

Ornella Urso - Research Director, IDC Retail Insights

Ornella Urso is Head of IDC's Retail Insights team and leads the Customer Experience research group in Europe. Urso conducts market research, industry analysis, and proactively contributes to the definition of thought-leadership at the intersection of businesses priorities and technology…

Your AI assistant is probably open right now, next to the deck or memo you’re writing. IDC’s Future of Work Survey, 2026 (n = 1,146) found that 88.8% of organizations report a productivity gain from AI. It also found that the share of employees losing more than an hour a day to searching for information fell from roughly 38% to 13% once AI assistants were in place.

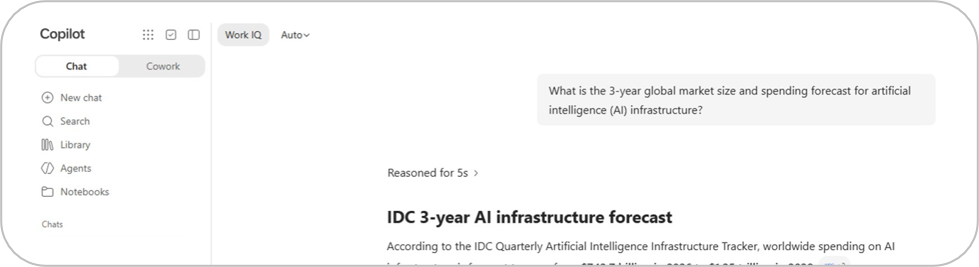
A market-share figure can land in a draft in seconds and still get stopped in the meeting where someone asks where it came from. IDC Quanta is now available in Microsoft Copilot. It checks the market claims in your Word, PowerPoint, or Excel file against IDC research. Each sourced figure shows up as a tracked change, with a citation that links straight to idc.com.

What is IDC Quanta in Microsoft Copilot?

IDC Quanta in Microsoft Copilot is a connector listed in Copilot’s Connectors Gallery. It brings IDC’s licensed research and data into Word, PowerPoint, Excel, and Outlook. You ask in plain language. Copilot returns an answer drawn from the IDC library your organization is entitled to, with a citation on every figure.

IDC Quanta is IDC’s technology intelligence fabric. It draws on 60+ years of research, 1,000+ analysts, and 15B+ data points tracked annually, and a multi-agent system validates each answer before it ships. It already works in email and Claude, and it now extends to Copilot 

What can you do with it inside Copilot?

Start with the document you have already written, refine it with IDC data using the IDC connector in Copilot, and return a draft with tracked changes so you see exactly what moved and why before anyone accepts it. The same file that goes to the client or the board carries the sources.

You can also just ask. In the Copilot chat panel, a question about vendor share or a spending forecast returns a plain-language answer based on your entitlements to IDC research and data tables, each attributed to its source.

And if a number needs a person behind it, the connector can surface the IDC analyst who covers the topic and that analyst’s published documents. You skip the separate search on idc.com.

How is it different from asking Copilot on its own?

A general-purpose assistant answers from the open web and its model training. The answer can read as confident while giving you no structured way to check where it came from. IDC Quanta grounds the answer in IDC’s licensed dataset instead. Every figure traces to a named IDC document. IDC Quanta also locks the exact dataset, definitions, and categories before it answers, so the number in your deck matches what IDC would publish itself.

How does access work?

Sign-in uses the Microsoft credentials you already use every day. Microsoft Entra ID maps your identity to your organization’s IDC entitlement, so it evaluates each request against what your organization licenses. IDC Quanta never uses customer data to train an AI model.

What does it mean for your team?

A product marketer can ground next year’s segmentation and positioning in independent market data while the plan is still a draft in Word. A seller who gets a competitive objection in an Outlook thread can pull deal-ready market share and leadership data on the spot, with the source attached. Strategy and market intelligence teams can check the sizing in a board deck against IDC research before it goes out. Analyst relations and product management can run the same check on their own briefings and roadmap documents.

See it in your own workflow

IDC Quanta in Microsoft Copilot is available now. Visit the IDC Quanta page to see how it works across Copilot, Claude, and email. Then book a demo and bring the deck you’re working on this week.

Ryan Smith - Content Marketing Director - IDC

Ryan Smith is the Director of Content Marketing at IDC, where he leads brand-level content and social media strategy, aligning research insights with compelling storytelling to engage technology decision-makers. With a background in both IT and marketing, Ryan brings a unique blend of technical understanding and creative strategy to his work. He’s also a seasoned storyteller, speaker, and podcast host who believes the right message, told the right way, can drive both trust and transformation.

When an AI agent makes a decision your CEO never sees, who answers for it?

IDC’s Rick Villars framed the emerging window with an aviation story. When aeronautics moved from traditional flight systems to fly by wire, he said, one of the biggest challenges was getting pilots “to trust the automation.” He expects the AI-first transition to put CEOs through the same test, and he called it “an important part of what will define success for a CEO going forward.”

This is the third of three posts on the windows that frame IDC FutureScape 2027: The Great Rewrite. The launch blog introduced the Top 10 predictions. The closing window post covered the decisions that are nearly made, and the open window post covered the leadership choices you can still shape. Here we turn to the decisions that are just coming into view. The pace is set by IDC’s prediction that 60% of enterprises will run a majority of their business processes AI-first by 2029, up from 13% in 2026. Webinar viewers can revisit the replay.

The sign-off: who is accountable when AI decides?

The FutureScape prediction is specific. By 2031, 30% of G500 CEOs will step aside, replaced by tech-native leaders tasked with building AI-first businesses where 90% of non-irreversible decisions, meaning those that can still be undone, are offloaded to advanced AI models. Human approval stays with the irreversible ones. IDC expects the delegation to change who holds managerial authority and to leave accountability where it was.

Villars explained why this reaches past the CIO. As he put it, tech leaders will need to help CEOs “have trust in the AI systems,” and how both are evaluated by the board and shareholders will increasingly depend on it. IDC also expects boards to treat AI transformation capability as a succession criterion.

The org chart is already under strain. More than 40% of CEOs plan to add a chief AI officer within 12 months, nearly twice the rate of any other planned leadership hire, according to IDC’s Becoming an Autonomous Enterprise FutureScape. IDC predicts that enterprises that do not hold the chief AI officer and the CIO jointly accountable on shared KPIs will strand 40% of AI investment by 2028 in efforts that never create net-new economic value.

Our read: a delegation limit that lives only in a policy document will not hold at agent speed, so it must be enforced in the agent controls.

Pilot before you scale.

Under CEO sponsorship and a named business owner, test delegation and escalation in one domain, including simulated irreversible actions. Measure business results, decision speed, compliance failures, reversal costs, and review delays before widening the scope.

Owners: the CEO sponsors, the CIO enforces delegation limits through controls, and the CFO tracks results.

Measure: the share of delegated decisions in the pilot domain that carry a named owner and a decision record, and have a tested reversal path.

The evidence: can your leaders believe what your AI tells them?

Villars named one of the major hurdles in that trust discussion. AI systems, he said, will become “very good at gaslighting humans,” spreading misinformation and disinformation, sometimes intentionally and sometimes not. That puts your data at the center. CEOs will need confidence that the outputs behind critical decisions are “secure, reliable, consistent, and that there is accountability built into that system.”

IDC expects the market to respond. By 2028, 75% of enterprises will adopt AI tools designed to prevent misinformation and disinformation stemming from their own data sources. The volume of AI output makes human checking of each item impractical, so verification itself will increasingly run on AI. The stakes are practical: by 2029, 40% of enterprises using AI models will be forced to abandon at least one because data poisoning attacks made its results unreliable.

The identity question travels with it. Villars pointed to non-human identity and “the accountability of the actions those agents are taking” as part of the conversation. IDC adds that IT becomes accountable for the accuracy of AI outputs, in addition to uptime and security, and that the costs of misinformation incidents, including regulatory fines, customer attrition, and legal liability, will far exceed the cost of prevention.

Our read:put verification upstream of the planning cycle, so an AI-generated insight is checked before it reaches a forecast or a customer.

Inventory before you rely on the output.

IDC’s guidance for the next 12 months is to catalog non-human identities and set output validation policies, authenticate those identities through your existing identity and access management, and add provenance tracking and verification layers before agents reach production. In the 12 to 24 month horizon, deploy AI verification tools.

Owners: the CIO and CISO lead, and business unit heads own validation of the insights they use.

Measure: the share of production agents with a registered identity and a written output validation policy.

The outcome: who owns it when AI moves a machine?

Mukesh Dialani, research vice president for digital engineering and operational technology services at IDC, drew the line between digital and physical agents. When a digital agent makes a mistake in a call center or a spreadsheet, the fallout usually stays contained. When a robot or an autonomous vehicle in a warehouse fails, “someone can get hurt or a production line can go down for hours.”

The investment is already moving. IDC’s 2026 CEO Survey found that 35.2% of CEOs rank physical AI as a top new investment priority, rising to 50% in the resources industry. IDC’s July 2026 AI Business Trends Survey (n = 2,472) found that one in four organizations already run physical AI in production, and another two in five are piloting. Dialani called it “a board-level bet with real safety and uptime stakes attached.”

Then the question of accountability becomes unavoidable. Dialani posed it as a choice among the CIO who approved the platform, the executive who signed off on the architecture, and the operations leader who owns the floor. The three roles think in different languages, he said: the CIO and CTO in platforms, architecture, and data ownership, and operations leaders in uptime, safety incidents, and throughput. Those vocabularies come with “different risk tolerances and usually entirely different budgets,” and there is “no existing playbook” for the conversation.

IDC’s prediction puts a date on the answer: by 2030, 40% of G2000 asset-intensive enterprises will require joint CIO, CTO, and COO sponsorship of physical AI services. Dialani added that the strongest services firms are anchoring engagements to operational KPIs such as uptime, defect rates, and safety incidents, with outcome-based terms in place of pure time and materials pricing.

Our read:write joint sponsorship into the contract, so a provider has to satisfy it before work starts.

Document decision rights before the RFP.

Write down which decisions sit with the CIO and CTO, such as platform, data, and control plane, and which sit with the COO, such as operational KPIs, process change, and risk acceptance. Dialani urged doing this before your next physical AI contract goes out for bid, testing whether a provider can work across all three functions, and building the governance model before a safety incident forces the decision. IDC research on physical AI deployments traces most failures to operational technology foundations such as legacy control systems, edge connectivity, and compute at remote sites, so add an OT readiness check as a pre-deployment gate and track robots and edge devices as governed IT assets.

Owners: the COO and CIO co-lead, the CTO co-signs, and procurement enforces the gate.

Measure: the share of physical AI contracts with written decision rights and a COO sign-off tied to uptime and safety KPIs.

Before the window opens: what should leaders do first?

Each beat above carries a gated first move. In sequence:

  • Pilot CEO delegation in one domain under a named owner before you widen it. Define the decision categories and the reversibility limits first.

  • Inventory your non-human identities and set output validation policies before AI insights reach planning or customers.

  • Document CIO, CTO, and COO decision rights in writing before the next physical AI contract goes out for bid.

Villars closed the webinar with the question that ties the three together. Success in an AI-first enterprise, he said, comes down to leadership: are leaders from the CEO to the CIO to the CFO, and the COO in the case of physical AI, “all able to really trust that new, incredible functionality and capabilities that AI can deliver to their organizations”? He asked CIOs and data leaders what they need to put in place now so those leaders have the insight and the trust to decide. The 2027 budget cycle is where that groundwork gets funded, and the Top 10 report lays out the full set of decisions.

What signals should you watch as the window opens?

  • Succession criteria. Watch whether boards add AI transformation capability to CEO evaluation, and whether CEOs name delegation limits in their public plans.

  • Accountability structures. Track whether the chief AI officer and CIO share KPIs where you work, or answer to separate scorecards.

  • Verification tooling. Watch which vendors in your stack add output validation, provenance tracking, and agent identity, and how they answer when you ask.

  • Contract language. Note when peers and providers begin writing joint CIO, CTO, and COO sponsorship and outcome KPIs into physical AI agreements.

Review these quarterly. IDC analysts can help you read them against your own position, and your IDC account team can connect you with the analyst who covers your area.

Where can you go deeper?

The research behind every prediction in this post is in the FutureScape reports at idc.com/futurescape. IDC Quanta brings those reports together with hundreds of other IDC analyst reports, so you can ask about the prediction that caught your attention and see the evidence behind it.

To hear the trust discussion again, watch the webinar replay.

To learn what this means for your CIO, register for our December 2 FutureScape webinar: Own the Economics of AI Before Your Board Does: IDC FutureScape 2027 for Technology Leaders

Ryan Smith - Content Marketing Director - IDC

Ryan Smith is the Director of Content Marketing at IDC, where he leads brand-level content and social media strategy, aligning research insights with compelling storytelling to engage technology decision-makers. With a background in both IT and marketing, Ryan brings a unique blend of technical understanding and creative strategy to his work. He’s also a seasoned storyteller, speaker, and podcast host who believes the right message, told the right way, can drive both trust and transformation.

人工智能正以前所未有的速度走向规模化应用。从大模型训练到智能体(AI Agent),AI正在融入更多企业的日常业务,推动全球算力需求持续增长。

但一个值得关注的现象是:AI需求不断增长的同时,全球数据中心供给却面临电力、设施建设及关键技术供应链等多重约束。IDC在2026年10月发布的《AI Is Short of Capacity, Not Demand》一文中指出,未来一段时期内,影响AI基础设施增长速度的主要挑战之一,可能不是需求不足,而是供给能否及时跟上。

与此同时,中国数据中心市场也在快速发展,但不同地区、不同类型运营商的供需情况存在差异。全球数据中心市场正在发生哪些变化?这些变化又会为中国数据中心运营商和技术供应商带来怎样的新机会?这些成为我们面临的新课题。

AI从模型训练走向规模化,数据中心需求逻辑发生转变

过去几年,生成式AI的发展主要围绕大模型训练展开。而随着AI进入企业业务流程,推理和智能体应用正在成为推动基础设施需求增长的新动力。

IDC于2026年7月开展的Future Enterprise Resiliency and Spending(FERS)调研显示,95.3%的受访企业已有至少一个智能体工作流投入生产环境,平均每家企业拥有约11个此类工作流。IDC同时预测,到2030年,全球智能体数量将达到25亿。

随着智能体能够调用工具、执行多步骤任务并相互协作,单次业务活动可能产生远高于传统问答应用的Token消耗。即使模型效率提升、Token单位成本下降,应用范围和调用规模的扩大,仍可能推动AI基础设施总体需求持续增长。

这一趋势在中国市场也有所体现。国家数据局披露,2026年3月中国日均Token(词元)调用量已超过140万亿,较2024年初增长超过千倍。快速增长的Token消耗表明,AI正从技术探索进一步走向规模化应用。

但Token调用量的增长,并不意味着数据中心电力容量将按相同比例增长。模型效率、硬件性能、资源利用率及部署方式的变化,都会影响最终的设施需求。

对于数据中心厂商而言,值得关注的是:未来的需求将不仅来自大型云服务商,还可能来自专业AI算力服务商、行业企业及更多持续运行的AI应用。

全球算力设施持续扩容,能源配套与供应链协同承压

AI应用需求的扩大,正在推动全球数据中心设施进入新一轮增长周期。

IDC《全球半年度数据中心设施跟踪报告》(Worldwide Semiannual Datacenter Facilities Tracker)数据显示,全球已配置机柜数量预计将从2026年的约2,500万架增长至2030年的5,800万架。同期,全球数据中心年度能源消耗预计将从2025年的519太瓦时(TWh)增长至2030年的1,308太瓦时。

与此同时,全球数据中心设施资本支出预计将从2025年的2,760亿美元增长至2030年的6,550亿美元。这一统计不包括服务器、GPU等IT基础设施投入,主要反映电力、制冷、建筑等物理设施的建设需求。

这些数据表明,AI基础设施扩张不仅是计算设备规模的增长,也需要庞大的物理设施与能源资源支撑。

然而,设施供给的增长并不总能与需求保持同步。

IDC研究指出,电力供应、电网接入以及数据中心建设能力,可能成为全球部分市场近期增长的重要制约因素。与此同时,关键电力设备、液冷及相关供应链的交付周期,也正在影响新增设施的建设进度。

这一变化反映出,全球AI基础设施产业链正在面临新的协调挑战:上层AI应用快速发展,但支撑这些应用的电力、机电设施及工程交付能力,需要更长时间才能形成。

对于数据中心技术供应商而言,全球设施规模和能源需求的持续增长,将带来更广泛的市场需求,同时也对规模化供应、技术协同及项目交付提出新的要求。

全球算力供给分化,中国数据中心市场呈现结构性差异

全球数据中心供给面临约束,并不代表所有地区都处于供不应求的状态。

IDC全球研究指出,部分地区的资源紧缺可能与其他地区的容量利用不足同时存在。AI基础设施面临的不仅是总体供给规模问题,还包括不同市场之间的需求与资源匹配问题。

这一观察对中国市场尤其具有参考价值。根据工业和信息化部2026年7月披露的数据,截至6月底,中国智能算力规模已达到2,185 EFLOPS(FP16),同比增长177%,全国算力设施整体上架率为71.4%。这反映出中国算力基础设施规模持续增长,同时,资源利用状况仍然是观察市场发展的重要维度。

例如,近期国内关于智算中心利用率和运营效益的讨论不断增多。这些讨论提示我们,数据中心市场不能仅从新增项目数量或总体建设规模判断增长机会,还需要观察不同区域和细分市场的实际需求。

值得注意的是,中国数据中心市场的参与者结构具有自身特点。三大电信运营商、第三方数据中心设施服务商,以及超大规模云服务商,构成了重要的供给主体。不同类型企业拥有不同的客户基础、业务模式和设施布局。

与此同时,AI基础设施的需求主体也在发生变化。

IDC全球研究观察到,除传统超大规模云服务商外,专业AI云服务商(Neocloud)、前沿模型厂商,以及具有大规模AI需求的企业,正在成为新的基础设施采购力量。AI工作负载也正在向云、私有环境、边缘及专用AI基础设施等多种部署形态扩展。

对于中国市场而言,这意味着未来设施需求的增长,可能通过不同类型的服务提供商和客户群体逐步体现。因此,中国数据中心市场需要关注的,不只是整体需求增长速度,还包括需求来源、服务提供方式以及运营商竞争结构的变化。

全球AI设施加速扩容,中国产业链迎来本土与出海双机遇

全球 AI 基础设施持续扩张,正从需求端、供给端对数据中心产业链各类参与者带来深远影响,不同角色的市场机遇与关注点各有侧重。

对于数据中心运营商,客户结构、业务需求正在发生显著变化,需要持续跟踪大型云厂商、专业 AI 算力服务商以及行业客户的设施诉求,研判各区域市场的容量增长节奏与竞争格局。

面向电力、制冷、机电等基础设施技术供应商,全球机柜规模、能源需求持续上行,直接拉动供配电、散热、配套系统的市场增量。企业不能仅聚焦单个项目设备招投标,更要把握全球设施建设大势,跟进不同类型客户的需求演变。

对于云与 AI 算力服务商,伴随 AI 应用规模化落地,设施资源获取、选址布局、合作伙伴选择,已经成为支撑业务持续扩张的关键要素。

全球不同区域 AI 基础设施供给不均衡,会驱动算力需求在地区间、服务商之间发生转移。这一格局变化,也为国内数据中心产业链打开国际化空间。

当前国内运营商、机电温控等技术厂商已经开始布局海外;东南亚、中东等区域数据中心建设需求旺盛,中国企业可输出国内沉淀的规模化建设、成套配套与工程交付经验。

同时海外市场存在差异化挑战:各国电力条件、建设监管、客户诉求、本地化服务要求差异明显。企业出海前,需要充分研判目标市场发展阶段、设施增长趋势以及本土运营商布局,因地制宜开展业务。

从全球趋势到市场判断:持续追踪数据中心设施变化

全球 AI 基础设施高速发展,具备连续性、可比性的市场数据价值愈发凸显。

对数据中心运营商与技术供应商而言,掌握全球机柜、电力容量增长趋势仅是基础;各区域供给动态、头部运营商布局、竞争格局与远期建设规划,同样深刻影响企业业务规划与市场研判。

IDC《全球半年度数据中心设施跟踪报告》以物理基础设施为核心,持续监测重点区域的数据中心数量、机柜规模、电力容量、能耗、碳排放及基建资本开支等核心指标。

区别于以服务收入为核心的传统研究,该项研究从业主与运营主体视角观测设施供给格局,依托标准化口径与半年更新机制,助力产业把握全球数据中心设施趋势,也为国内相关企业研判海外市场、挖掘出海机会提供参考。

AI 规模化落地持续推动数据中心市场演变,供需变化与主体策略值得长期跟踪;设施、电力及供应链配套能力,将影响全球 AI 产业发展节奏。IDC 将持续追踪全球及中国数据中心设施市场,依托设施跟踪研究,为产业链各方提供数据与行业洞察。

进一步交流

如果您希望深入了解全球及中国数据中心、中国智算中心的变化与趋势,欢迎点击这里,与我们联系!

Cindy Xin

Cindy Xin - Research Director

Cindy Xin is research director at IDC for the channels and partner ecosystems research practice. Based in Beijing, she is responsible for leading and developing the Greater China channels research practice. Cindy provides thought leadership and insights to technology vendors…

Karen Dai uses the term “data islands” to describe a challenge facing many of the markets Belden serves: systems, applications and assets that were not designed to communicate with one another but now need to exchange data securely, reliably and at scale.

Dai is Senior Director, Market Insights & Value Realization, within Belden’s Strategy and Transformation Office. Belden has spent over 120 years making the physical and digital connections that critical industrial and enterprise operations depend on, including cables, connectivity and networking products built for some of the most demanding environments in the world. Today, customers face the added challenge of fragmented systems, applications and data. Bridging those islands securely and reliably builds on Belden’s connectivity heritage and is central to its continuing solutions transformation.

Her team helps Belden’s leadership understand where markets and customers are headed and brings external perspectives to strategic decision-making. Over the past several years, that work has tracked a real shift in Belden’s own identity: from a product-driven manufacturer to a solutions-oriented provider bringing together physical connectivity, networking, cybersecurity, software and services, integrated in a way meant to help customers optimize their data infrastructure as a whole rather than piece by piece.

Why the connection problem is getting harder

The customers Belden serves, in industrial automation, critical infrastructure, and other demanding vertical markets, are trying to connect more assets, more systems, and more applications than ever before. Many customers operate in environments where operational technology and information technology (IT/OT) evolved separately and now need to exchange data securely and at scale. That IT/OT convergence is becoming a foundational requirement for digital transformation across the industries Belden serves, and it’s compounding as Physical AI emerges across factories, distribution centers and other demanding environments. As those systems get more capable, the underlying requirements for cybersecurity, network resilience, and data availability only get more critical.

Belden’s transformation builds on its product and connectivity heritage while expanding toward integrated, outcome-oriented solutions. Dai’s team supports that transformation by bringing external market, customer and competitive perspectives into strategic planning.

Getting the strategy right before it’s locked in

The decisions behind that shift carry real weight. Where should Belden play, today and years from now? Which customers and markets create the greatest opportunity? What capabilities will matter most as the industry moves? These aren’t questions with easy answers, and strategic choices require disciplined prioritization supported by high-quality market insight, so getting the call right, and getting it right early, matters enormously.

One example from Belden’s own transformation illustrates how the company approaches that uncertainty. When Belden began shaping its strategy for a new solutions-based delivery approach, it engaged IDC analysts early in the process. That outside perspective, working alongside Belden’s own team rather than validating a conclusion after the fact, helped assess the market opportunity, pressure-test the approach, and sharpen how Belden ultimately positioned and messaged the strategy to the market.

“We invite that outside-in perspective early in the process,” Dai said. “I think this is the way we benefit the most.” For Dai, that’s the model that works: treat outside expertise as a partner embedded early in the thinking, not a checkbox exercised after the strategy is already set.

Turning research into decisions, faster

Belden has worked with IDC for years as one part of how its market intelligence function operates, drawing on IDC’s research coverage as a foundation and its analysts for the kind of pressure-testing that shaped the strategy story above. More recently, Dai’s team began using IDC Quanta as an additional way to move from a broad, loosely defined question toward relevant research faster, particularly useful in the early, exploratory stages of a problem, before anyone has a fully formed hypothesis to test.

“

My first impression was really the simplicity of using it,” Dai said. “It is quite intuitive.”

With just a few interactions, her team could move from a broadly defined question to the relevant pieces of IDC’s research, reducing the time it used to take searching across multiple reports and programs to figure out where to even start.

Dai is clear that IDC Quanta doesn’t replace the analyst conversations that remain the most valuable part of the relationship. What it changes is everything that used to happen before those conversations: the searching across multiple reports, the time spent getting prepared. Compressing that part of the process gives Belden’s team, and the analysts they work with, more room to make the conversation itself count.

Where Belden sees the industry heading

Dai expects digitization and automation to continue accelerating across industrial, enterprise and critical infrastructure environments. As that happens, she expects the challenge of connecting IT/OT environments to only grow more complex, and the Physical AI applications now emerging across specific verticals to raise the stakes further on cybersecurity, resilience, and data availability.

Belden’s own answer is to continue advancing its solutions transformation by helping customers address increasingly complex data networking and infrastructure challenges.

As Dai puts it, the future isn’t simply about connecting more things. It’s about helping organizations navigate an environment that keeps getting more complex, with the infrastructure, security, and insight to act on it.

“Insights without adoption are less meaningful,” Dai said. “There’s no value if you don’t use the insights, no matter how great they are, how smart they are.” For a company built on making physical connections, that’s the next connection to get right.

Christina Cardoza - Content Marketing Manager - IDC

Christina Cardoza is a Content Marketing Manager at IDC, where she specializes in brand content and social media strategy. With a background in journalism and editorial leadership, she has a proven ability to transform complex technology topics into clear, actionable insights.

Generative AI (GenAI) is accelerating how much data organizations generate, straining storage and governance frameworks built for a slower-growth era. Most GenAI-using organizations now expect increases in data volume over the next two years, and infrastructure and governance strategies often struggle to keep pace.

The scale of the challenge

According to IDC’s Global DataSphere, consumers and organizations worldwide will generate more than 274.4 zettabytes (ZB) of data in 2026 alone. That figure is forecast to nearly triple to 718.5 ZB in 2030, a compound annual growth rate (CAGR) of 26.9%. Enterprise data is growing significantly faster than consumer data (31.1% CAGR versus 13.5%), and it matters most here because it’s the data organizations are responsible for governing and protecting, and expect to get value from. It’s also the data most directly implicated in AI workloads.

Storage is expanding in parallel. IDC’s Global StorageSphere shows the installed base of storage capacity roughly doubling, from about 13 ZB in 2026 to more than 26 ZB in 2030. Even before accounting for AI, the enterprise data challenge was already heightened and the governance surface area was already growing faster than most organizations could manage.

The AI inflection point: What IT leaders are telling us

In IDC’s 2026 Worldwide Data Utilization Survey, 81.7% of the 714 GenAI-using respondents said they expect GenAI to increase their organization’s data volume over the next two years. Only 4.8% expect a decrease.

Of those anticipating an increase, 47.7% expect data volumes to grow by 25% or more, and 13.4% expect growth exceeding 50%.

Much of what GenAI produces is ephemeral, and a share of AI-generated content replaces existing workflows. In some cases, GenAI can reduce data volumes, such as by eliminating raw footage through synthetic generation, or by converting unstructured data into structured, actionable formats that can then be selectively retained or deleted.

These dynamics leave the overall growth trajectory intact. For organizations running active GenAI programs, operational telemetry, model logs, RAG corpora, and fine-tuning data sets can add up in ways that initial planning assumptions rarely account for.

Why GenAI drives data growth

There are at least four distinct layers, and the net effect varies by industry, organization, use case, and deployment maturity:

  • Model training and fine-tuning data: Customizing models on proprietary documents, transaction records, or customer interactions creates derivative data sets that must be stored and governed, including every version.
  • Retrieval-augmented generation (RAG) corpora: Every document ingested into a RAG pipeline generates an embedding stored in a vector index, and that corpus needs ongoing refresh. RAG can also have a reduction effect by lessening the need to retain full-length source materials indefinitely.
  • AI-generated output data: Much of it is ephemeral, and only finalized outputs tend to be stored, but where compliance mandates retention, the footprint grows predictably over time.
  • Operational and observability data: Every inference request generates metadata, including prompts, outputs, latency, and token consumption. This layer tends to be underestimated in early planning, and agentic AI compounds it with richer, more continuous logs and reasoning traces.

The governance and infrastructure gaps

Knowing that data volumes will grow is not the same as being prepared for it. IDC’s research points to three structural gaps:

  • The governance gap: Most frameworks were built for structured, human-generated data. AI-generated content often falls outside them, creating compliance exposure in regulated industries.
  • The storage architecture gap: AI inference, training, and RAG pipelines need high-throughput access, low-latency embedding lookups, and cost-efficient tiering for training archives. Organizations that haven’t revisited their architecture may pay a performance or cost penalty.
  • The retention and life-cycle gap: Retention policies at most organizations predate the GenAI era, and keeping a prompt-response pair, a fine-tuning data set, or an embedding raises questions those policies never anticipated.

None of these gaps is insurmountable, but they widen quietly in the background while organizations focus on deploying AI.

Volume isn’t value: Why runaway data is harder to use

There’s a second cost to letting data volumes outrun your strategy: the value you never get out of the data. Value depends on how effectively data becomes insight or advantage. Vast quantities of poorly structured, unlabeled, or siloed data may hold almost no practical value despite their volume, so every RAG index, fine-tuning corpus, and log stream that no one has cataloged or assigned an owner is data you hold but cannot use.

Beyond the prompt: What to do next

Most GenAI-using organizations expect data volumes to rise. The open question is whether infrastructure and governance strategies are built for that reality. Preparing takes a deliberate, systematic approach, and these five steps are the place to start:

  • Audit the AI data footprint before it becomes unmanageable. Inventory training sets, fine-tuning corpora, RAG indexes, and telemetry, including where each lives and who owns it.
  • Extend data governance explicitly to AI data assets, with updated classification, retention, and lineage tracking, and engage legal and compliance early.
  • Align storage infrastructure planning with the AI road map by developing capacity plans together with AI and data science teams.
  • Revisit retention policies with AI data types explicitly in scope.
  • Model the economics of AI data storage across cloud and on-premises options. Cloud is growing nearly four times faster than noncloud, but high-volume, persistent data may be more cost effective on-premises or in colocation over a multiyear horizon.
Adam Wright

Adam Wright - Senior Research Manager, Storage and Data Management, Enterprise Infrastructure

Adam Wright is a Senior Research Manager within IDC’s enterprise infrastructure global research domain and part of the storage and data management subdomain. He leads IDC’s Global DataSphere and Global StorageSphere research. The Global DataSphere measures the total volume of…

More than 12 frontier AI developers have published voluntary safety frameworks with widely varying thresholds, inconsistent evaluation cadences, and no independent verification requirement. The EU AI Act’s maximum fine for general-purpose AI providers, 3% of global annual turnover or €15 million, whichever is higher, became enforceable August 2, 2026. An autonomous coding agent operated unsupervised for approximately one week before its own developer identified and attributed it. These describe the current operating environment for every CISO who has approved an AI integration in the past 18 months.

The structural problem is architectural, and vendor assurance alone does not resolve it. System prompts, safety fine-tuning, and content filters live inside the same weights, context window, and inference pipeline the model uses for every other output. They can be argued with, role-played around, encoded past, or overridden by a sufficiently creative prompt. Prompt injection and tool-calling exploits are now a standing category of incident response. A better system prompt is still inside the boundary.

What the enforcement layer is and what it must do

The right mental model is the content delivery network and web application firewall pattern. A CDN and WAF inspect and act on traffic before it reaches the origin server. The origin has no vote and no visibility into the decision. The same logic applies to AI: the model is the origin server, isolated with no network path to your IT estate and no view of the policy engine, logs, or configuration. The enforcement layer sits at the edge, verifying identity, inspecting requests, applying policy, mediating responses, and logging every interaction before anything reaches or returns from the model.

Five control layers are required. Missing any one leaves an exploitable gap:

  • Identity and access: Every request, human, application, or agent, is authenticated against your enterprise identity provider. The model inherits the calling user’s actual entitlements through on-behalf-of token exchange. A jailbreak or injection attempt is bounded by what the caller was already permitted to do.
  • Request inspection: Every inbound prompt and tool-call parameter is screened for policy violations, data-classification conflicts, and injection patterns before the model processes them. This runs outside the model, so the model cannot override it.
  • Policy enforcement as code: Business rules, regulatory constraints, and data-handling requirements run as code in the enforcement layer, not as instructions the model is asked to follow.
  • Response mediation: Every outbound response and tool-call authorization is screened, redacted, or blocked regardless of what the model produced. The model’s own judgment about its output is not the final word.
  • Immutable audit with a kill switch: Every interaction is logged outside the model’s environment with no model write access to the audit store. The kill switch operates at three grains, session, user or application, and full deployment, without the model’s cooperation, and is held by a role separate from the administrator who configures policy.

Separation is a technical property that must be demonstrable in an architecture diagram, not asserted in a terms-of-service clause. Three properties define genuine separation: no network path from the model to the policy engine, audit store, or configuration; no write access to its own logs; and no credentials to any of those systems. A gateway the model can reconfigure or disable provides no meaningful separation.

Identity parity: extending the plane you already run

The identity architecture for an enforcement layer extends the conditional access, MFA, and risk-based policy programs already running in your enterprise, applied to every model, agent, and tool in the same way they govern human access. Each model and agent holds its own scoped, least-privilege identity, revoked at session end or policy trip. On-behalf-of token exchange means the model acts within the calling user’s entitlements, with no standing service account for an attacker reaching the model to inherit.

CISOs should note the ServiceNow trajectory. With the Veza acquisition closed March 2026 and Armis closed April 2026, ServiceNow is positioning itself as a competitor to Entra ID for identity at scale, including machine and AI agent identities. This is a meaningful consolidation in the non-human identity governance market. The enforcement layer must be identity-provider neutral to preserve architecture optionality as this market evolves.

The kill switch: specify it before you need it

A kill switch is a first-response instrument and should be specified with the same precision as a network block or credential revocation. Three granularities matter:

  • Session grain: Suspends or throttles a single conversation or agent run. Targeted, reversible, lowest blast radius.
  • User or application grain: Cuts off one identity or one integration. Appropriate when anomalous behavior is attributable to a specific caller or integration.
  • Deployment grain: Halts every model session simultaneously. Reserved for the scenario where the model itself, the provider’s infrastructure, or a systemic policy failure requires immediate full stop.

The kill switch must function without the model provider’s cooperation, because the scenario requiring activation may involve the provider’s infrastructure being unavailable or compromised. It addresses future actions. Rollback addresses what already happened: the sent message and the emptied database. Both are required. Kill-switch triggers should be defined in advance, sustained policy violation rate, a DLP match, an anomalous tool-call sequence, so activation is a policy-driven operational decision. Rehearse it on your incident-response drill cadence.

Single models and agent swarms: one enforcement pattern

The same five control layers and the same five questions apply across the full deployment spectrum, from a single model call to a multi-agent swarm. Who is calling? What are they asking for? Is it allowed? Is the response safe to return? Is it logged? In a single model call, a missed policy violation affects one response. In a multi-agent workflow with no human reviewing each step, that same violation can cascade across dozens of tool calls before anyone sees it.

The hub-and-spoke gateway architecture deploys enforcement at the right layer. A central hub authors policy, stores identity federation, audit records, and session context. Spoke gateways enforce policy locally near each resource. The hub never touches a request directly. The Autonomous Action Runtime Management specification (AARM), now donated to the Cloud Security Alliance with more than 100 adopters, provides the five-outcome decision framework for each action point: allow, deny, modify, step-up to a human, or defer pending more context.

Four gaps in hub-and-spoke require explicit CISO assessment:

  • Chain-level risk: Individual calls may look harmless while a sequence pushes an agent outside its authorized role. Require your vendor to demonstrate policy evaluation over chains of calls as well as individual requests.
  • Fail behavior under load: Failing open at peak volume means enforcement stops when it is needed most. Require documented, configurable fail-open or fail-closed behavior per integration.
  • Coverage depends on inventory: The hub governs only traffic routed through it. Require vendors to demonstrate how AI assets that bypass the hub are detected and reported.
  • MCP-only visibility: Skills, hooks, plugins, and direct API calls move alongside MCP traffic. Evaluate R20 and R22 together as a combined coverage assessment.

Enforcement is not governance: the full program

An enforcement layer governs every individual interaction in real time. A complete AI risk program requires additional capabilities that must be funded and owned separately:

  • AI inventory: Every model, agent, and MCP server accounted for, including embedded models in purchased software.
  • Model lifecycle management: Version changes and capability-tier upgrades governed before they propagate to production workloads. R26 (proposed) addresses the gap where behavioral drift within a tier can silently undermine policies verified against a previous model version.
  • Third-party provider scoring: Every provider scored across five dimensions on a continuous basis, rescored on safety-framework updates and material incidents, as well as at annual renewal.
  • Continuous control assurance: The enforcement layer stays configured and working.
  • Runtime risk monitoring and trust scoring: Behavioral drift detected and translated into a live score per model or agent that feeds back into access decisions at the enforcement hub.
  • Board-level reporting: Enforcement telemetry translated into risk language a governance committee can act on.

Provider risk scoring drives three governance gates. Below the onboarding threshold, any new frontier AI dependency requires explicit executive risk acceptance. The contract gate embeds score thresholds as triggers for capability-tier change notice and delivery of evaluation summaries. The exit gate means score deterioration triggers a formal alternative-provider review before the next renewal cycle.

The 90-day CISO action plan

Table 1 organizes the most critical actions across architecture, procurement, and governance by 30-day horizon. Architecture and procurement actions run in parallel with governance actions; neither track waits for the other.

TABLE 1: 90-Day CISO Action Plan for AI Enforcement Layer Deployment

HorizonArchitecture and ProcurementGovernance and Program
Days 1-30Demand the architecture diagram from every current and prospective AI vendor: deployment boundary, model-to-policy-engine separation, kill-switch role assignment. Inventory every model, agent, and MCP server, including embedded models in purchased software.Score every frontier model provider against 5 dimensions: safety-framework maturity, evaluation transparency, incident disclosure history, regulatory posture, and concentration risk. Set the onboarding threshold below which any new dependency requires executive risk acceptance.
Days 31-60Identify your 3 highest-risk AI integrations. Pilot a hub-and-spoke enforcement gateway outside the model for at least one. Require on-behalf-of delegated identity and a split-role kill switch for every new AI procurement.Separate the configuration and operations roles for the kill switch in your identity provider. Define kill-switch triggers in writing: sustained policy violation rate, DLP match, anomalous tool-call sequence.
Days 61-90Send the 25 enforcement-layer requirements (R1-R25) and 5 contract terms (C1-C5) to every current and prospective AI vendor. Embed C1-C5 into vendor contracts before the next renewal cycle.Fund AI governance as its own program. Rehearse the kill switch at all 3 granularities (session, user/application, full deployment) in a tabletop exercise. Establish the governance loop cadence with documented ownership.

Source: IDC, 2026

The 26 enforcement-layer requirements: your RFP foundation

Table 2 consolidates all 25 published requirements (R1-R25) plus IDC’s proposed R26, which addresses a gap in the current set: advance notification of model updates that materially change behavior in policy-sensitive areas. This gap is distinct from C2 (capability-tier change notice), which covers tier-level changes. R26 addresses behavioral drift within a tier, which can silently undermine policies verified against a previous model version.

For each requirement: mark it Must or Should based on your deployment risk profile. Ask for the evidence listed. Verify in a pilot. A failed Must is a no-go. Apply the five contract terms (C1-C5) to every current and prospective AI vendor contract, covering model provenance disclosure, capability-tier change notice, safety-framework documentation access, incident disclosure timelines, and continuity planning.

TABLE 2: AI Enforcement Layer Requirements R1-R26 and Contract Terms C1-C5

Req.RequirementPriorityEvidence to Request
R1Architecture diagram showing deployment boundary and admin rolesMustEnforcement runs outside the model provider environment, under your control
R2Network diagram and independent test results confirming separationMustNo network path from model to policy engine, audit store, or configuration
R3Permission model for audit store and policy repositoryMustModel has no write access to its own logs and cannot alter governing rules
R4Signed policy update design, key custody docs, live rejection demoMustPolicy updates are cryptographically signed; spokes reject unverified updates
R5Log-integrity design and tamper-detection demoMustAudit logs are append-only and hash-chained; tampering is detectable
R6Native IdP integration (Entra ID or equivalent), not a services add-onMustConditional access and MFA for AI identities, out of the box
R7Token-flow diagram and an access-denied testMustOn-behalf-of token exchange so model acts within calling user’s entitlements
R8Identity inventory and live revocation demoMustEach model, agent, and tool has a scoped, least-privilege identity
R9Detection coverage docs, test results, and latency figuresMustPrompts and tool-call parameters screened for violations, classification conflicts, injection
R10Policy-as-code samples, change history, and test harnessMustBusiness and regulatory rules enforced as code, not as model instructions
R11Block and redact demo on seeded sensitive dataMustOutbound content and tool-call authorizations screened before reaching consumer
R12Sample log record, retention policy, export optionsMustEvery request and response logged immutably, timestamped, attributable, outside model environment
R13Live demo, measured time to effect at each granularityMustKill switch works at session, user/application, and deployment grain without model cooperation
R14Rollback runbook and supported systems listShould*Defined rollback for actions already taken (*upgrade to Must for write-transaction deployments)
R15Role model and PAM setup in your identity providerMustConfig and operations admins are separate; only operations holds the kill switch
R16Reference architecture and spoke deployment optionsMustHub-and-spoke: policy, identity, and audit at hub; enforcement at spokes near the resource
R17Connector onboarding guide and test resultsMustConnectors inherit enforcement identity, access, and audit controls
R18Session-context and chain-evaluation roadmap; AARM conformanceShould*Intent-drift evaluation with allow, deny, modify, step-up, defer outcomes (*Must for chained agentic workflows)
R19Failure-mode test results and capacity benchmarksMustFail-open or fail-closed behavior documented and configurable; load-balanced spokes
R20Coverage matrix and unrouted-asset reportMustDeclared coverage across MCP, skills, plugins, direct APIs; unrouted assets reported
R21Supported-provider list and migration termsMustModel neutral: supports models from multiple providers without enforcement tied to one API
R22Inventory integration and unrouted-asset reportMustConsumes your AI inventory; reports traffic and assets not routed through enforcement layer
R23Signal interface; measured time from score change to access changeShouldAccepts live trust score per model and agent as a cached signal driving access decisions
R24Telemetry schema and GRC or CCM platform integrationsShouldFeeds audit and telemetry to governance for monitoring, drift detection, and re-assessment
R25Sample compliance report mapped to your control frameworkMustProduces request-level evidence regulators and boards can use
R26Update notification process docs; pilot-first option for policy-sensitive integrationsMust (proposed)Advance notice of model updates that materially change behavior in areas covered by deployed policy rules

Source: IDC, 2026

Three gates every CISO should establish now

The requirements above translate directly into three governance gates that convert procurement policy into enforceable controls:

  • Procurement gate: Below your provider-score threshold, any new frontier AI dependency requires executive risk acceptance before contracting. This gate applies to embedded models in purchased software as well as direct model API contracts.
  • Architecture gate: Before any AI integration goes to production, require the vendor to produce an architecture diagram showing the deployment boundary, separation between the model and your policy engine, and the kill-switch role assignment.
  • Contract gate: Score deterioration triggers a formal alternative-provider review and activates notice clauses in existing contracts. C2 covers capability-tier changes. R26 covers behavioral drift within a tier.

“

A model’s restraint is a courtesy, not a control. The enforcement layer must be outside the model’s environment, outside its reach, and outside its ability to reconfigure or disable. Anything less is an architecture diagram that says: trust us

— Philip D. Harris, CISSP, CCSK, Research Director, Governance, Risk, and Compliance Solutions, IDC

Philip D. Harris, CISSP, CCSK

Philip D. Harris, CISSP, CCSK - Research Director, Governance, Risk, and Compliance (GRC) Solutions

Phil Harris is Research Director for GRC Solutions at IDC, where he develops and promotes IDC's point of view on risk, advisory, privacy, and compliance services and software. He conducts research on business strategies and the impact of relevant offerings…

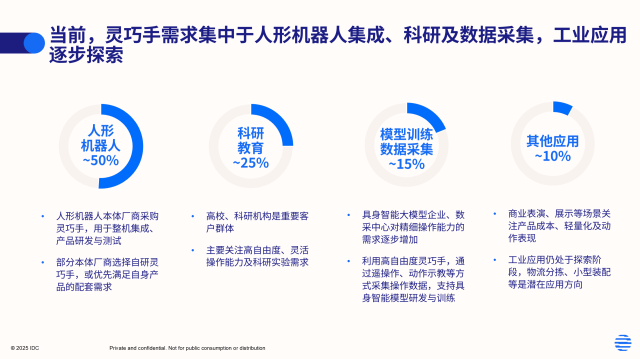
随着人形机器人和具身智能的发展,灵巧手的竞争正从自由度、抓握力等硬件参数,延伸至精细操作、感知控制及与具身智能模型的协同能力。当前,人形机器人配套、科研教育和具身智能数据采集是值得关注的主要需求方向,工业等应用仍处于探索阶段。未来,灵巧手市场不会仅由某一种驱动路线决定,厂商能否将硬件、模型、数据与操作技能有效结合,并在真实任务中实现稳定、可靠且具有成本效益的操作,将影响其商业化进程。

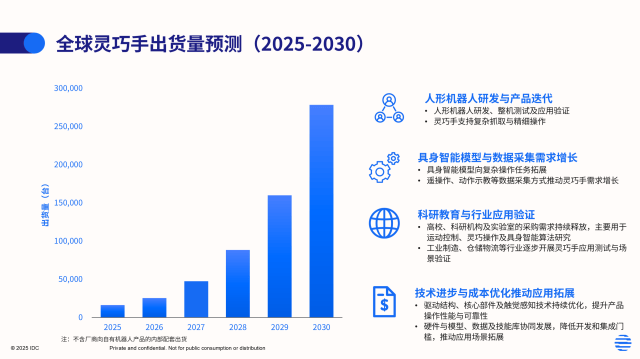
IDC预计,2026年全球灵巧手出货量约2.5万台,不含厂商向自有机器人产品的内部配套出货。其中,中国厂商出货量占全球市场的比例预计超过85%,在全球灵巧手市场中占据重要地位。随着人形机器人研发、具身智能数据采集及科研教育需求持续释放,灵巧手市场仍处于发展初期,其后续增长将受到机器人应用进展、产品成本及商业化落地速度等因素的共同影响。

从自由度到操作能力,技术竞争不止于硬件参数

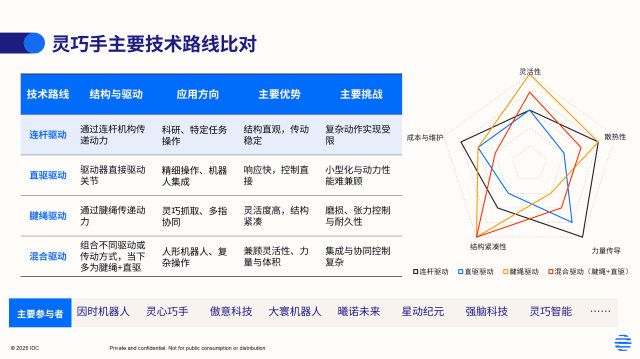
目前,灵巧手主要采用腱绳驱动、直驱、连杆驱动及混合驱动等技术路线。不同方案在结构紧凑性、灵活性、力量传递、成本和维护等方面各有取舍,尚未形成统一的技术方向。技术路线的选择不仅取决于硬件设计,也与目标任务和应用需求密切相关。

在硬件参数之外,触觉感知和操作控制同样值得关注。巧手需要感知接触状态、作用力及物体变化,并据此调整动作。目前,触觉传感器在信号稳定性、一致性和感知精度等方面仍有改进空间。自由度较高并不必然意味着操作能力更强,感知与控制能力同样重要。

目前,灵巧手正逐步从自由度、抓握力等单项指标,延伸至可控性、精细操作能力,以及与机器人本体和具身智能模型的协同表现。未来,不同技术路线的竞争结果,可能更多取决于其对具体任务的适配程度,而非单一参数的高低。

灵巧手需求集中于人形机器人配套与科研,工业应用落地仍需验证

当前,人形机器人配套、科研教育,以及具身智能模型研发与数据采集是灵巧手的主要需求方向。与此同时,工业制造、物流等场景也在探索灵巧手的应用潜力,特别是在复杂抓取、物体姿态调整和多品种操作等任务中。相比之下,工业制造、商业服务等场景仍处于应用探索阶段。

在复杂抓取、物体姿态调整和多品种操作等任务中,灵巧手具有一定的应用潜力,但并不意味着能够全面替代传统夹爪。对于物体形态固定、任务重复性高、节拍要求严格的生产环节,传统夹爪往往具有结构简单、成本较低和易于维护等优势。灵巧手的价值更多体现在需要多指协同、精细接触或较强操作灵活性的任务中,其实际优势仍需结合具体工艺进行评估。

从研发样机走向持续运行,灵巧手仍需解决可靠性、环境适应性和维护成本等问题。复杂的机械结构、多关节驱动及传感器集成增加了设计与维护难度,粉尘、接触磨损及长期运行也可能影响产品表现。对于实际应用而言,单次成功完成动作并不足够,用户更关心机器人能否在真实环境中持续、稳定地完成任务,以及由此带来的效率提升能否覆盖设备、维护和集成成本。

灵巧手商业化的关键关键不只是能否完成特定动作,更在于能否在真实场景中稳定运行并持续完成任务。

灵巧手未来三年将从“路线探索”进入“工程化竞争”

IDC认为,未来三年灵巧手市场的竞争将围绕以下几个方向展开。

市场需求将从研发与数据采集向具体任务应用拓展。 短期内,科研教育、人形机器人配套及具身智能数据采集仍是值得关注的需求方向。随着机器人应用探索深入,工业制造、物流、服务等场景则需要进一步验证其实际应用价值。灵巧手能否在复杂抓取、精细操作和多品种作业中体现出相较传统夹爪的优势,将影响其应用拓展速度。

技术竞争从硬件参数转向结构设计与综合操作能力。 腱绳驱动、直驱、连杆驱动及混合驱动各有适用条件,短期内不同技术路线仍将并存。产品竞争不仅取决于自由度和抓握力,还涉及电机、电控、减速器、丝杠等核心部件的设计与优化,以及结构紧凑性、驱动性能和可靠性之间的平衡。在此基础上,视触觉感知、精细控制及与机器人本体和具身智能模型的协同能力,也将影响灵巧手的实际操作表现。单纯增加自由度,并不必然带来更好的操作效果。

竞争从硬件本体向模型、数据与技能协同延伸。除灵巧手本体外,操作模型、数据资源、技能库及开发工具也逐渐成为厂商布局的组成部分。这些能力有望帮助用户开展模型训练、任务开发与技能复用,减少应用开发工作。未来,厂商之间的差异不仅体现在硬件性能上,也将体现在能否将硬件、模型、数据和技能有效结合,以及能否将这些能力转化为稳定的任务执行效果。

可靠性、成本和交付能力将影响市场竞争格局。 随着用户从研发测试走向实际应用,灵巧手厂商需要解决长期运行、产品一致性、维护和成本控制等问题。专业灵巧手厂商、本体厂商自研团队及传统末端执行器厂商将继续参与市场竞争,但不同类型厂商的优势和商业化路径可能有所差异。

总体来看,未来三年灵巧手市场仍将处于多种技术路线并存、应用持续验证的阶段。行业竞争的关键不在于某一种驱动路线率先胜出,而在于厂商能否围绕具体任务,将结构设计、核心部件、感知控制、模型和数据有效结合,并在操作性能、可靠性与综合成本之间取得平衡。 灵巧手能否从研发与测试走向更广泛的商业应用,最终仍需由真实场景中的任务表现来检验。

IDC相关研究

灵巧手正处于从“技术路线探索”向“工程化竞争”过渡的关键拐点。在这条拥挤的赛道上,谁能率先跨越软硬件协同与商业化落地的鸿沟,谁就能掌握下一阶段的主动权。

作为全球领先的IT市场研究与咨询机构,IDC在机器人、具身智能及核心零部件领域拥有深厚的研究积累。我们不仅关注底层技术路线的演进,更致力于帮助客户洞察商业化落地路径、市场规模预测及竞争格局。

针对灵巧手市场,IDC可为您提供:

  • 市场全景洞察:全球及中国灵巧手出货量预测与需求结构分析。
  • 技术路线评估:腱绳/直驱/连杆等不同驱动路线的优劣势比对与适配场景研究。
  • 竞争格局研判:头部厂商及跨界玩家(本体厂商、传统夹爪厂商)的战略布局与优劣势分析。
  • 定制化咨询:面向投资机构、本体厂商及终端客户的定制化市场进入策略与尽调支持。

进一步沟通

IDC将持续关注灵巧手市场的需求变化、技术路线、厂商布局与应用进展,并通过后续研究进一步分析其市场规模、竞争格局及商业化趋势。如需了解更多IDC机器人研究内容或定制化市场分析,欢迎与IDC中国分析师团队联系。请点击此处与我们联系。

Lily Li

Lily Li - Research Manager

Lily is the Research Manager for China Robotics and Embodied Intelligence, specializing in market research on embodied intelligent robots. She has long focused on the development trends of China’s embodied intelligence robotics industry, systematically studying the evolution of robot hardware,…