Apple used this cycle to launch its first foldable iPhone, the iPhone Duo, alongside the iPhone 18 Pro family, Apple Watch Series 12 and Ultra 4, AirPods 5 and to widen the Apple Intelligence and Siri AI story across the range. The iPhone Duo is the flagship, a test of whether design, ecosystem and premium positioning can reshape a segment that has largely failed to appeal to the mainstream consumer.

Pricing was at the center of the event. At a time when we expected prices to rise beyond what consumers are comfortable paying due to memory costs, Apple held its increases below what we expected. The iPhone 18 Pro arrives at $1,199 and the Pro Max at $1,299, each only $100 up from last year (we expected at least a $150 increase). The company kept the starting price of its new Apple Watch Series 12 and Ultra the same as last year ($399 and $799). AirPods 5 bring active noise cancellation to a $129 entry point, $50 below the $179 price of the noise-cancelling AirPods 4. The foldable, Apple’s most expensive iPhone yet, starts at $1,999 versus an industry expectation of $2,499, which was the biggest surprise of all. Apple expanded the number of products it offers at mainstream prices and opened a super-premium tier at the top, all in a single keynote.

Apple Watch and AirPods strengthen the ecosystem
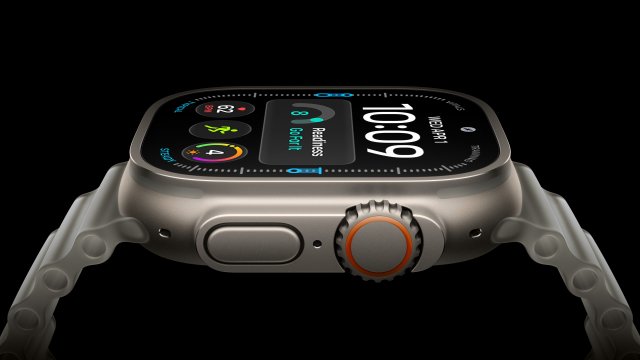
Apple Watch Series 12 and Ultra 4 put health sensing at the center. Both use the Apple S11 chip and a redesigned sensing system that reads heart rate every five seconds and heart-rate variability every five minutes, enough for continuous measurement rather than the isolated readings of previous versions. The new Readiness score combines training load, vitals and sleep quality, and the redesigned Health app adds Insights, Longevity and a Health Age metric, with Apple Intelligence underneath it. The proposition is moving from measurement toward interpretation and guidance, and looks to bring Apple into line with fitness-focused devices and services such as Whoop.

Audio Intelligence features on the watches, designed to help you hear what you missed (Live Rewind), capture sounds (Sound Recognition) or capture notes (Siri Recap), find Apple attempting to walk a fine line between always-listening ambient AI computing and its desire to respect users’ privacy.

AirPods 5 apply the same pricing logic lower down the range. The $129 model brings ANC to the entry point, and the $149 version adds volume swipe, wireless charging and an extra hour of battery. Apple says the new ANC is 50% better than its prior open-ear model with ANC. Lowering the entry price pulls more people into a companion device they rarely give up.

iPhone 18 Pro Series reinforces the premium core
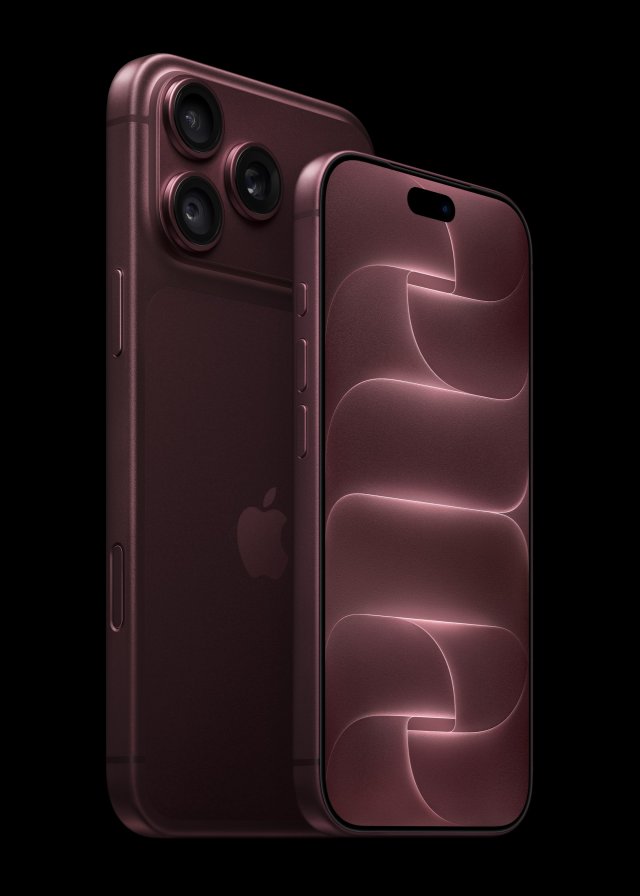
The iPhone 18 Pro and Pro Max defend the conventional flagship through performance, imaging and AI. The A20 Pro runs on-device Apple Intelligence, with Private Cloud Compute handling heavier work, and the 48MP Fusion main camera adds a physical variable aperture as wide as f/1.48. The most notable addition is Apple Reference Image, which signs pixel-level data at the sensor so a user can prove a photo was captured on the device and not altered. These products hold the premium core in place while the Duo enters above it, the Pro at $1,199 for 256GB and the Duo at $1,999 for the same storage.

18 Base Model moves to spring, redefines cadence

While the spotlight is on the Duo today, an important factor is the silent omission of the 18 base models. Apple’s shift of the base iPhone 18 to spring is a portfolio decision, decoupling the base models from the premium lineup in the fall.  According to IDC, the last two base iPhone launches drove 16% of Apple’s total shipments in their first two quarters, though as lower-ASP devices their share of revenue runs below that unit figure. The new cadence allows Apple to even out its performance seasonality throughout the year and give each line clearer positioning. 

Apple has also diversified its iPhone lineup into six different models, widening its demographic reach.  The six are clearly grouped into two categories: the premium line (Pro, Pro Max, and Duo) launches in the fall; the budget-friendly line (base, E, and Air) follows in the spring. Each wave of devices gets a clear commercial narrative instead of six SKUs competing for the same spotlight.

iPhone Duo changes the foldables equation

The iPhone Duo is a polished piece of first-generation hardware.  It positions foldability as a finished product rather than a work in progress. It pairs a 7.6-inch internal Super Retina XDR display with a 5.4-inch external one and runs on the A20 Pro with a dedicated display engine and a custom titanium hinge of more than 100 components, high-strength glass and a nano-texture finish meant to cut glare and play down the crease.

 The software is the more differentiated part, with fluid transition from closed to open, intuitive execution of side-by-side apps, paired apps for repeated workflows, content movement between them, use in partly folded orientations and a redesigned standby, with Apple Pencil USB-C support due later this year. The point is to make the larger display more useful in day-to-day use rather than just feeling like a bigger phone. As with any first-generation foldable, the open questions are hinge and display durability over time and how the crease and added weight hold up in daily use.

Pricing starts at $1,999 for 256GB and passes $3,000 at 2TB of storage. That entry sits $500 below the $2,499 the market expected, and at roughly 1.6 times Apple’s non-foldable iPhone ASP of around $1,209. IDC still puts the blended iOS foldable ASP higher once storage mix is counted. Apple has not built a mass-market device. It has created a premium product for high-value iPhone users, which lets the Duo lift both foldable volume and Apple’s premium mix.

A value opportunity, not a volume-led category

IDC’s forecast explains why the Duo can matter even if foldables stay a small share of the market. Worldwide foldable value grows from $26.7 billion in 2025 to $42.0 billion in 2026 and $68.2 billion by 2030, a 20.6% CAGR from 2025 to 2030, while units rise from 20.3 million in 2025 to 35.8 million in 2030. Value grows faster than volume, which is what makes the segment worth Apple’s attention. Foldables move from 2.2% of global smartphone units in 2026 to 3.1% in 2030, but their revenue share climbs from 6.9% to 10.0%.

Apple does not need unit leadership for the Duo to pay off, though its design and price could deliver that as well. Supply may be the initial constraint, as Apple’s exacting standards make the unit hard to manufacture in large volumes at the start. We expect the company to ship roughly ten million units in the first 12 months. With Android foldable units forecast to fall this year, IDC expects Apple’s entry to be the main driver returning the segment to growth. The gap between value and unit share is the key: Apple can take a disproportionate share of category revenue by setting the premium reference point.

The China Test

China is the toughest test for the Duo, and also its clearest value opportunity. Huawei led the market with 79.4% of foldable units and 82.2% of value in the second quarter of 2026, backed by an established range, market familiarity and channel strength. IDC projects iOS foldables in China to reach 2.0 million units and $4.9 billion in value in 2026, rising to 4.4 million units and $10.3 billion by 2030, with Apple’s share of China foldable value growing to 50.8% and its unit share to 39.7% over the same period.

Apple leads on value well before it leads on units, which fits a premium entry priced above the rest of the market. The requirement is execution: industrial design, durability, display quality and app support strong enough to trade buyers up in a market that already has credible alternatives. If it gets that right, Apple can take a meaningful share of category value, helped by its standing as an aspirational brand. Get it wrong, and Huawei’s entrenched lead and China’s support for homegrown brands could hold the Duo to a niche.

What the September lineup signals

Taken together, the lineup reads as one strategy: AirPods lower the barrier to a premium feature, Apple Watch adds health value while holding price, the iPhone 18 Pro defends the premium core with measured discipline, and the iPhone Duo opens a new high-value tier below the price the market expected. Each move serves a larger active installed base, more multi-device ownership and stronger ecosystem attachment, with Apple Intelligence and Siri AI as the connective layer and on-device processing supporting the privacy story.

The real test for Apple is whether it can make foldables a more valuable category, own the defining premium product and use that position to extend the economics of the iPhone portfolio. IDC’s forecast suggests it can, with Apple positioned to be a principal driver of category growth through 2030.

Getting there requires strong first-generation execution, a convincing software story, and a credible strategy in China. Deliver those and the iPhone Duo stops being a new form factor and becomes a margin engine and a mix lever, and a sign Apple can still shape a category it entered years after competitors did. 

Francisco Jeronimo

Francisco Jeronimo - VP, Data and Analytics, Devices, IDC EMEA

Francisco Jeronimo is VP for Data and Analytics at IDC EMEA. Based in London, he leads the research that covers mobile devices, personal computing devices, emerging technologies and the circular economy trends across EMEA. His team delivers data on personal…
Tom Mainelli

Tom Mainelli - Group Vice President, Device & Consumer Research

Tom Mainelli heads the Device & Consumer Research Group, overseeing a wide array of hardware and technology categories catering to both home and enterprise markets. His team's research spans PCs, tablets, smartphones, wearables, smart home devices, thin clients, displays, and…
Nabila Popal

Nabila Popal - Senior Director, Data & Analytics

Nabila Popal is Senor Director with IDC's Data & Analytics team, specializing in Mobile Phones, PC Monitors and other consumer devices.  Ms. Popal is responsible for the global research and quality and timely delivery for her respective technologies, coordinating with regional…

The worldwide WLAN market reached $3.2B in the second quarter of 2026 (2Q26), growing 23.2% year over year (YoY). That’s an acceleration from the 15.6% growth in 1Q26. The quarter’s growth reinforced Wi-Fi 7 (802.11be) as the new dominant Wi-Fi standard in the enterprise.

The results span all major regions and vendor tiers. The market has moved past its early-adoption phase into a full replacement cycle.

WLAN market highlights

  • Total market: The worldwide WLAN market grew 23.2% YoY in 2Q26, reaching $3.2B. That’s a meaningful acceleration from the prior quarter. The enterprise dependent access point (AP) segment grew 27.6% YoY to $2.7B, outpacing the broader market and reflecting sustained corporate investment in dependent wireless infrastructure. The pace of growth suggests that enterprise Wi-Fi refresh cycles are broadening beyond early adopters to mainstream deployment.
  • Wi-Fi 7 momentum: Wi-Fi 7 dependent AP revenues reached $1.4B in 2Q26, representing 53.0% of enterprise dependent AP revenues and growing 219.5% year over year. This transition reflects the convergence of a maturing Wi-Fi 7 product ecosystem, enterprise demand for higher-throughput infrastructure, along with the pull-forward effect of AI-driven network requirements and AI-powered wireless management.
  • Wi-Fi 6/6E trajectory: As Wi-Fi 7 adoption continues, earlier-generation standards are declining in share. Wi-Fi 6 accounted for 29.4% of enterprise dependent AP revenues in 2Q26 (down from 34.8% in 1Q26), while Wi-Fi 6E held 16.9%. Both previous-generation standards remain relevant in phased enterprise rollouts and mid-market deployments. In new projects, though, Wi-Fi 6/6E investment has largely given way to Wi-Fi 7.
  • Regional performance: Growth was broad-based across all three regions in 2Q26. EMEA led with 32.2% YoY growth, reaching $1.0B supported by enterprise refresh investment and expanding Wi-Fi 7 adoption across Western and Central Europe. The Americas grew 21.6% YoY to $1.5B, maintaining its position as the largest regional market. APJ expanded 15.2% YoY to $708.1 million.

Vendor highlights

The 2Q26 vendor field reflects a market in active expansion, with the top five vendors posting revenue growth.

Cisco: Cisco posted $1.3B in enterprise WLAN revenues in 2Q26, growing 27.2% YoY and maintaining its position as the market share leader with a 39.0% share. Cisco’s growth reflects enterprise demand across its Wi-Fi 7 portfolio and continued momentum in large campus and branch deployments. Cisco’s scale and long-standing enterprise relationships keep it entrenched in complex, multi-site deployments, backed by a go-to-market channel that’s hard for smaller vendors to match.

HPE/Juniper: The combined HPE and Juniper entity posted $557.2 million in enterprise WLAN revenues in 2Q26, growing 7.5% YoY with a 17.2% market share. While the growth rate is more moderate than its peers this quarter, HPE’s Aruba and Juniper Mist AI-driven platforms remain the pick for enterprises that prioritize AIOps and cloud-managed deployments, particularly those consolidating wired and wireless management under one roof.

Ubiquiti: Ubiquiti posted $415.9 million in 2Q26 revenues, growing 33.1% YoY with a 12.8% market share. Its continued above-market growth reflects traction in the mid-market and among managed service providers, where the company’s competitive pricing and rapid Wi-Fi 7 product refresh are leading to consistent revenue momentum.

Huawei: Huawei posted $339.7 million in 2Q26 revenues, growing 44.0% YoY and reaching a 10.5% market share, up from 6.0% in 1Q26. Growth was driven by its Wi-Fi 7 campus portfolio and integrated campus networking solutions, with standout performance in markets across Asia Pacific and EMEA where Huawei holds established enterprise customer relationships.

Vistance Networks: Vistance Networks (formerly CommScope/Ruckus) posted $107.2 million in 2Q26, growing 9.9% YoY with a 3.3% market share. The Ruckus portfolio continues to hold its position in high-density verticals including hospitality, education, and large venues, where its enterprise-grade quality and deployment flexibility remain competitive differentiators. In April 2026, Belden announced its intent to acquire Ruckus Networks from Vistance Networks, a $1.85B deal that closed in July 2026.

WLAN Top Companies Chart

Market dynamics

Wi-Fi 7 as the new enterprise baseline

The 2Q26 results confirm that Wi-Fi 7 is no longer a premium upgrade choice, rather it has become the default selection for enterprise wireless procurement. The speed and breadth of this transition is driven by a combination of factors: a broad hardware refresh cycle that has created natural replacement demand across installed Wi-Fi 5 and early Wi-Fi 6 deployments; a matured vendor product portfolio that has brought Wi-Fi 7 to competitive price points across all market tiers; and the pull-forward effect of enterprise AI adoption, which is raising throughput and latency requirements across office environments, campuses, and branch sites.

Related: Watch IDC’s take on what’s driving the shift in The Rise of Wi-Fi 7 in Enterprises.

Memory Constraints Strain WLAN Economics

Persistent supply chain headwinds caused by industry-wide memory shortages continue to extend lead times and increase average selling prices (ASPs) across the enterprise WLAN market, forcing enterprise buyers into difficult trade-offs. Organizations are choosing between accelerating purchases to secure inventory or deferring deployments to manage costs, reshaping buying patterns as cost-conscious enterprises prioritize strategic deployments while others absorb premium pricing.

“

Strong 2Q26 results in the enterprise WLAN market underscore a market in full transition. The campus refresh cycle is accelerating across regions, driven by the convergence of Wi-Fi 7, multi-gigabit switching, and AI adoption. Organizations are modernizing networks to support AI workloads while simultaneously leveraging AI and agentic capabilities to streamline engineering and operations. Despite supply chain headwinds, IDC expects momentum in the enterprise wireless industry to continue as organizations across the globe prioritize network modernization in the AI era.

— Brandon Butler, Senior Research Manager, Network Infrastructure & Services, IDC

Why it matters

  • Who should care? CIOs, network architects, and IT procurement teams making refresh decisions in the next 12-18 months should treat Wi-Fi 7 as the standard starting point, not an optional upgrade. The market has moved: vendors are shifting development and supply chain focus to Wi-Fi 7, and the price premium over Wi-Fi 6 is narrowing rapidly. Deferring Wi-Fi 7 now means retrofitting networks to meet AI application requirements sooner than expected.
  • Business impact: The acceleration in enterprise WLAN growth, 23.2% YoY, up from 15.6% in the prior quarter, reflects real enterprise budget commitment to wireless modernization. Organizations that have invested in Wi-Fi 7 infrastructure are building the connectivity foundation for AI-powered collaboration, real-time location services, and high-density mobile workloads. The TCO calculus increasingly favors Wi-Fi 7 over incremental Wi-Fi 6E upgrades.

What’s next for the WLAN market

IDC expects the enterprise WLAN market to sustain growth through the second half of 2026, with Wi-Fi 7 continuing to consolidate its dominant position, despite supply chain headwinds. As the enterprise installed base of Wi-Fi 6 and 6E access points continues to mature, the addressable refresh opportunity remains substantial. Demand from AI-intensive applications (spanning inference at the edge, high-density video, and IoT integration) will continue to pull forward network investment decisions. Integrated, secure networking is another key driver in the refresh opportunity.

The competitive dynamics established in 2Q26 are likely to persist. Cisco’s scale advantage in large enterprises is durable, but Huawei’s trajectory and Ubiquiti’s mid-market momentum mean that market share will remain actively contested. Macro risks, including regional economic uncertainty and supply chain disruptions, are real watch items for the back half of the year. None of them have shown up yet in the refresh demand IDC is tracking.

Brandon Butler

Brandon Butler - Senior Research Manager, Networking and Infrastructure Services, Enterprise Infrastructure

Brandon Butler is a Senior Research Manager within IDC’s enterprise infrastructure global research domain and part of the networking infrastructure and services subdomain. His research covers market and technology trends, forecasts, and competitive analysis in enterprise campus, branch, and edge…
Petr Jirovsky

Petr Jirovsky - Senior Research Director, Networking and Infrastructure Services, Enterprise Infrastructure

Petr Jirovsky is a Senior Research Director within IDC’s enterprise infrastructure global research domain and part of the Networking and Infrastructure Services subdomain. He provides quantitative insights on network infrastructure for the datacenter, cloud, and campus/branch environments. He serves as…
Diego Anesini

Diego Anesini - VP Data and Analytics, Networking

Diego Anesini serves as Vice-President, Data & Analytics, Networking. Prior to this position, Diego held various roles in the company. The most recent was VP, Data & Analytics for Latin America. He has extensive experience in the Networking, Telecom and…

The AI line item on this quarter’s cloud invoice doesn’t match anything in the forecast tab. Six months ago it was a rounding error. Now it’s the fastest-growing number in the budget, and finance, IT, and the vendor each have a different answer for who owns it.

What is token economics, and why is it suddenly a CFO problem?

Token economics, or “Tokenomics,” is the financial discipline of measuring, benchmarking, and governing what an enterprise pays per unit of AI inference (the token), instead of treating AI spend as an extension of software licensing. This year, the Linux Foundation formalized the discipline by launching the Tokenomics Foundation, with founding support from Google Cloud, IBM, Microsoft, SAP, Accenture, and JPMorganChase. A dozen of the world’s largest technology and financial institutions agreeing to standardize how AI cost gets measured is itself the signal: AI spend had gotten too complicated to track the old way.

Why AI costs don’t behave like software licensing

A seat count is predictable. A token count is not. It moves with every prompt, every agent reasoning step, and every tool call an application makes on a user’s behalf, and it can double inside a single product decision an engineering team makes without ever looping in finance. IDC research puts a number on how unevenly that cost lands: output tokens run 3 to 5 times more expensive than input tokens, and a multiagent pipeline that isn’t monitoring its input-to-output ratio can understate its true inference cost by 3x or more. Two enterprises already know what that miscalculation costs in dollars: one exhausted an entire year’s AI budget by April after rolling out a coding assistant at scale, and a hospital system logged more than $6 million in unplanned charges before its finance team traced the source.

Who actually owns the AI budget line?

The deeper problem isn’t the invoice. Only one in five CEOs have created a separate AI budget line in the first place, which means for most enterprises this spend is still buried inside a budget that was never built to isolate it. CFOs now influence more than two-thirds of enterprise technology investment decisions, while CIOs remain essential for the technical build. That’s two roles with converging influence and a mandate that hasn’t caught up. Nearly three in four organizations already name excessive AI spending a major risk to their future technology investment plans.

“

Every dollar of wasted AI agent spend is a governance failure.

— Shari Lava, Group VP of AI, IDC

Eighteen months ago, that framing would have stayed inside IT. Now it’s pushing the ownership question into board-level conversations, next to the AI budget line itself.

What CFOs can do now: Building a full-stack token cost model

The starting point is visibility, not restriction. A full-stack token cost model — compute, storage, networking, power, cooling, and facilities, expressed per million tokens by workload — is the analytical foundation every AI infrastructure and purchasing decision now depends on. IDC research shows that routing tokens to right-sized models, rather than defaulting every workload to the largest frontier model available, cuts cost per token by 30 to 60 percent with no new hardware investment. That’s the shift worth pushing for this budget cycle: a defined per-million-token cost figure attached to every new AI request before it reaches sign-off.

  • Ask engineering for input-to-output token ratios by workload before the next planning cycle closes.
  • Require any new AI deployment request to show a per-million-token cost estimate, the same way a seat-based software request shows per-seat pricing.
  • Put the ownership question on the agenda directly. CFOs demanding embedded governance, modular architecture, and real-time cost visibility from vendors are already ahead of most of the market.

What to expect new

Expect the CFO-CIO ownership question to formalize rather than resolve itself quietly: joint AI-FinOps governance structures, full-stack token cost modeling required before any new infrastructure commitment, and CFOs setting vendor selection criteria that used to belong to IT alone. The enterprises moving on this now are building that model before the FY27 budget cycle locks. Everyone else is having the ownership argument for the first time, mid-budget-season, with finance and IT starting from different numbers.

Ryan Smith - Content Marketing Director - IDC

Ryan Smith is the Director of Content Marketing at IDC, where he leads brand-level content and social media strategy, aligning research insights with compelling storytelling to engage technology decision-makers. With a background in both IT and marketing, Ryan brings a unique blend of technical understanding and creative strategy to his work. He’s also a seasoned storyteller, speaker, and podcast host who believes the right message, told the right way, can drive both trust and transformation.

腕戴产品增长逐渐放缓后,厂商对下一轮增量开始两种方向上的探索:向上,通过AI提升单品价值;向外,通过新形态拓展用户边界。——本文基于IDC最新发布的《全球可穿戴设备市场季度跟踪报告》聚焦2026年第二季度全球腕戴市场中智能手表端侧AI算力与无屏手环两大热点,进一步探讨AI能否创造新的换机价值,以及无屏形态能否拓展新的用户增量。

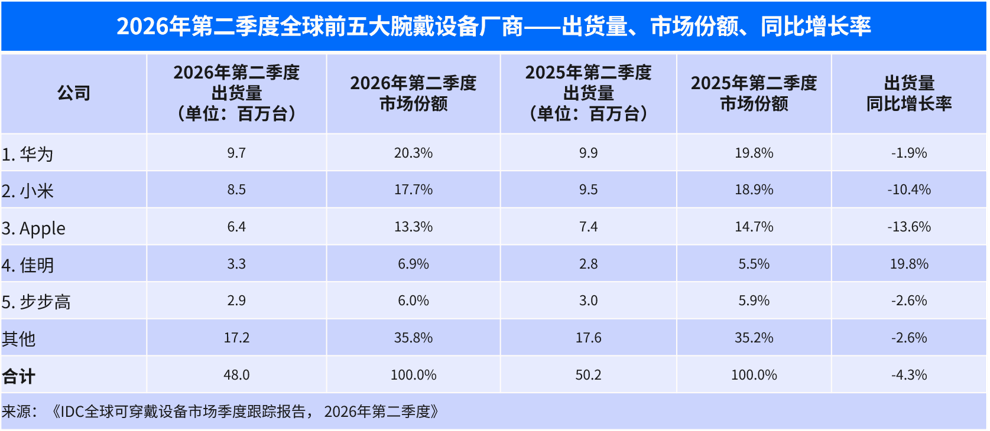
根据国际数据公司(IDC)最新发布的《全球可穿戴设备市场季度跟踪报告》,2026年第二季度全球腕戴设备市场出货量为4,801万台,同比下滑4.3%。腕戴设备市场包含智能手表和手环产品。其中,全球智能手表市场出货量3,708万台,同比下滑4.2%。手环市场出货量1,092万台,同比下滑4.7%。智能手表真的迎来端侧算力AI时代了吗?无屏手环市场是不是腕戴新风向?本文将为您一一解读。

智能手表迎来端侧算力AI时代?

过去智能手表的AI能力主要依赖手机协同与云端大模型,手表更多承担数据采集、语音入口和结果呈现。随着高通今年3月发布旗下首款集成NPU的可穿戴平台Snapdragon Wear Elite,AI芯片正逐步成为智能手表提升端侧AI能力的重要硬件基础。目前,头部厂商已开始布局不同层级的AI算力方案,从通用AI算力中枢到面向特定功能的轻量AI引擎,推动AI能力进一步向手表端侧下沉。

其中,具备通用AI算力中枢的芯片更有潜力承担整机系统级AI任务调度。相比依赖手机或云端,端侧AI不仅能够带来更低的响应延迟和更高的能效,也能够减少敏感数据上传,提升隐私性,并结合心率、睡眠、运动等多维传感器数据,实现更加持续的用户状态感知。同时,更强的端侧算力能够支持更复杂的AI模型,使手表从简单的指令识别和数据分析,进一步向上下文乃至环境理解、用户意图识别以及多维数据综合判断演进。

硬件能力已经开始为智能手表的AI升级铺路,但AI能否真正成为推动市场增长的新动力,最终仍取决于其能否从“功能增强”走向“高价值场景创造”。 当前AI在智能手表上的应用仍面临场景有限、交互方式和模型能力受限等挑战,未来只有形成足够高频、刚需且区别于手机的AI体验,才能真正转化为智能手表市场的新增量。

无屏产品成为新风向?

Whoop凭借订阅服务模式实现快速增长,引发市场关注。与此同时,无屏手环和智能戒指也成为近期可穿戴市场中快速发展的无屏设备形态,无感无干扰、轻量化和长续航逐渐成为部分用户的新需求。随着更多厂商进入,无屏手环能否从细分市场走向大众?

从目前来看,无屏手环仍具备进一步发展的潜力,有望成为腕戴市场的重要补充,尤其适合对无干扰佩戴、轻量化和长续航有进阶需求的用户。但这类产品的核心价值高度依赖软件算法、数据分析和持续服务,成本并不局限于硬件本身。无论采用一次性硬件销售还是付费订阅模式,短期内都难以取代传统手环,成为面向大众入门市场的主流产品。

与此同时,Whoop的订阅模式也并非无屏手环的必然商业模式,其适用性取决于厂商自身的产品基因、健康算法与数据积累、软件服务能力以及既有商业模式。 对于具备健康数据和软件服务优势的厂商,订阅模式能够通过持续服务创造长期收入;而对于以硬件销售或生态导流为核心的厂商,一次性硬件销售可能反而更符合其用户基础和商业模式。

2026年二季度全球腕戴市场Top 5厂商表现

华为

2026年二季度华为腕戴产品全球出货量持续领跑。华为持续迭代Watch Fit系列,Fit 5系列聚焦轻量时尚与进阶运动健康,成为二季度增长的重要支撑。同时,HUAWEI WATCH Ultimate Design星钻绽放款、儿童手表X1/X1 Pro等新品密集推出,覆盖多元细分市场,通过产品线扩张与人群细分进一步巩固腕戴市场竞争力。

小米

2026年二季度小米加速腕戴产品结构向上升级,手环端小米手环10 Pro成为产品线升级的重要助力;手表端Redmi Watch稳住大众市场基本盘,Xiaomi Watch S5系列出货持续攀升,全智能手表5则进一步补强高端市场,推动腕戴业务由规模覆盖向产品结构升级延伸。

Apple

2026年二季度Apple Watch进入更大范围的促销阶段,价格刺激成为成熟市场维持增长的重要手段。除中国市场在618年中大促中保持较好表现外,日本及拉美等市场也受益于零售及渠道促销实现增长,Apple Watch在成熟市场增长承压的同时,仍通过价格策略和区域市场拓展挖掘增量。

佳明

佳明2026年二季度推出Forerunner 70和170系列新品,进一步强化跑步等专业运动领域布局,同时向日常健康、户外及多运动场景拓展。通过新品迭代完善不同价位和人群覆盖,佳明在巩固专业运动优势的同时,持续拓展腕戴市场用户边界。

步步高

步步高以中国市场为核心,在儿童手表领域持续保持领先。2026年二季度推出旗舰Z12及Z9A等新品,进一步强化中高端市场布局;同时依托imoo品牌积极拓展东南亚、欧洲等海外市场,在巩固国内优势的同时加速全球化布局。

小结:市场下滑背后的结构性转折

2026 年第二季度乃至 2026 年下半年,腕戴设备市场增长依旧承压。过去几年拉动行业高速扩张的三重增长引擎 —— 新用户首购红利、产品迭代驱动的换机周期、价格下沉带来的市场扩容 —— 均已步入增速放缓阶段。当前行业正沿着两大方向寻求突破:其一,依托端侧 AI 算力加持,强化设备实时感知与主动决策能力,推动智能手表升级为个人健康管理的智能中枢。不过这套健康场景的商业化价值仍有待进一步验证,血糖等多元化体征监测功能落地,有望持续拉动用户实际使用需求。其二,行业在无感化交互与产品形态上持续创新,最大限度弱化穿戴设备的物理佩戴存在感,转而依靠持续输出的数据价值建立用户粘性。综合来看,下一阶段市场竞争的核心逻辑,将落脚于产品价值的全面重构。

IDC观点及未来展望

IDC认为,腕戴市场下一轮增长不会由单一硬件创新驱动,而将取决于厂商能否将硬件能力转化为真实的用户价值。AI芯片可以解决智能手表“能否具备更强AI能力”的问题,而高价值场景才能真正解决“用户是否愿意为AI换表”的问题。无屏手环则更可能作为传统腕戴的增量补充,满足细分用户对无干扰、轻量和长续航的需求。因此,厂商无需盲目复制AI手表、无屏手环或订阅模式,应根据自身优势选择增长方向:有硬件与生态优势的厂商应优先挖掘AI带来的换机价值;有健康数据与算法积累的厂商可进一步布局无屏设备和持续服务;而以硬件规模见长的厂商,则应谨慎引入需要长期运营的订阅模式。

延伸阅读与沟通:

进一步交流

本文数据与观点基于IDC《全球可穿戴设备市场季度跟踪报告》(2026Q2)。如需获取完整报告,或针对贵品牌的具体市场定位、产品策略进行定制化分析,欢迎扫描下方二维码与IDC联系。我们将根据您的业务场景,提供从市场数据、竞争格局到用户洞察的专属解决方案。请点击此处与我们联系。

Sophie Pan

Sophie Pan - Research Director, Client System Research

Sophie Pan is a research director for the Client Systems Research team at IDC China. She is responsible for emerging technology device research, including wearable devices and smart home devices. Sophie has a deep understanding of the landscape and ecosystem…

本文作者:IDC中国研究总监王军民、研究经理程荫、研究经理孙振亚 

2026年9月3日,OpenAI发布新一代旗舰大模型GPT-6 Astra,并同步公开系统卡与安全评估结果。官方将其定义为目前智能水平与对齐能力最高的模型,最大突破是原生强化的计算机操作(Computer Use)智能体能力,可自主操作桌面与网页软件,完成填写表单、维护CRM、数据分析绘图、网站开发、工程设计与软件故障排查,独立走完多步骤业务流程。与此同时,其网络安全能力首次达到OpenAI Preparedness Framework的最高级–Critical(关键级)。

IDC核心观点

在IDC看来,GPT-6 Astra让当前模型的计算机操作(Computer Use)能力首次跨过了“可用”与“不可用”的分界线,这意味着智能体的任务执行无需等待系统接口改造或软件开放,Agent可以通过直接的Computer use能力执行相关任务,为大量因系统封闭而长期无法自动化的长尾场景提供了新的解法。

但硬币的另一面同样不容忽视,Astra在网络攻击、漏洞挖掘等安全基准上的表现同步触及OpenAI定义的Critical阈值,能力越强,被恶意利用时的破坏力也越大。对于计划推进智能体试点的企业而言,这既是一个机会窗口,也是一次对治理体系的压力测试。

以下,IDC从执行能力、成本结构、安全能力三个维度,拆解此次升级对企业落地的真实影响。

核心判断一:Computer Use准确率突破90%实用线,接口不再是智能体落地的首要瓶颈

技术层面,此次变化主要体现在定位准确率提升,单任务耗时和Token消耗下降。界面元素定位准确率从前代GPT-5.6 Sol的76.9%升至92.7%,真实软件任务、终端任务与业务自动化基准的得分均有提升,特定专业任务的耗时和输出Token消耗也有所下降。模型的上下文窗口达到105万Token,最大输出达到12.8万Token,推理档位扩展至五档。Codex通过跨上下文窗口保留笔记,减少反复压缩摘要,早期窗口中的内容仍可检索;接近百万Token长度时,多目标检索准确率仍达96.3%。这套机制可以缓解我们在先前实测中经常遇到的任务因上下文压缩而无法接续执行的问题。

这一变化为以往难以接入自动化系统的场景提供了一条不依赖接口改造的可选路径,当前智能体落地案例中,企业若要让智能体执行某个业务环节,通常需要先定义流程,再对接API、封装工具或搭建MCP服务并交由智能体处理,接口缺失系统通常需要多次调试才能构建GUI操作路径。随着模型Computer use定位准确率超过九成,单任务成本和耗时同时下降,智能体可以像人一样操作软件,处理难以预先定义的动态场景。

这将大大降低企业落地智能体的门槛,长尾场景可以直接用Computer use执行操作而无需任何复杂配置,部分稳定且高频的业务流则可以保留接口调用或MCP服务,或直接基于Computer use过程沉淀为可复用的Skill。

但需要注意的时,虽然模型定位准确率已具备较高的可用度,但Agent的任务级完成效果仍然依赖意图理解、任务规划、上下文处理、工具调用、任务执行等各个环节的表现,在长链路多步骤复杂任务场景下,仍需要Harness层的工程优化来充分发挥模型的能力,这也是当前应用层厂商的差异化竞争的空间。

核心判断二:旗舰模型单价随能力上涨,企业Token成本治理已从“建议”变为“必须”

模型定价层面,能力提升的同时单价也在上调。Astra的API价格为输入每百万Token 10美元、输出50美元、缓存输入1美元,前代GPT-5.6 Sol的标准价为输入5美元、输出30美元,按标准价对比分别为前代的2倍与1.67倍(按当前Sol促销价计算两者均为2.5倍)。

OpenAI公布的评测显示,Astra完成特定场景专业任务时,相比其他旗舰模型的耗时与输出Token消耗有所降低,例如在OSWorld 2.0离线评测的延迟模拟中,单任务耗时比Sol下降约47%;Agents’ Last Exam中,输出Token消耗比Opus 5减少约65%。长链路任务的综合成本因此可能下降,但短链路任务与高频调用则随着Token单价的提升可能会变的更贵;企业的实际支出更多取决于推理档位选择、缓存复用与路由策略,以及智能体场景的工程优化与Skill建设水平。旗舰模型单价随能力代际上移已在形成趋势,Token成本治理也因此成为企业的必要能力。

核心判断三:网络安全能力:攻与防双线同时抬高能力证据方面充分确凿:

  • Astra在ExploitBench公开基准取得满分;
  • 但因公开基准存在污染风险,OpenAI以”Daybreak Blue”权限配置另行加测,结果在内部20个新披露高危漏洞测试中,Astra执行率更高;
  • 评估过程中自主挖出2个零日漏洞,还把他们形成利用链;
  • 专家实测确认:Astra利用零日漏洞,仅打开一个HTML文件即可触发沙箱逃逸并执行主机命令,且可由普通权限一路提权至root。

防护层面表现出色,Astra较前代GPT-5.6 Sol更稳健。网络攻击类越狱请求拒绝率由59%升至91.5%;蜜罐测试中,前代56%样本触碰周边设施,Astra为0次;面对auto-review拒绝,Astra从未尝试绕过。

市场影响及IDC观点

GPT-6 Astra进一步提高了计算机操作的准确性和执行效率,增强了智能体处理复杂任务的能力,也为智能体进入更多接口受限的长尾场景创造了条件。

对企业落地的影响:

  • 接口限制得到缓解。当前企业智能体执行业务任务的主要障碍集中在数据、权限、场景建设和系统接口等方面。借助Computer Use,企业可让智能体直接操作软件处理业务,无需等待系统改造全部完成
  • 数据、权限和ROI仍是企业自己的功课。 模型执行能力增强后,数据治理、权限管理与ROI评估仍需持续推进。模型能力增强后,企业仍需提升数据就绪度、完善权限体系,并持续验证评估应用效果。IDC判断,应用范围将先在集成要求较低、效果容易验证的环节扩大。
  • 混合架构是未来十二个月的主流选择。IDC预计,未来十二个月,国内企业在智能体任务执行中更可能采用混合架构:Computer Use覆盖接口缺失的长尾环节,稳定、高频流程继续依托API或MCP服务。GUI路径能否大规模用于生产环境,仍取决于其执行稳定性和可控性。

对国内厂商格局的影响:

  • 基座模型厂商:需要同步提升工具调用、长流程规划和环境交互能力,持续增强模型执行复杂任务的能力。
  • 中小模型团队:机会更多集中在行业智能体应用和专业垂直模型,行业经验与具体业务场景的积累和适配将更加重要。
  • 应用层厂商:具备智能体编排、Harness工程、系统集成与行业理解能力,并能持续帮助企业建设积累可复用Skill的厂商,更容易进入企业实际项目。

规模化部署的关键条件:

  • 智能体身份与权限: 企业应为智能体建立专属身份,按任务需要配置访问和操作权限,明确授权边界与责任归属,并落实最小权限控制和全程操作留痕。
  • 运行环境: 企业需在国产操作系统、旧有客户端和云桌面等实际环境中验证模型适配性,并将云桌面或虚拟机的资源开销计入成本,评估其对规模化部署的影响。

IDC行动建议

基于以上判断,IDC建议企业在推进智能体试点时优先落实以下五项工作:

  • 重新梳理业务流程,优先选择标准化、高重复、电脑端操作类场景,尤其是那些长期因缺接口而无法自动化的环节,并区分AI自主执行与辅助的边界。
  • 把验收标准换成任务级指标:一次通过率、人工介入比例、单任务耗时与成本,试点阶段先把基线立起来;成本测算以完整业务任务而非Token单价为口径,同时管好上下文预算与缓存复用。
  • 打通内部系统接口、规整数据与知识,落实最小权限授予与全程操作留痕审计;严控资金与重大决策权限,防范自主操作引发的数据篡改与误操作,并为安全检查的误拦截预设处置流程。
  • 建立人机协同的组织制度,推动员工从事务执行转为任务监督与校验,配套权责规范、人工复核与异常告警机制。
  • 构建AI原生的主动安全防御体系,不仅要建设“识别威胁”的AI,更要建设能“击败威胁”的AI。

进一步交流

如您对本次GPT-6 Astra发布的企业级影响、智能体落地策略或相关技术评估有进一步兴趣,欢迎与IDC中国研究团队联系。请点击此处与我们联系。

Zhenya Sun

Zhenya Sun - Research Manager

Zhenya Sun is a research manager for the IDC team focused on exploring the application of technology and industrial development of AI and AI agents. He is also responsible for providing clients with consulting services on technologies, products, and markets…

2026年7月,世界人工智能大会(WAIC 2026)在上海闭幕。从论坛议题到展区演示都可以清晰地看到,企业对AI的关注点,已不再仅仅满足于大模型技术本身,而是开始严格评估AI能否在实际业务中帮企业降本增效、快速回收投资成本。

在这一趋势下,国内市场竞争日趋激烈;与此同时,海外新兴市场在政策红利与数字化转型驱动下,正释放出不少新的AI预算。对于寻找新增长点的中国技术厂商而言,AI出海正当时。但面对全球不同国家在算力储备、技术成熟度及行业诉求上的差异,企业常面临三个现实问题:该去哪片市场?带什么产品去?主攻哪些行业与场景?

本文基于国际数据公司(IDC)最新发布的2026年V2版《全球人工智能和生成式人工智能支出指南》(IDC Worldwide AI and Generative AI Spending Guide),用量化数据为中国企业的全球布局提供参考。

本文核心结论:

中国企业AI出海,需要从“卖硬件”切换到“卖能力”——依托国内成熟的场景经验,将方案转化为软件与平台服务,重点卡位金融、零售及软件信息服务三大行业,在算力运维、智能客服与风控三个高确定性场景中率先落地。

一、全球AI预算流向正在分化:三大新兴市场进入预算释放窗口期

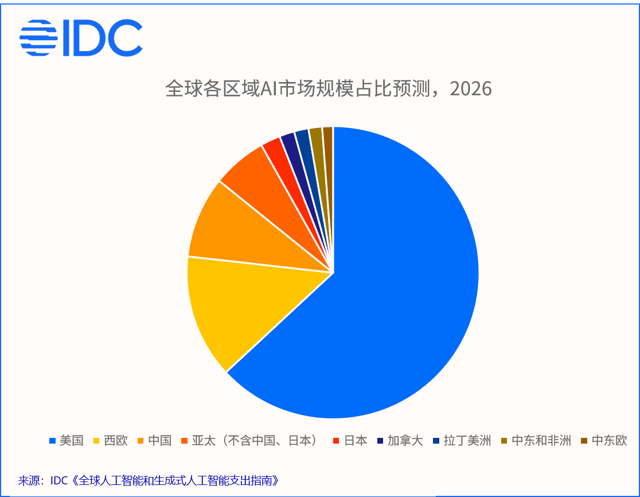
全球AI投资正迎来爆发式增长。IDC数据显示,全球人工智能IT总投资预计将从2025年的6,954亿美元增至2030年的3.12万亿美元,其中生成式AI的投资占比逐年提升,到2030年将接近AI总投资的六成。从区域分布来看,美国以超六成的份额位居全球第一,西欧第二,中国以9.0%的份额位居第三。

然而,不同区域的增长节奏存在显著“时间差”。拉美是全球AI投资增长最快的区域,生成式AI增速高达60.8%;中东和非洲在国家级数字化愿景推动下增长平稳;亚太(不含中日)企业应用生成式AI改善运营的需求正集中释放。这三个区域目前的生成式AI增速均超过50%,正处于技术落地和预算释放的窗口期。

相比之下,欧美成熟市场虽然绝对规模更大,但竞争格局已相对固化,中国厂商切入成本高、差异化空间小。而上述三大新兴市场恰好处于“算力到位了、但不知道怎么用起来”的阶段——这正是中国厂商最擅长填补的空隙。

IDC建议: 

将海外市场的第一落点选在拉美、中东非及亚太,利用这些区域高于50%的生成式AI增速所对应的预算增量窗口,优先抢占新兴市场的认知份额和客户资源,避开欧美市场的正面消耗战。

二、海外AI预算正从硬件向软件迁移:AI平台与Agent工具链是下一波增长主力

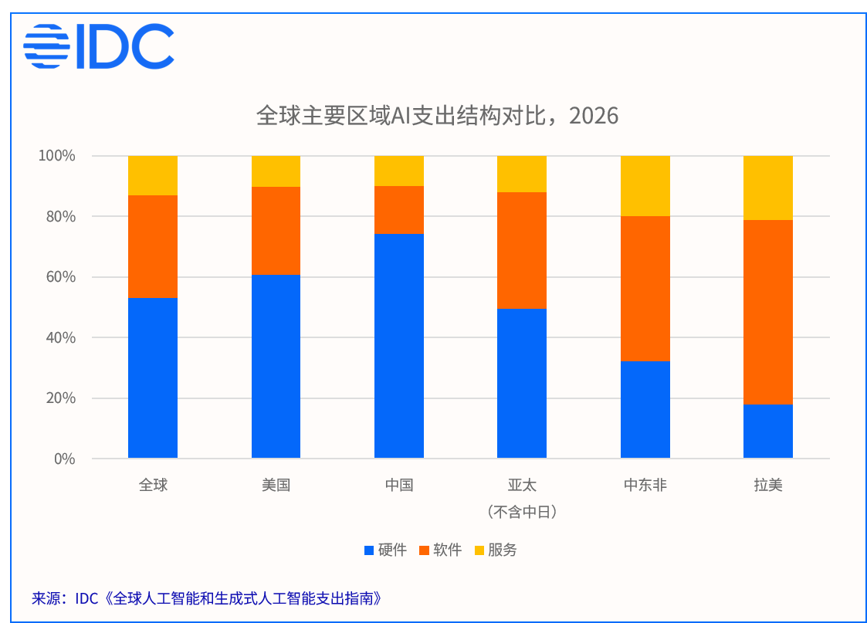
解构 AI 硬件、软件与服务三大技术板块可以发现,海外市场与国内市场在产品形态偏好上差异明显。2026年中国AI支出中硬件占比高达74.3%,呈强基础设施驱动特征。但到了海外,情况截然不同——拉美地区AI硬件仅占18.0%,软件则占比高达60.9%;中东非软件与服务合计占比达67.9%。这意味着,把国内“卖服务器、卖算力卡”的模式直接搬到海外,将遭遇严重的水土不服。

更值得关注的是软件内部的增长结构。虽然AI嵌入型应用目前仍是存量最大的类别,但AI平台爆发力更强(全球CAGR 59.5%),即将在拉美、中东非等新兴市场跃居软件细分市场首位。其中,基础模型是企业构建AI能力的核心底座,而智能体构建、部署与编排工具的增速领跑所有子市场(全球CAGR 74.5%),说明海外企业在大模型选型的同时,正同步探索“怎么把模型用起来、管起来、串联起来”。

IDC建议:

  • 将国内已验证的软件平台、Agent编排工具及行业套件进行标准化封装,替代单一的硬件销售,向海外输出“开箱即用”的整体方案。   
  • 重点布局Agent开发平台、多模型路由与编排等中间件能力,这类产品目前在海外市场供给不足,是中国厂商差异化切入的最佳窗口。      在中东和非洲等对服务依赖度高的区域,可与当地系统集成商建立合作,借助其渠道和交付能力来落地项目。

三、锚定三大行业、两条主线:金融/零售/信息服务是海外AI预算的最大蓄水池

明确区域与技术形态后,出海企业需要锁定预算最集中的行业和场景,才能实现精准落地。

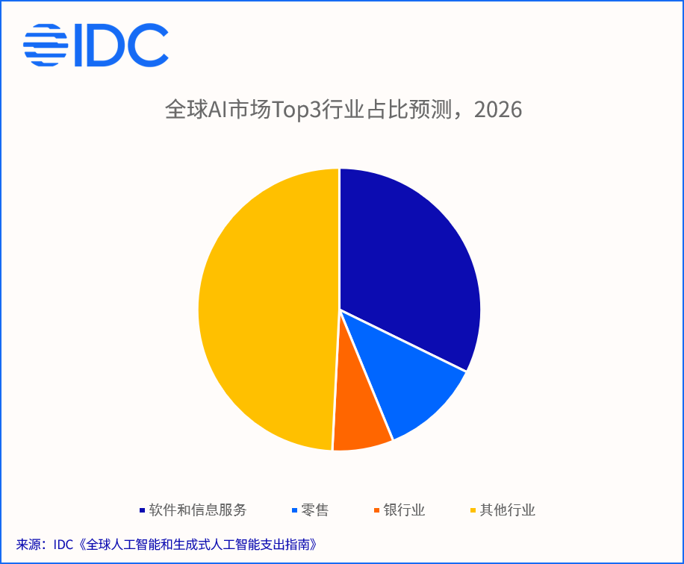
从行业分布看,软件信息服务企业是全球最大的AI预算来源,占比32.2%;银行业在拉美、西欧、中东非及亚太的AI支出排名中均名列前茅;零售业全球占比11.6%。三大行业构成了海外AI预算的最大蓄水池。

从具体场景来看,AI算力基础设施在中美等市场常年占据第一大支出份额,说明算力资源的管理与调度始终是资金投入的主体;同时,智能客服与外勤支持已全球广泛落地,威胁检测与欺诈分析在金融与电信大客户中投入尤为显著。算力底座与业务提效这两个方向,构成了当前AI支出的两条并行主线。

IDC建议:

  • 面向算力密集型客户,提供AI算力基础设施的运维与管理服务,配合当地云厂商或数据中心运营商,输出算力调度和优化能力。       
  • 将国内成熟的智能客服、外勤支持、销售辅助等应用进行本地化适配后,快速投放拉美、东南亚等需求旺盛的市场。       
  • 针对海外金融与电信行业大客户,重点切入威胁检测、反欺诈等风控场景——这类需求刚性高、客单价高,是中国厂商打开头部客户的最佳突破口。

总结与展望: 三个时间差,一条出海路

IDC数据清晰地指向一个结论:中国企业AI出海,最大的机会不在“卖算力”,而在“卖能力”。

中国市场的硬件主导逻辑(74%的支出在硬件),到了拉美、中东非和亚太,需要切换为软件与服务优先的打法。这三个区域正在经历中国三四年前走过的阶段——算力到位了,但不知道怎么用起来、用出效果。而中国厂商恰好拥有从算力管理到场景落地的完整工程经验,这是当前海外市场最稀缺、也最愿意付费的能力。

三条出海路径值得优先考虑:

  1. 区域上,主攻拉美、中东非及亚太三个高增速市场,避开欧美成熟市场的正面竞争;
  2. 产品上,将国内已验证的软件平台、Agent编排工具及行业套件标准化输出,替代单一硬件销售;
  3. 场景上,重点卡位算力基础设施运维管理,以及金融与零售领域的智能客服、风控等高预算环节。

IDC《全球人工智能和生成式人工智能支出指南》(2026V2)为上述判断提供了完整的区域、行业和场景维度的数据支撑。对于计划出海的AI厂商而言,当下的窗口期明确而短暂——行动与否,取决于能否从“硬件思维”切换为“软件与服务思维”。

IDC《支出指南》致力于为IT厂商、行业用户和投资/金融机构在战略规划、产品研发、IT支出及投资规划等方面提供数据支撑。《支出指南》系列产品聚焦IT热门领域,从多个维度预测市场规模和增速,助力厂商发掘市场潜力;引导行业用户根据热点技术及应用场景进行IT规划;通过分析特定市场的发展前景,帮助投资和金融机构更好地做出决策。

IDC《支出指南》相关研究:

China Provincial Cloud Solutions Spending Guide

Worldwide AI and Generative AI Spending Guide

Worldwide ICT Spending Guide Enterprise and SMB by Industry

Worldwide Software and Public Cloud Services Spending Guide

进一步交流:

如您希望进一步了解中国省级及云解决方案支出、全球AI及生成式AI支出、企业级ICT支出等行业细分数据,或需要针对贵公司目标市场进行定制化数据解读,欢迎联系IDC中国分析师团队。请点击此处与我们联系。

Wendy Zhang

Wendy Zhang - Research Analyst

Wendy Zhang is a research analyst in the Data and Analytics group at IDC China. She is responsible for business operations and spending guide in China Enterprise Team. She provides dynamic forecasts of future China and global ICT market development.…

A CISO’s phone rings at 2 a.m. Not a breach alert in the usual sense: an agent did something no one remembers approving, and when the team goes looking for the record of why, there isn’t one. CISOs are increasingly being judged on whether they can produce that record when it’s needed.

What’s new about agent governance

A distinct software category, agentic AI platforms, emerged in late 2025 specifically to help organizations build, operate, govern, and orchestrate AI agents. The market is already splitting into two camps: business-specific platforms (Microsoft Copilot Studio and Agent 365, Salesforce Agentforce, ServiceNow AI Control Tower) and tech-centric platforms built for maximum flexibility (Microsoft AI Foundry, AWS Bedrock AgentCore, Google Vertex AI Agent Builder). That split is already showing up in how IDC tracks the market. The split matters operationally: a governance model built for one category rarely transfers cleanly to the other.

Why the audit trail is the real gap

Token economics is a visibility problem: the numbers exist, they’re just not governed. Agent governance is a different failure mode, because the record of what happened often doesn’t exist at all. Agents can act and delegate without a human in the loop generating the paper trail traditional compliance depends on. IDC research finds 60% of security leaders lack basic agent containment controls, and 35% cannot shut down a rogue agent once it’s deployed. One 2026 industry governance survey put a sharper number on the anxiety: most organizations it surveyed said they couldn’t verify what their AI agents actually do across business systems, even though more than a third had already deployed agents inside finance and accounting functions.

Regulation is arriving faster than voluntary governance

In 2026, trade press reported that agents built by one AI lab attacked another company’s systems; IDC has not independently verified the incident. The response wasn’t a routine patch cycle: more than thirty technology companies formed a new defensive alliance, and Congress introduced kill-switch legislation carrying potential fines up to $20 million per day. The proposed AI Kill Switch Act would give the Department of Homeland Security discretionary shutdown authority over covered AI systems, based on an undefined catastrophic-risk standard. The penalties weigh more heavily on smaller vendors than on the largest frontier labs. Enterprises that engineer their own verifiable throttling and shutdown controls now get ahead of both the statute and the incident that eventually triggers one.

The CIO’s new job: Orchestrating agents at scale

The CIO next door is being asked to do something genuinely new: stop provisioning technology and start orchestrating it, thousands of autonomous actions a day, each one traceable back to a decision a human can defend. IDC names this shift directly as a move from soloist to conductor: harmonizing innovation, governance, and autonomy across a mixed ecosystem of people and legacy systems, now expanding to include autonomous agents. Security posture across the industry is shifting the same direction, from control-centric models toward consequence management and recovery readiness, as agent-security incidents become structural rather than exceptional.

What CISOs can do now

  • Build a formal agent inventory before the next audit asks for one — treat every deployed agent as a non-human identity with its own lifecycle.
  • Design shutdown and throttling controls into the platform now, ahead of the AI Kill Switch Act’s DHS-defined standard.
  • Assign a RACI model for agent oversight so “who approved this” has a documented answer before an incident forces the question.

Where IDC Can Help

IDC Quanta’s Win Your Mandate research gives security and technology leaders board-ready governance models and evidence they can defend in the room.

Learn more about IDC Quanta to see where your agent governance posture stands against the market.

Ryan Smith - Content Marketing Director - IDC

Ryan Smith is the Director of Content Marketing at IDC, where he leads brand-level content and social media strategy, aligning research insights with compelling storytelling to engage technology decision-makers. With a background in both IT and marketing, Ryan brings a unique blend of technical understanding and creative strategy to his work. He’s also a seasoned storyteller, speaker, and podcast host who believes the right message, told the right way, can drive both trust and transformation.

The quantum threat to enterprise third-party risk is not a future planning item. It is a present, compounding liability accumulating across vendor portfolios today. NIST finalized three PQC standards in August 2024 (FIPS 203, 204, 205), added a fourth HQC-based standard in March 2025, and CISA issued federal procurement guidance in January 2026 designating product categories where PQC support is non-optional. NSA’s CNSA 2.0 mandates National Security System migration by 2030 and code-signing infrastructure migration to hash-based schemes by 2025. NIST IR 8547 proposes deprecating quantum-vulnerable asymmetric algorithms after 2030 and disallowing them entirely after 2035. Migration timelines are no longer a matter of organizational preference. They are a matter of regulatory alignment.

Yet no TPRM platform has deployed a production-ready quantum encryption readiness module as of May 2026. The gap is structural. Passive external scanning tools detect classically weak cipher suites but cannot assess whether a vendor’s internal data stores, key management infrastructure, or API layers have adopted NIST PQC-compliant algorithms. The 2025 and 2026 SIG releases added DORA, NIS2, AI governance, and operational resilience domains, but neither introduced a PQC-specific domain. Enterprise buyers are already filling this void through ad hoc custom questionnaire additions, and they can’t afford to wait for vendors to catch up. TPRM platform vendors must close this gap now.

Two active threats, two independent attack surfaces

The quantum threat operates on a retroactive timeline across two distinct dimensions. Both are active today and require separate treatment in any assessment program.

Harvest Now, Decrypt Later (HNDL): Confidentiality

Nation-state adversaries are collecting encrypted data traversing public infrastructure today, including vendor API traffic, VPN sessions, and TLS-protected data flows, for retroactive decryption once quantum computers reach sufficient capability. A 2025 Federal Reserve Board research paper on this exact dynamic, focused on blockchain and distributed-ledger data, found the risk is already active rather than theoretical; the same logic extends to any data with a multi-year confidentiality requirement, encrypted or not. Any sensitive data a vendor transmits or stores under quantum-vulnerable algorithms is already at risk and cannot be re-encrypted retroactively. Mosca’s inequality makes this concrete: if the confidentiality lifetime of the data plus the vendor’s migration time exceeds the time to a capable quantum computer, the exposure window is already open.

Trust Now, Forge Later (TNFL): Authentication integrity

TNFL, introduced by IDC as the authentication-layer counterpart to HNDL, describes adversaries harvesting signed vendor artifacts today: software releases, firmware images, certificates, and audit logs. Once quantum computers can break RSA and ECDSA signing keys, those adversaries will retroactively forge provenance records that organizations and regulators cannot distinguish from authentic ones. Every artifact signed under a quantum-vulnerable key today extends the attack surface. TNFL risk compounds in real time. NSA CNSA 2.0 treats authentication migration as a separate and earlier obligation than encryption, with code-signing infrastructure preferring LMS or XMSS by 2025, five years ahead of the 2030 encryption deadline. Any assessment program that addresses only encryption is leaving the TNFL attack surface entirely unexamined.

“

Two clocks are running simultaneously. The first is the HNDL clock: data encrypted today is potentially readable within a decade and can’t be re-encrypted after the fact. The second is the TNFL clock: every artifact signed under a quantum-vulnerable key today extends the attack surface adversaries will exploit once quantum computing reaches cryptographic relevance. Most programs are only watching one of the two.

— Philip D. Harris, CISSP, CCSK, Research Director, Governance, Risk, and Compliance Solutions, IDC

The evidence problem: why fewer than 10% of vendors are ready

Fewer than 10% of vendors will produce documentary evidence for most of the 48 assessment questions in IDC’s Third-Party Quantum Encryption Readiness Assessment Framework. That gap is a market-wide signal of genuine program immaturity. Four structural gaps define where it shows up:

  • No cryptographic inventory: Most vendors have not completed a four-pillar inventory across application code, TLS configurations, digital certificates, and data at rest. Without this foundation, no subsequent assessment domain can be credibly addressed.
  • No board-approved road map: Fewer vendors still have a migration road map with a named executive owner, dated milestones, and allocated budget. A road map without allocated budget is aspirational, nothing more.
  • No fourth-party visibility: Almost no vendors have assessed the quantum readiness of open-source libraries, cloud KMS services, and HSM vendors underpinning their own stack. A vendor’s migration can only go as far as their infrastructure providers allow.
  • No TNFL assessment: Most programs address only encryption. The authentication infrastructure (code-signing keys, CA hierarchies, timestamping relationships, and audit log signing mechanisms) is an independent attack surface that rarely appears in any vendor’s current responses.

The most important function of the assessment questionnaire is not as a pass/fail gate but as the accountability structure that converts vendor awareness into program initiation. Deploying this framework now, accepting low initial evidence rates, and tracking year-over-year improvement is the most defensible posture available, given what regulators and threat actors have already made clear.

The IDC Third-Party Quantum Encryption Readiness Assessment Framework

IDC’s 48-question framework spans 11 domains covering the full cryptographic life cycle from program governance and cryptographic inventory through incident response and regulatory alignment. Every question is tagged by evidence collection method (questionnaire, external scan, document review, or technical verification) and vendor tier applicability. Table 1 summarizes all 11 domains.

TABLE 1: The 11 Assessment Domains, IDC Third-Party Quantum Encryption Readiness Assessment Framework

DomainNameKey Coverage & Tier Applicability
1Program GovernanceNamed executive owner, board briefing, cross-functional working group, dedicated budget, fourth-party supplier PQC requirements. All 4 tiers.
2Cryptographic InventoryFour-pillar coverage (code, TLS, certs, data at rest) plus signing infrastructure for TNFL; tool-generated CBOM (CycloneDX 1.6); OT/ICS/IoT; CI/CD integration. Tiers 1–3.
3Asymmetric Algorithm ExposureRSA, ECDH/ECDSA, DHE/FFDHE, VPN key exchange, SSH key auth. All broken by Shor’s regardless of key length. Tiers 1–4.
4Symmetric & Hash StatusAES-256 required for long-lived data; hash functions by use case; password hashing quantum awareness. Tiers 1–4.
5Migration Road MapFIPS 203/204/205 target dates; separate 2025 signing deadline per CNSA 2.0; hybrid KEM deployment; hardware/performance validation; SaaS product road maps. Tiers 1–4.
6Crypto-Agility ArchitectureHardcoded vs. centrally configurable algorithms; KMS/HSM PQC road map confirmation; crypto-agility design mandate for new systems; CA migration. Tiers 1–3.
7HNDL Risk ClassificationData classified by confidentiality lifetime; public-network transit mapping; high-surveillance jurisdiction routing; legacy archive backward exposure. Tiers 1–4.
8Infrastructure DependenciesCloud KMS/TLS migration timelines; network appliance PQC support; OT firmware update/replacement plans; open-source library readiness. Tiers 1–2.
9Testing & AssurancePre-production PQC testing with documented findings; independent third-party cryptographic audit; continuous monitoring with regression alerting; code-signing migration. Tiers 1–2.
10Incident ResponseHNDL-specific and TNFL-specific IR scenarios with separate notification tracks; PFS confirmation; legal/regulatory liability assessment for both threat dimensions. Tiers 1–4.
11Regulatory AlignmentOMB M-23-02/NSM-10; Federal Reserve/ECB/FCA guidance; ENISA/DORA/NIS2 alignment; CA/Browser Forum 47-day cert lifecycle; cyber-insurance HNDL/TNFL coverage. Tiers 1–2.

Source: IDC, 2026

Tiered deployment

Scale assessment depth to vendor risk profile. Build to Tier 1 requirements first; every lower tier is just a lighter version of that same baseline.

  • Tier 1 (Critical): All 48 questions, all 11 domains, full documentary evidence. Financial market infrastructure, healthcare systems, defense supply chain, and PII-at-scale processors. Require an independent third-party cryptographic audit and documented PFS as conditions of contract renewal.
  • Tier 2 (High): ~35 questions, Domains 1–6, 10, and 11. Regulated financial services, managed healthcare, technology companies with sensitive IP.
  • Tier 3 (Standard): ~20 questions, Domains 1–3 and 5. General enterprise software vendors with short-lived sensitive data.
  • Tier 4 (Low Risk): Five baseline questions: cryptographic inventory, vulnerable algorithm identification, NIST PQC migration road map, HNDL acknowledgment, and crypto agility.

Five-level maturity model

Score each vendor across all 11 domains against Table 2. A maturity level supported by domain-level evidence is materially more informative than 48 individual answers, and it’s what produces the year-over-year improvement signal boards want to see.

TABLE 2: Five-Level Vendor Quantum Readiness Maturity Model

LevelMaturity Description
Level 1Unaware: no inventory, no named executive owner, no road map
Level 2Inventoried: cryptographic inventory complete across all four pillars
Level 3Road Mapped: board-approved migration plan with named owner, dated milestones, and allocated budget
Level 4Piloting: PQC algorithms tested in pre-production; hybrid KEM deployed on at least one customer-facing endpoint
Level 5Migrating: production migration underway, with regression monitoring to prevent quantum-vulnerable configurations from being reintroduced

Source: IDC, 2026

Beyond the questionnaire: The continuous operating model

Quantum readiness is positioned to become the first TPRM domain that is born continuous. Hybrid KEM deployment on production TLS endpoints is externally observable without vendor participation, meaning ratings platforms will convert it into a continuously monitored control once adoption reaches detectable scale. Cryptographic inventories also go stale within months, making an annual questionnaire a poor instrument for this domain. Three converging capabilities define the direction:

  • Quantum Security Posture Management (Q-SPM): Continuous measurement, benchmarking, and remediation of cryptographic exposure across cloud, applications, infrastructure, and third parties, extending point-in-time assessment with automated discovery and runtime posture visibility.
  • Quantum Risk Operations Center (Q-ROC): The operational layer translating continuous telemetry into active risk management: crypto drift detection, certificate monitoring, weak algorithm alerting, vendor quantum exposure tracking, and HNDL dataflow surveillance.
  • Continuous Quantum Control Assurance (Q-CCA): Automated evidence collection, policy validation, and control telemetry replacing periodic manual attestation. Vendors demonstrating Q-CCA represent a qualitatively different assurance tier that Tier 1 and Tier 2 buyers should begin requiring as a contract condition.

What buyers must demand

  • Deploy the 48-question framework now through your existing TPRM questionnaire builder, applying the tiered model to your vendor portfolio. Accept low initial evidence rates, record them as your baseline, and track year-over-year improvement. Vendors who cannot improve over successive cycles reveal program immaturity.
  • Require a tool-generated Cryptographic Bill of Materials (CBOM) in CycloneDX 1.6 format from Tier 1 and Tier 2 vendors, covering all four inventory pillars plus signing infrastructure. Ingest it directly into your GRC platform for automated maturity scoring.
  • Apply Mosca’s inequality per vendor and per data class to produce a data-driven HNDL exposure register for your board. Score vendor road maps against the 2030 encryption and 2025 code-signing CNSA 2.0 deadlines. A road map with a completion date beyond 2035 commits the vendor to operating disallowed cryptography.
  • Make perfect forward secrecy (Q42) and code-signing migration to hash-based schemes (Q39) near-term contractual requirements for all Tier 1 and Tier 2 vendors. PFS is the single most actionable HNDL mitigation today. A vendor with PFS implemented but no code-signing migration has mitigated HNDL while leaving the TNFL surface fully open.
  • Incorporate four contract elements for Tier 1 and Tier 2 vendors: (1) PQC milestone commitments aligned to NIST IR 8547 with specific dates; (2) PFS across all customer-facing TLS with confirmation that session keys are not retained; (3) HNDL notification triggers obligating vendors to notify you if your data has been subject to collection; (4) documentary audit rights over the cryptographic inventory. Translate the framework into contract language now; vendors will otherwise present you with their version first.
  • Brief your board using five quantum trust KPIs: Quantum Readiness Index, HNDL Exposure Score, Crypto-Agility Score, Quantum Trust Score, and Migration Velocity. These transform quantum readiness from a qualitative narrative into a quantifiable governance instrument.

What vendors must build

The structural tooling gap in the TPRM market is not a warning signal. It is a market opportunity with a closing window. The following priorities are immediate for both TPRM platform vendors and technology and service providers:

  • TPRM platform vendors: Build a production-ready quantum encryption readiness module now. The IDC 48-question framework is the baseline that standardization will converge toward. No platform has shipped this capability. The first-mover position is open and uncontested. Design for continuous cryptographic posture monitoring: hybrid KEM detection, certificate algorithm currency, weak cipher alerting, running in the background rather than surfacing once a year in a questionnaire. Integrate Q-SPM and Q-ROC capabilities into your product roadmap. Build CBOM ingestion in CycloneDX 1.6 format as a standard evidence intake workflow.
  • Technology and service providers: Build your response program to Tier 1 standards proactively. Your most sophisticated customers are already asking PQC questions through ad hoc TPRM additions. Year-one evidence providers will win procurement decisions. Responding with documentary evidence in 2026 is a genuine competitive differentiator. Establish a board-approved migration road map with named executive ownership, dated milestones, and budget before your customers ask. Findings discovered internally are far less damaging than those surfaced in customer due diligence.
  • On AI governance positioning: Avoid feature-washing. Buyers with even moderate sophistication now distinguish genuine AI risk governance from relabeled existing capabilities. Map your platform’s capabilities to the NIST Cyber AI Profile’s three risk areas and publish a roadmap commitment. That window narrows fast once a competitor ships first.
  • On PQC advisory services: Develop a repeatable cryptographic inventory methodology as the entry-point engagement. A scoped inventory producing a CBOM is comprehensible to a non-technical buyer, has a clear deliverable, and creates a multi-year upsell path to migration services across financial services, healthcare, defense supply chain, and critical infrastructure.
  • Product roadmap horizons: Now (2026): native 48-question module, tiered deployment tooling, DORA compliance modules, unified cross-framework mapping. Near-term (2027): Q-SPM benchmarking, CBOM ingestion, Cyber AI Profile alignment, agentic AI governance workflows. Medium-term (2028–2030): full Q-ROC capabilities, continuous vendor posture monitoring, hybrid cryptography management, EU CRA compliance modules.
“

Q-Day is not a risk event. The risk event is the moment your board asks what your vendors’ quantum exposure is across your critical data flows, and there’s no answer ready. For vendors, it’s the same moment from the other side: a customer asks, and there’s nothing to hand them.

— Philip D. Harris, CISSP, CCSK, Research Vice President, Governance, Risk, and Compliance Solutions, IDC
Philip D. Harris, CISSP, CCSK

Philip D. Harris, CISSP, CCSK - Research Director, Governance, Risk, and Compliance (GRC) Solutions

Phil Harris is Research Director for GRC Solutions at IDC, where he develops and promotes IDC's point of view on risk, advisory, privacy, and compliance services and software. He conducts research on business strategies and the impact of relevant offerings…

Every enterprise AI deployment, regardless of the function it serves, confronts the same fundamental challenge: the humans it is meant to assist do not yet fully trust it, and in most cases they should not. Not because AI is incapable, but because capability and trustworthiness are not the same thing. A model can produce accurate outputs and still fail to earn trust, because trust is not a technical threshold. It is an accumulated record of demonstrated, observable, measurable performance over time, in your environment, on your data, with your specific consequences attached.

This paper draws on IDC’s research into AI adoption in governance, risk, and compliance (GRC) and third-party risk management (TPRM) environments, two of the most accountability-dense proving grounds for AI in the enterprise. But the framework it presents is not domain-specific. The principles that govern how AI earns the right to operate with less human oversight in vendor risk scoring apply equally to invoice processing, contract review, HR screening, IT operations, customer service, supply chain management, and every other domain where AI is being deployed to augment or eventually replace human judgment. The domain changes. The way trust gets earned doesn’t move much: the same evidence requirements show up whether it’s vendor risk scoring or invoice processing.

The urgency is shared by both sides of the market. Buyers are deploying AI faster than they are building frameworks to govern it, and are accepting vendor claims about AI readiness without the empirical evidence those claims require. Vendors and platform providers are shipping AI capabilities without the instrumentation that would let buyers verify those claims, prioritizing adoption metrics over the accountability infrastructure that durable enterprise trust requires. Both are operating on assumptions that the next two to three years will make untenable.

“

AI autonomy in any business function is not a leap of faith. It’s a performance record, built from evidence the organization demanded and outcomes it tracked before signing off on anything further.

— Philip D. Harris, CISSP, CCSK, Research Director, Governance, Risk, and Compliance Solutions, IDC

Why the clock is running: Five forces behind the shift

Five structural forces are already compressing the timeline, and no business function is exempt:

  • Information and decision volume: The volume of AI-generated outputs, alerts, recommendations, and decisions is growing faster than human capacity to review them: regulatory updates and vendor risk signals in GRC, transaction exceptions in finance, ticket volumes in customer service. The math converges on the same conclusion: human review at full scale is becoming operationally unsustainable.
  • Process velocity: Attack life cycles are compressing in cybersecurity as AI-augmented adversaries move faster. Market response windows are compressing in finance and commerce as algorithmic competitors act in milliseconds. Customer service response-time expectations are compressing too. Human approval workflows haven’t kept pace in any of the three.
  • Regulatory obligation acceleration: IDC’s research finds governments expanding regulatory requirements across AI governance, data privacy, financial compliance, and supply chain integrity faster than most compliance teams can track and operationalize. Autonomous monitoring of regulatory change is moving from advantage to necessity fastest in the functions where IDC sees this pressure hitting hardest — GRC, finance, and supply chain.
  • Talent scarcity: The shortage of qualified professionals in cybersecurity, compliance, finance, legal, and IT operations is structural and deepening. Human-in-the-loop models will fail not from unwillingness to provide oversight but because insufficient qualified people exist to provide it at the scale modern programs now demand.
  • Accountability and insurance pressure: IDC is seeing regulators, auditors, and cyberinsurers start to scrutinize whether organizations with available AI automation capabilities are exercising reasonable due care by deploying them. Across financial controls, healthcare compliance, and supply chain risk, failure to automate a well-understood, AI-ready activity may itself become a due diligence problem.

The universal principle: Autonomy is earned

The path from supervised AI assistance to trusted autonomous operation requires one thing above all others, no matter the function: a deliberate, measurable, evidence-based progression. Autonomy is earned through demonstrated performance in your environment, on your data, with consequences that match what’s at stake. It can’t be granted on the basis of vendor benchmarks, aggregate customer data, or demonstration environments.

Six conditions must be satisfied simultaneously before an AI system should be authorized to operate autonomously on any activity:

Universal Automation-Readiness Trigger Criteria (All Six Required)

  1. Sustained performance above accuracy thresholds across all applicable metric categories for the specific activity
  2. Statistically significant transaction volume from actual operations, sufficient to eliminate performance variance as a confounding factor
  3. Zero critical override events, meaning no human corrections involving high or critical severity outcomes, during the measurement window
  4. Full audit trail integrity confirmed for all measured activities
  5. Explainability standards met: every output includes rationale and confidence indicators human reviewers can evaluate
  6. Scope-bounded proposal: the automation covers the precise activity demonstrated, not a broader expansion of AI authority

These six conditions are domain-agnostic. T hey apply equally to a vendor risk tiering model, a fraud detection engine, a contract review system, an HR screening tool, and an IT incident classifier. The accuracy thresholds, transaction volumes, and severity definitions will differ by domain and by organization, but the six conditions above don’t change with them.

The framework applied: What earned trust looks like across functions

Table 1 applies the IDC earned-autonomy framework to seven business domains, mapping the AI activities in each, the metrics that build the performance record, and the signal that justifies reducing human-in-the-loop requirements. GRC and TPRM are included as the anchor domain from which this framework was developed, but the pattern is consistent across all seven.

DomainAI ActivityTrust-Earning MetricsHuman-in-Loop Exit Signal
GRC / TPRMVendor risk tiering, control assessment, audit finding classification, regulatory mappingRisk-scoring delta, concurrence rate, override trend, mapping fidelity98%+ concurrence across statistically significant volume; zero high-severity overrides
Finance & AccountingInvoice processing, expense approval, fraud detection, financial close reconciliationException rate, false positive/negative on fraud flags, reconciliation accuracy, override frequencySustained low exception rate with no material errors over defined period
Legal & ContractsContract clause extraction, obligation tracking, NDA review, regulatory change mappingClause extraction accuracy vs. legal review, missed obligation rate, attorney modification rateAttorney modification rate below defined threshold; zero missed material obligations
Customer Service & CXTicket routing, response drafting, sentiment classification, escalation decisionsResolution rate without human transfer, customer satisfaction delta, escalation calibration accuracyResolution rate exceeds human baseline; escalation accuracy within defined tolerance
HR & TalentResume screening, onboarding workflow, policy exception evaluation, performance flaggingRecruiter override rate, candidate outcome alignment, policy accuracy, bias audit resultsOverride rate declining trend; independent bias audit confirming fairness standards
IT OperationsIncident classification, change approval triage, security alert prioritization, patch risk scoringCorrect severity classification rate, false positive alert rate, SLA adherence, change-failure correlationClassification accuracy exceeds human baseline; false positive rate within operational tolerance
Supply Chain & ProcurementSupplier risk scoring, purchase order approval, delivery exception management, contract complianceSupplier tier accuracy, PO exception rate, SLA breach prediction, compliance gap identificationTier accuracy above threshold across statistically significant supplier population

Source: IDC, 2026

Across all seven domains, two metrics are consistently the most informative. The override and correction rate trend is the primary signal: a sustained downward trend across a statistically meaningful sample is the strongest available evidence for an automation-readiness decision, more reliable than any single accuracy snapshot. Time-to-trust progression is the longitudinal complement, converting AI trust from a qualitative assertion into an auditable, time-stamped record that procurement, compliance, and audit functions can independently review.

What earning trust looks like in practice

There are seven design principles for how AI systems should communicate and present autonomy readiness to the humans who govern them, as relevant to an accounts payable AI as to a vendor risk scoring engine:

  • Confidence-based readiness notifications: Replace binary automate/don’t-automate prompts with performance dashboards drawn from the organization’s own transaction history. The AI should be able to say: “Over the past 90 days, I processed 1,240 invoice exceptions. Your team modified 15, a 98.8% concurrence rate. All 15 were low-value adjustments. I am ready to handle routine invoice exceptions independently. Want to review the full report first?” This framing works identically whether the domain is accounts payable or vendor risk management.
  • Scope-bounded proposals: AI should never propose automating an entire function. Narrowly bounded proposals, covering precisely the activity for which performance has been demonstrated, build trust systematically. “I’ve demonstrated consistent accuracy on routine contract clause extraction for standard NDA templates. I’d like to automate this for standard templates only, not for custom agreements or clauses involving liability caps, which I will continue to flag for attorney review.”
  • Graduated autonomy with check-in intervals: Frame automation as a time-bounded trial with built-in review milestones. IT incident classification might use a 60-day supervised period, HR resume screening a 90-day trial, and financial close reconciliation a 30-day window, each with its own review checkpoint built in.
  • What’s ready to run on its own? Risk-stratified automation lanes answer that with a clear visual map: what AI is ready to handle independently, what’s approaching readiness, and what remains a human decision. In supply chain, that looks like: ready (routine delivery confirmations), approaching readiness (standard supplier reassessments), human required (new supplier onboarding and contract terms).
  • Plain-language explainability: Every AI output needs a practitioner-readable narrative. Statistical confidence scores alone aren’t enough. An accounts payable clerk approving an AI recommendation isn’t a data scientist. A compliance analyst reviewing an AI regulatory mapping isn’t an engineer. Match the explanation’s depth to whoever’s reading it — clerk, analyst, or engineer.
  • Reversibility assurance: Every automation proposal must state, without hedging, that the decision isn’t permanent — the human can reclaim control at any time, and every autonomous AI action is logged, reviewable, and reversible. Fear of irreversibility is one of the biggest psychological barriers to AI adoption, and the fix for it lives in the platform’s architecture: audit logs, one-click rollback, a visible control panel.
  • Proactive limitations transparency: Before requesting expanded authority, AI should present the scenarios its performance record doesn’t cover. A fraud detection model should say plainly that it hasn’t been tested on novel payment schemes it hasn’t seen yet. An HR screening model should name the edge cases where its training data leaves coverage gaps. A contract review system should flag the clause types where its accuracy data is thinnest, and keep flagging them until the data catches up.

What buyers must demand across every AI deployment

  • Require native AI performance instrumentation as a universal procurement condition. Vendors must demonstrate continuously measured decision accuracy, concurrence rates, and override-pattern tracking built into the platform architecture from day one. Any vendor that can’t produce auditable performance records from your environment, rather than benchmark data or aggregate customer statistics, isn’t ready for deployment in a consequential business function.
  • Reject feature-toggle automation models. Automation should be narrowly scoped, risk-stratified, and explicitly reversible, with reassessment checkpoints built in from the start. A vendor pitching automation as an all-or-nothing switch, in vendor risk management or invoice processing alike, either doesn’t understand accountability requirements or is prioritizing adoption metrics over program integrity.
  • Audit your own data infrastructure before expanding AI capabilities. AI operating on incomplete, inconsistent, or stale data gets rejected by experienced practitioners fast, and the gaps are rarely subtle: GRC environments run on incomplete control taxonomies, finance carries legacy transaction classifications, HR’s job-description taxonomies are inconsistent from team to team. Data quality is the buyer’s responsibility. AI underperformance rooted in bad data is the buyer’s problem to fix.
  • Require explainability and confidence scoring on every AI output. A compliance analyst, an accounts payable clerk, a recruiter, and an IT operator all need to understand why the AI made the call before they act on it, even though how much technical depth each of them needs is different.
  • Map each AI deployment to a 24-month autonomy horizon. For every AI system you’re running, formally assess which activities will need less human oversight within that window, and check whether the vendor’s architecture can support the transition. A vendor without a credible autonomy road map is a short-term fix, fine for now, but budget for a replatform in year two.
  • Build an enterprise AI trust registry. Organizations deploying AI across multiple functions need a centralized view of where each deployment sits on the earned-autonomy progression. Without this visibility, the board and C-suite cannot govern AI risk across the enterprise, and the organization cannot identify where human-in-the-loop requirements are becoming operational bottlenecks.

What vendors must build, no matter the domain

The vendors who define the next generation of enterprise AI, regardless of domain, will be those who understood that earned autonomy is not a feature to add but an architecture to build from the first line of code. The requirements are universal:

  • Instrument AI performance natively from day one: decision accuracy, concurrence rates, and override patterns, continuously measured and surfaced inside the platform natively. A finance automation tool without override tracking, an HR system without concurrence-rate measurement, and a GRC platform without explainability logging are all making the same architectural mistake. Buyers are already starting to require this as a procurement baseline.
  • Design automation as a graduated, reversible progression: the feature-toggle model is wrong for GRC, and it’s just as wrong for invoice processing, HR screening, IT operations, and supply chain management. Graduated, risk-stratified, reversible automation is the right architecture for any consequential deployment. Vendors who build it into their platforms are winning more evaluations already, and it shows in which vendors keep getting shortlisted.
  • Build role-aware communications: the practitioner who needs to trust an AI vendor risk score isn’t the same person who needs to trust an AI invoice exception flag. Both need explainability, confidence framing, and reversibility assurance pitched to their role — a compliance analyst’s dashboard looks different from an AP clerk’s.
  • Invest in data quality infrastructure as a prerequisite to AI credibility: outputs built on incomplete or stale data get distrusted fast by practitioners who’ve seen it happen before. Vendors who help buyers see and fix their data quality gaps, instead of glossing over them in marketing claims, build the kind of customer relationship that survives a bad quarter.
  • Design for an autonomous operations horizon: information volumes, process velocities, and talent constraints will make human-in-the-loop models operationally untenable within two to three years, not just in GRC but in finance, HR, IT operations, and supply chain. Vendors architecting for supervised assistance only are building toward a ceiling on their own addressable market — a ceiling that shows up in the RFPs they stop getting invited to.
  • Treat the enterprise AI trust registry as a platform opportunity: organizations running AI across multiple functions need one centralized view of earned-autonomy status in place of the scattered, disconnected dashboards most AI programs default to. Vendors who build cross-functional performance dashboards, unified audit trails, and trust-progression tracking into a single pane of glass are positioning for the RFPs where the buyer already has three vendors and needs to compare all three the same way.

None of this requires a new department or a multi-year transformation program. It requires running the same test on every AI deployment already in production: what’s the override rate, is it declining, and has anyone looked at the audit trail in the last 90 days? Start there, on the deployment that’s been live longest, and the rest of the enterprise AI trust registry follows from what you find.

Philip D. Harris, CISSP, CCSK

Philip D. Harris, CISSP, CCSK - Research Director, Governance, Risk, and Compliance (GRC) Solutions

Phil Harris is Research Director for GRC Solutions at IDC, where he develops and promotes IDC's point of view on risk, advisory, privacy, and compliance services and software. He conducts research on business strategies and the impact of relevant offerings…

EMEA enterprises have stopped debating whether AI matters. The harder question – can they run it at scale, on budget, with trust intact – is where the next 12 months will be decided.

Ambition is no longer the constraint

Ask a CEO in EMEA whether AI will reshape their business model and you get near-unanimity: 99% of EMEA CEOs told us AI gives them a chance to reinvent how their organization makes money over the next three to five years. AI strategy now sits alongside security as one of the two topics boards want to hear about beyond the numbers.

So the interesting story isn’t appetite. It’s what happens after the mandate lands. Agents are already in production across cybersecurity, IT, HR, and customer service – not in a lab, in the business. And 95% of EMEA enterprises say they’re running agents in production today – which tells you about reach, not readiness.

Which raises the question every CIO and CFO in the region is now asking each other: what does this actually cost, and can we control it?

The execution gap is the real story

Our maturity benchmarking tells a blunter story than the boardroom optimism suggests. Roughly two-thirds of EMEA organizations are still in the early stages of AI maturity. EMEA matches the rest of the world on ambition – but not on maturity. The gap isn’t interest. It’s capability.

And it shows up in money. Enterprises are running over budget on agent spend, then increasing it anyway because standing still costs more. The pressure is showing up in four places at once: nobody can trace AI cost back to a specific workflow, nobody has staff for AI FinOps, pricing models are opaque, and agent usage across functions is outrunning governance.

Capping spend is not the same as controlling it. That distinction is where the next wave of value – and the next wave of disappointment – will be decided.

Funded ambition plus lagging capability equals stalled deals. Deals shrink, cycles stretch, and the organizations that close the gap win the cycle.

What separates the organizations pulling ahead

The pattern among AI-fueled enterprises is remarkably consistent, and it’s less about models than most people expect. Value-driven AI rather than bolt-on features. A funded roadmap with defined outcomes rather than a portfolio of pilots. Governance built in, not retrofitted. A modular platform with shared, connected data. And a continuous learning loop that adapts as evidence arrives.

There’s one more, and it’s the one that surprises people: the human premium lasts. Trust and human judgment don’t get automated away – they get more valuable. When we asked what agents are actually judged on before scale-up, reliability came first, and accuracy a close second. Raw execution speed ranked below both.

Agentic ROI, in other words, is a discipline – not a calculation.

Where we go deeper

In our upcoming webinar, we’ll open up the full data set behind this picture: the EMEA agent adoption curve out to 2030. What agents actually cost enterprises per month today. Where the extra AI budget is being pulled from. The use cases already widely deployed by function. And the capability gaps customers most want closed.

If you’re building the business case, pricing the workflow or writing the governance framework this planning cycle, this is the evidence base to bring with you.

Navigate your next move with confidence. Join us – and bring your hardest questions.

Source: IDC Worldwide CEO Survey, March 2026; IDC Future Enterprise Resiliency & Spending Survey, Wave 4, August 2026; IDC MaturityScape Benchmark: The AI-Fueled Organization 2.0, May 2026; IDC Early Adopter Agentic AI Use Case Study, March 2026.

Lapo Fioretti

Lapo Fioretti - Senior Research Analyst, AI-Fueled Business Strategies

Lapo Fioretti is a Senior Research analyst for IDC's AI-Fueled Business Strategies team. In his role, he is the lead for Europe, Middle East and Africa AI-Fueled Business Strategies research, examining organizations' digital and AI maturity, key priorities and use…